CVE-Statistik: Dezember 2025
- 05. Januar 2026
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im Dezember 2025 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
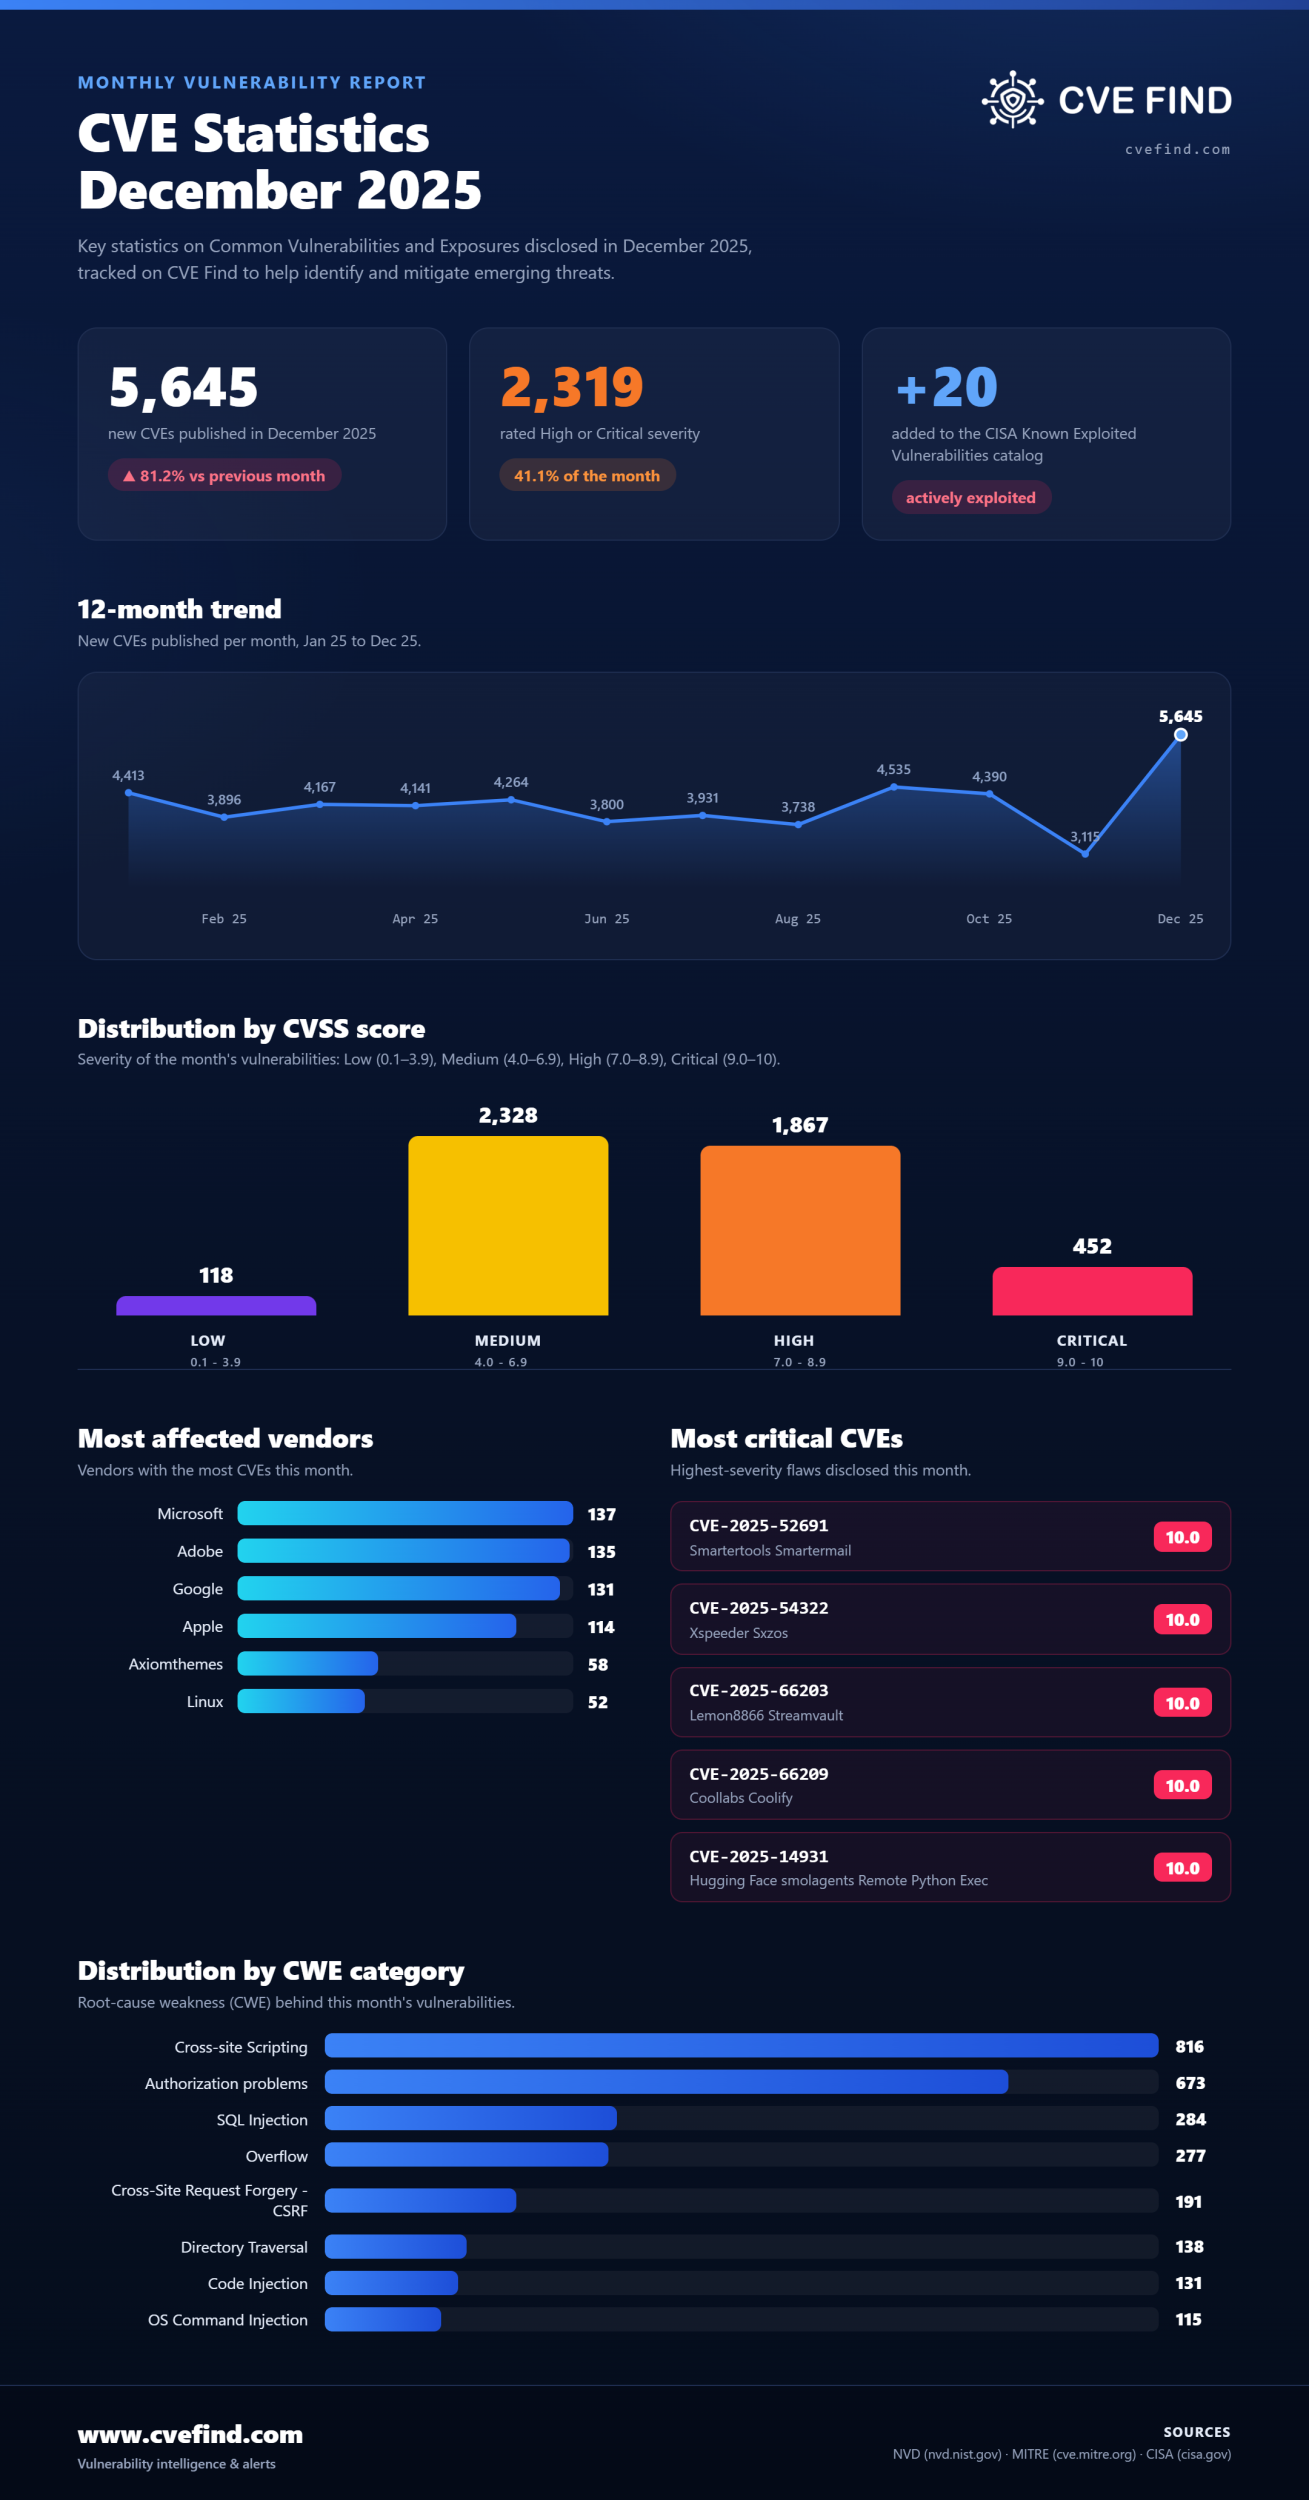
- Gesamtzahl der veröffentlichten CVEs : 5,645 (+81.2% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 20
📂 Verteilung nach Hauptkategorien
- Cross-site Scripting : 816
- Authorization problems : 673
- SQL Injection : 284
- Overflow : 277
- Cross-Site Request Forgery - CSRF : 191
- Directory Traversal : 138
📈 Verteilung nach CVSS-Score
- Low : 118
- Medium : 2328
- High : 1867
- Critical : 452
🏢 Am stärksten betroffene Hersteller
- microsoft : 137
- adobe : 135
- google : 131
- apple : 114
- axiomthemes : 58
📦 Am stärksten betroffene Produkte
- adobe experience_manager : 115
- google android : 111
- apple macos : 110
- microsoft windows : 72
- linux linux_kernel : 52
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2025-52691 (10 CRITICAL) : Successful exploitation of the vulnerability could allow an unauthenticated attacker to upload arbitrary files to any location on the mail server, potentially enabling remote co...
- CVE-2025-54322 (10 CRITICAL) : Xspeeder SXZOS through 2025-12-26 allows root remote code execution via base64-encoded Python code in the chkid parameter to vLogin.py. The title and oIP parameters are also used.
- CVE-2025-66203 (10 CRITICAL) : StreamVault is a video download integration solution. Prior to version 251126, a Remote Code Execution (RCE) vulnerability exists in the stream-vault application (SpiritApplicat...
- CVE-2025-66209 (10 CRITICAL) : Coolify is an open-source and self-hostable tool for managing servers, applications, and databases. Prior to version 4.0.0-beta.451, an authenticated command injection vulnerabi...
- CVE-2025-14931 (10 CRITICAL) : Hugging Face smolagents Remote Python Executor Deserialization of Untrusted Data Remote Code Execution Vulnerability. This vulnerability allows remote attackers to execute arbit...
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
