CVE-Statistik: Januar 2026
- 02. Februar 2026
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im Januar 2026 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
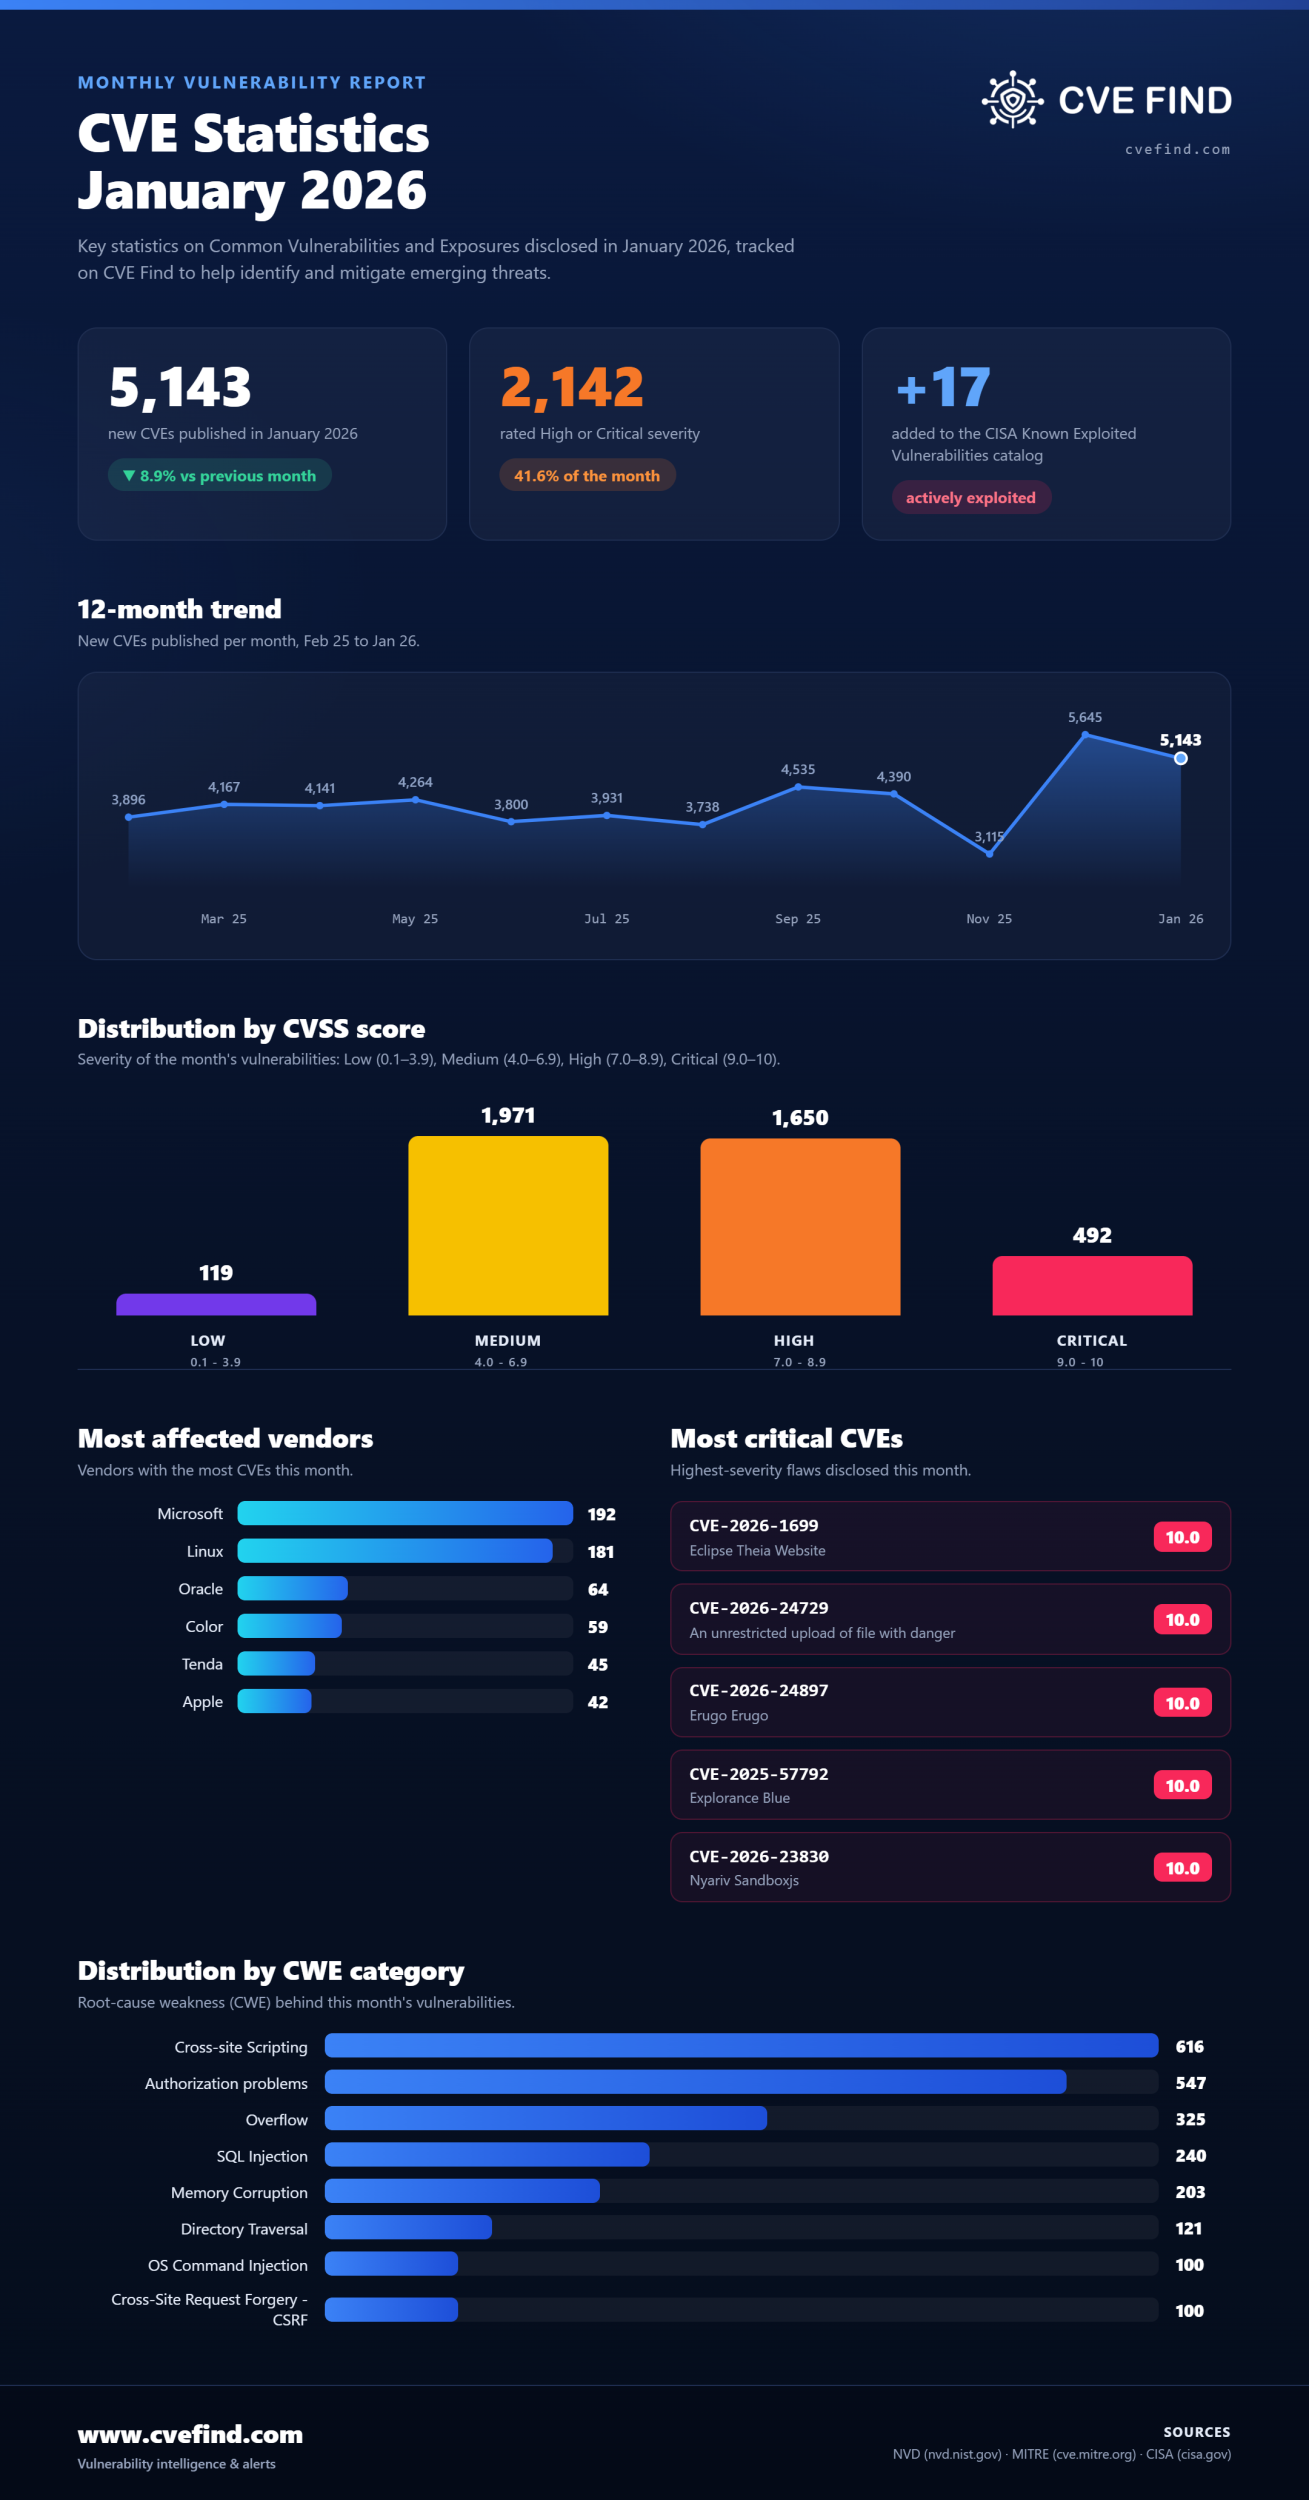
- Gesamtzahl der veröffentlichten CVEs : 5,143 (-8.9% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 17
📂 Verteilung nach Hauptkategorien
- Cross-site Scripting : 616
- Authorization problems : 547
- Overflow : 325
- SQL Injection : 240
- Memory Corruption : 203
- Directory Traversal : 121
📈 Verteilung nach CVSS-Score
- Low : 119
- Medium : 1971
- High : 1650
- Critical : 492
🏢 Am stärksten betroffene Hersteller
📦 Am stärksten betroffene Produkte
- linux linux_kernel : 181
- microsoft windows_11_25h2 : 83
- microsoft windows_server_2025 : 83
- microsoft windows_11_24h2 : 83
- microsoft windows_11_23h2 : 77
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2026-1699 (10 CRITICAL) : In the Eclipse Theia Website repository, the GitHub Actions workflow .github/workflows/preview.yml used pull_request_target trigger while checking out and executing untrusted pu...
- CVE-2026-24729 (10 CRITICAL) : An unrestricted upload of file with dangerous type vulnerability in the file upload function of Interinfo DreamMaker versions before 2025/10/22 allows remote attackers to execut...
- CVE-2026-24897 (10 CRITICAL) : Erugo is a self-hosted file-sharing platform. In versions up to and including 0.2.14, an authenticated low-privileged user can upload arbitrary files to any specified location d...
- CVE-2025-57792 (10 CRITICAL) : Explorance Blue versions prior to 8.14.9 contain a SQL injection vulnerability caused by insufficient validation of user input in a web application endpoint. An attacker can sup...
- CVE-2026-23830 (10 CRITICAL) : SandboxJS is a JavaScript sandboxing library. Versions prior to 0.8.26 have a sandbox escape vulnerability due to `AsyncFunction` not being isolated in `SandboxFunction`. The li...
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
