CVE-Statistik: Juli 2026
- 03. August 2026
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im Juli 2026 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
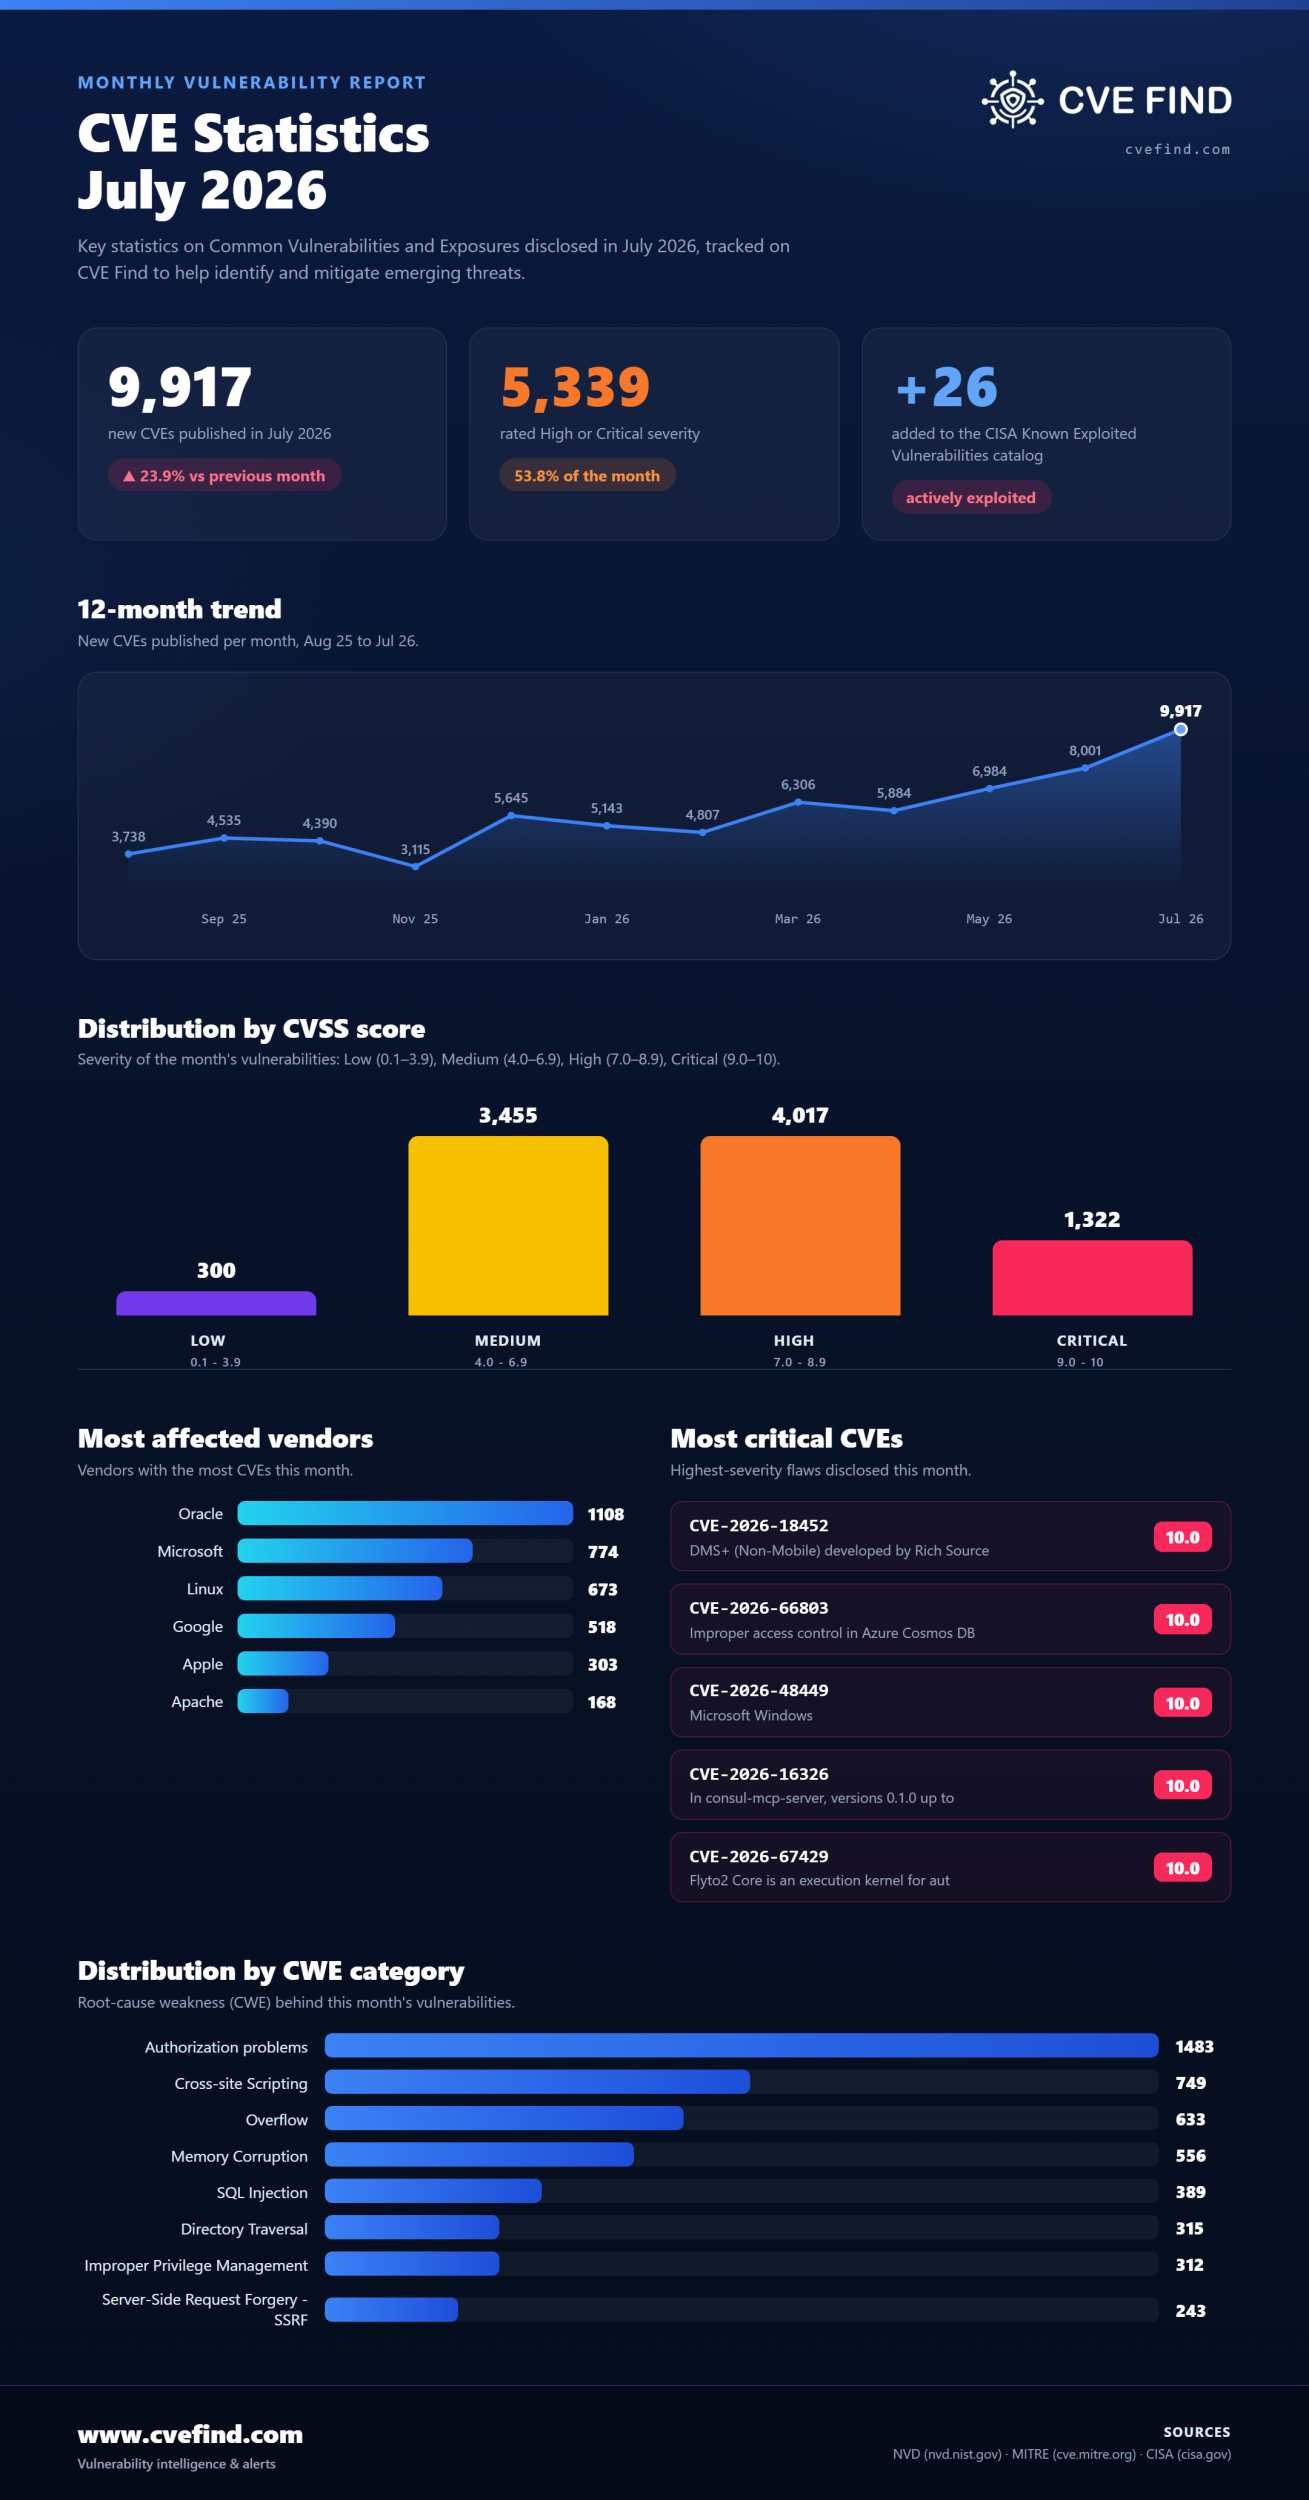
- Gesamtzahl der veröffentlichten CVEs : 9,917 (+23.9% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 26
📂 Verteilung nach Hauptkategorien
- Authorization problems : 1483
- Cross-site Scripting : 749
- Overflow : 633
- Memory Corruption : 556
- SQL Injection : 389
- Directory Traversal : 315
📈 Verteilung nach CVSS-Score
- Low : 300
- Medium : 3455
- High : 4017
- Critical : 1322
🏢 Am stärksten betroffene Hersteller
📦 Am stärksten betroffene Produkte
- linux linux_kernel : 673
- google chrome : 485
- microsoft windows_11_26h1 : 395
- microsoft windows_11_25h2 : 392
- microsoft windows_11_24h2 : 392
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2026-18452 (10 CRITICAL) : DMS+ (Non-Mobile) developed by Rich Source has a Use of Hard-coded Credentials vulnerability. Unauthenticated remote attackers can exploit a fixed API key to gain control over a...
- CVE-2026-66803 (10 CRITICAL) : Improper access control in Azure Cosmos DB allows an unauthorized attacker to execute code over a network.
- CVE-2026-48449 (10 CRITICAL) : Adobe Campaign Classic (ACC) is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in the context of the current user. Exploitati...
- CVE-2026-16326 (10 CRITICAL) : In consul-mcp-server, versions 0.1.0 up to 0.1.3 did not properly isolate session state in stateless mode, which may allow one client's Consul authentication token to be used fo...
- CVE-2026-67429 (10 CRITICAL) : Flyto2 Core is an execution kernel for automation and AI-agent workflows. Prior to 2.26.6, image.download and related file-writing modules use caller-controlled output_dir inste...
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
