Statistiques CVE : octobre 2025
- 01 novembre 2025
- Temps de lecture: 3 min min
🌐 Découvrez les chiffres clés des vulnérabilités publiées en octobre 2025 sur CVE Find.
🔎 Vue d'ensemble
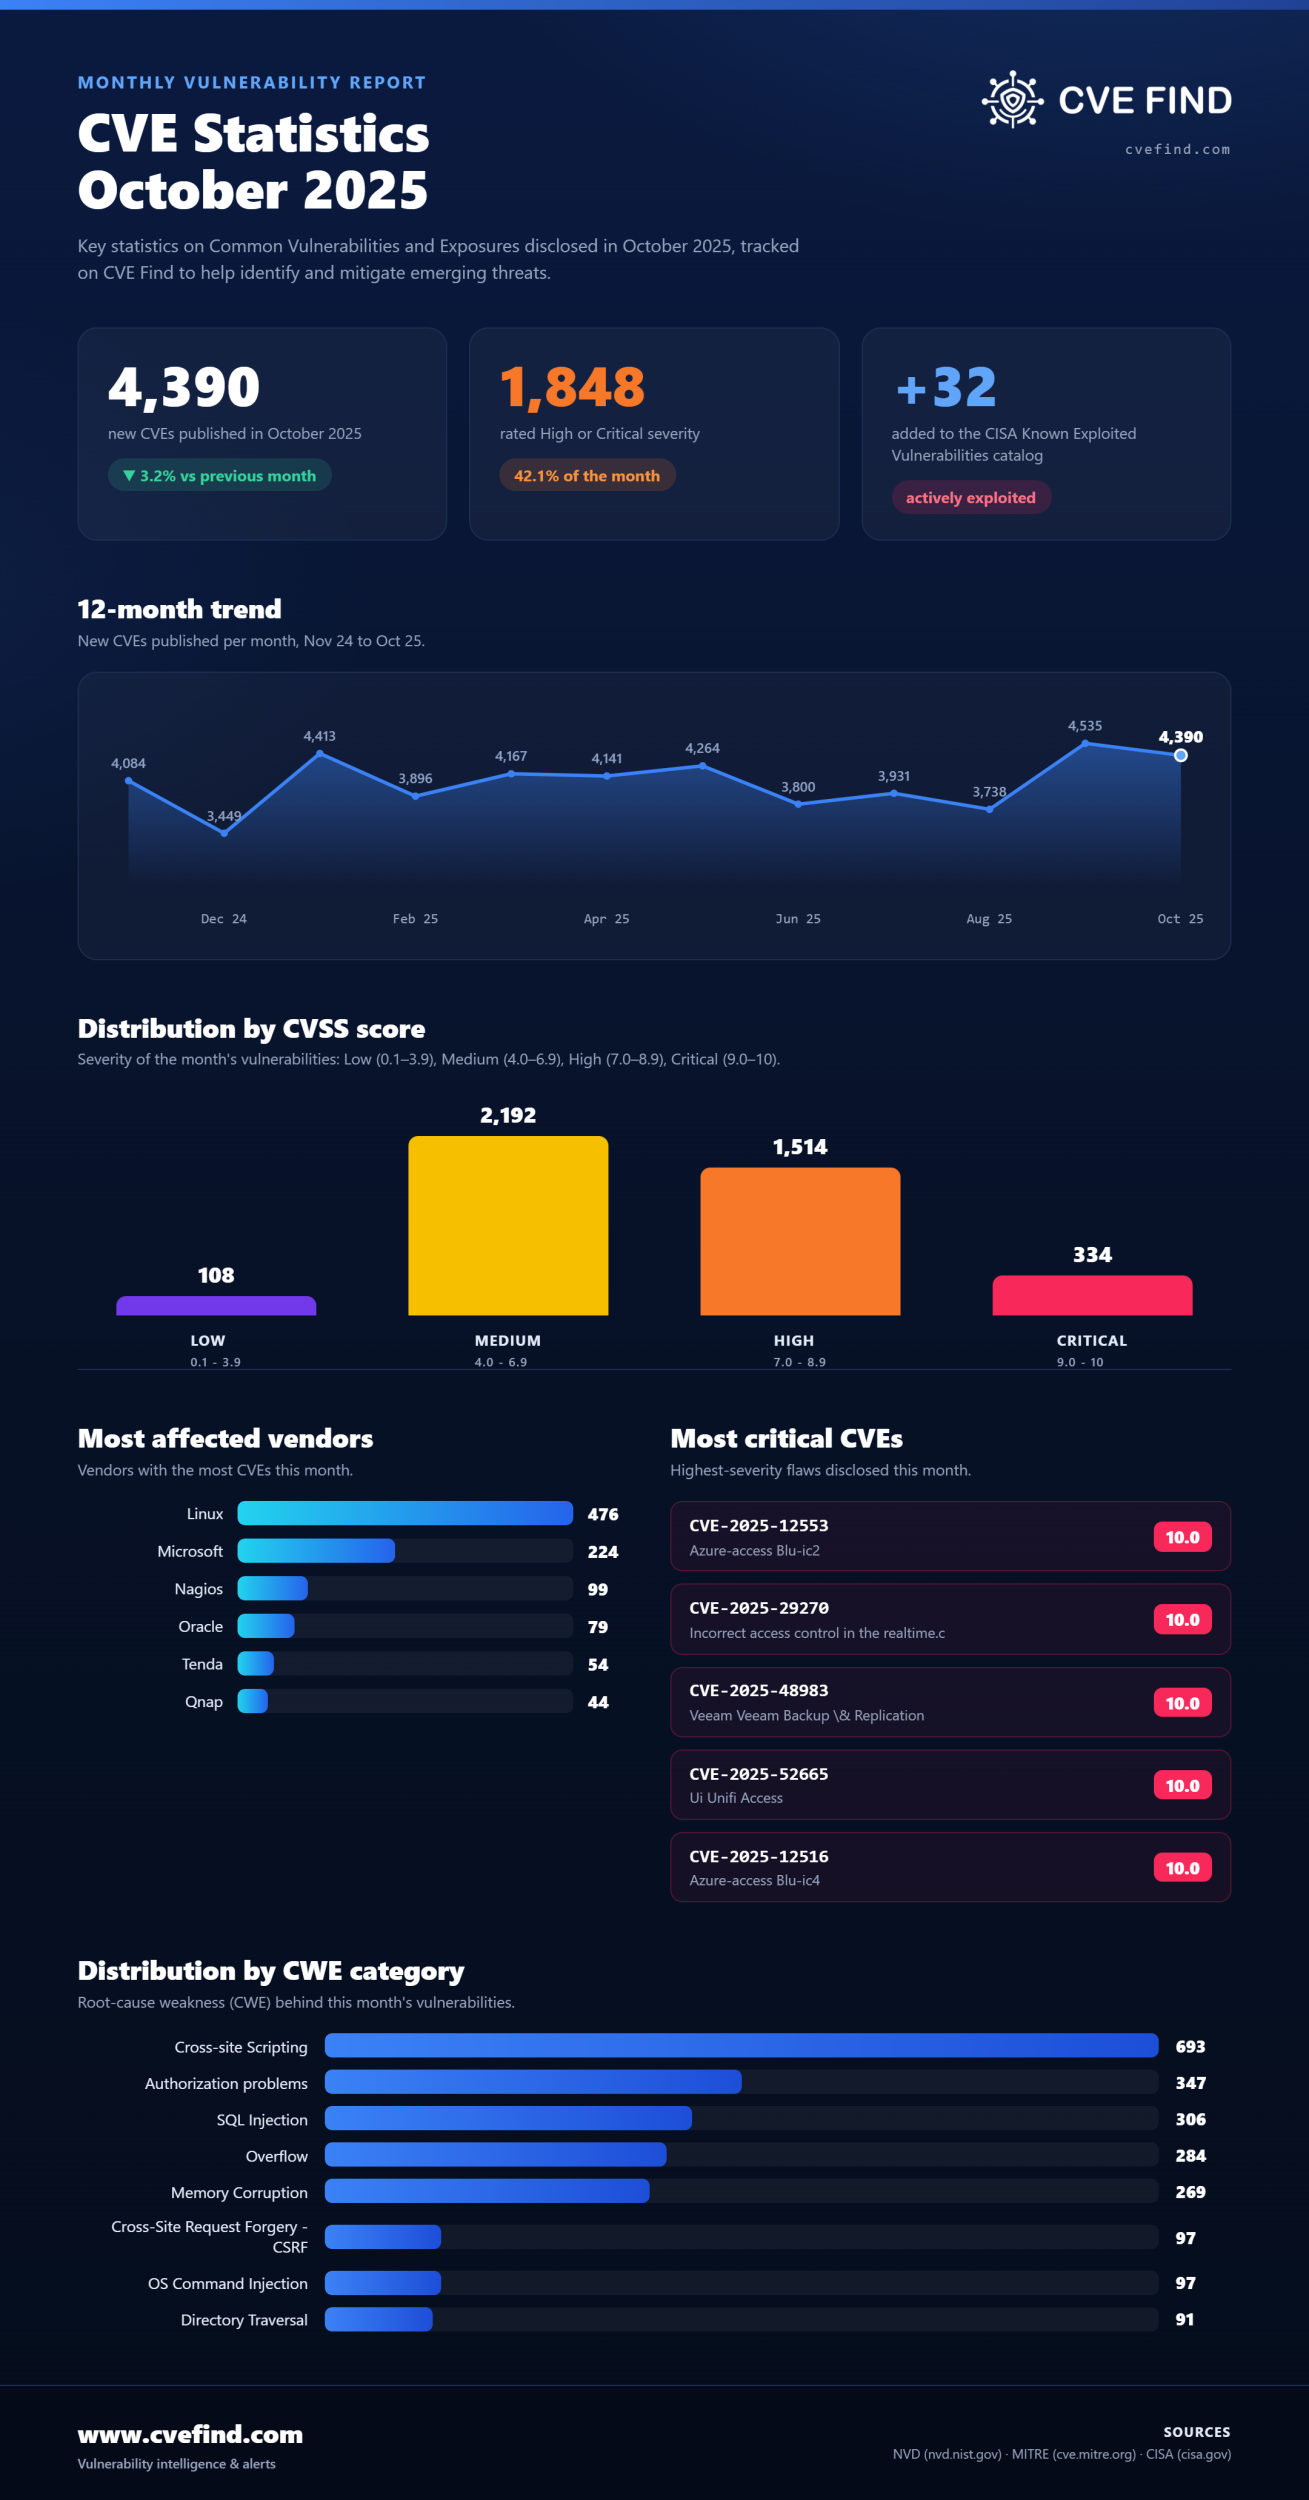
- Nombre total de CVE publiées : 4,390 (-3.2% par rapport au mois précédent)
- Vulnérabilités ajoutées au catalogue CISA KEV : 32
📂 Répartition par catégories principales
- Cross-site Scripting : 693
- Authorization problems : 347
- SQL Injection : 306
- Overflow : 284
- Memory Corruption : 269
- Cross-Site Request Forgery - CSRF : 97
📈 Répartition par score CVSS
- Low : 108
- Medium : 2192
- High : 1514
- Critical : 334
🏢 Éditeurs les plus touchés
📦 Produits les plus touchés
- linux linux_kernel : 476
- microsoft windows_server_2025 : 126
- microsoft windows_11_24h2 : 121
- microsoft windows_11_25h2 : 113
- microsoft windows_server_2022_23h2 : 110
⚠️ CVE marquantes du mois
- CVE-2025-12553 (10 CRITICAL) : Email Server Certificate Verification Disabled.This issue affects BLU-IC2: through 1.19.5; BLU-IC4: through 1.19.5.
- CVE-2025-29270 (10 CRITICAL) : Incorrect access control in the realtime.cgi endpoint of Deep Sea Electronics devices DSE855 v1.1.0 to v1.1.26 allows attackers to gain access to the admin panel and complete co...
- CVE-2025-48983 (10 CRITICAL) : A vulnerability in the Mount service of Veeam Backup & Replication, which allows for remote code execution (RCE) on the Backup infrastructure hosts by an authenticated domain user.
- CVE-2025-52665 (10 CRITICAL) : A malicious actor with access to the management network could exploit a misconfiguration in UniFi’s door access application, UniFi Access, that exposed a management API without ...
- CVE-2025-12516 (10 CRITICAL) : Lack of Graceful Error Handling - HTTP 5xx ErrorThis issue affects BLU-IC2: through 1.19.5; BLU-IC4: through 1.19.5 .
Explorez toutes les données en détail sur CVE Find.
Découvrez comment bexxo peut sécuriser votre entreprise. N'hésitez pas à nous contacter pour une consultation personnalisée dès aujourd'hui !
