CVE-Statistik: Oktober 2025
- 01. November 2025
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im Oktober 2025 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
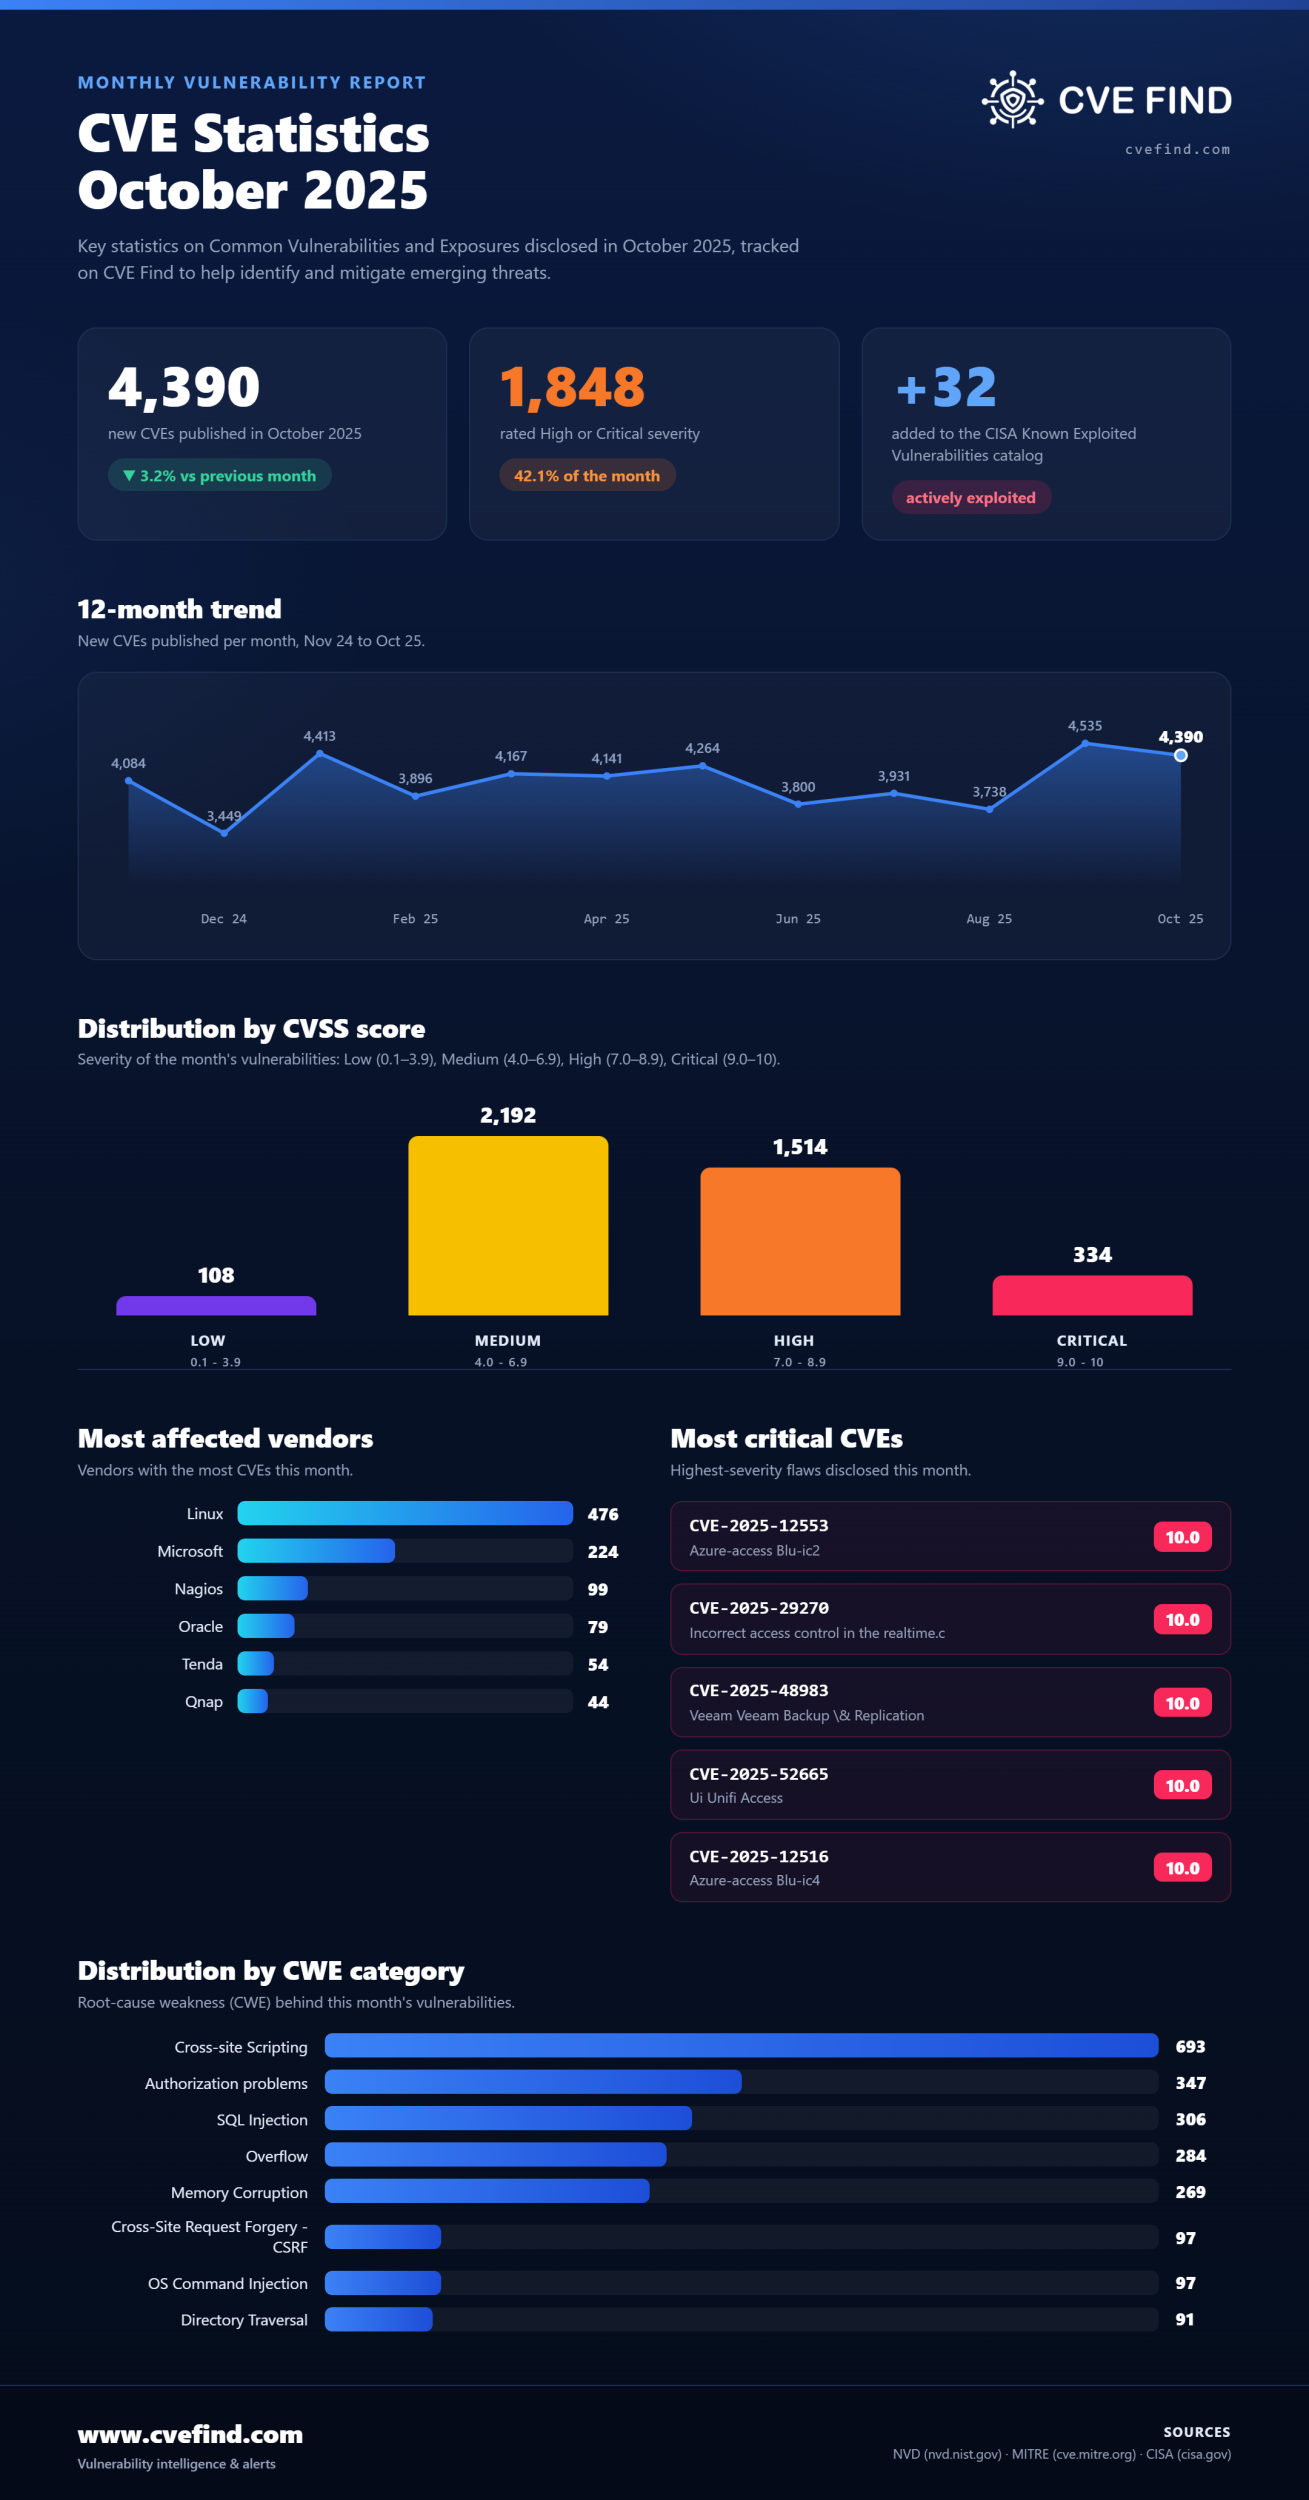
- Gesamtzahl der veröffentlichten CVEs : 4,390 (-3.2% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 32
📂 Verteilung nach Hauptkategorien
- Cross-site Scripting : 693
- Authorization problems : 347
- SQL Injection : 306
- Overflow : 284
- Memory Corruption : 269
- Cross-Site Request Forgery - CSRF : 97
📈 Verteilung nach CVSS-Score
- Low : 108
- Medium : 2192
- High : 1514
- Critical : 334
🏢 Am stärksten betroffene Hersteller
📦 Am stärksten betroffene Produkte
- linux linux_kernel : 476
- microsoft windows_server_2025 : 126
- microsoft windows_11_24h2 : 121
- microsoft windows_11_25h2 : 113
- microsoft windows_server_2022_23h2 : 110
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2025-12553 (10 CRITICAL) : Email Server Certificate Verification Disabled.This issue affects BLU-IC2: through 1.19.5; BLU-IC4: through 1.19.5.
- CVE-2025-29270 (10 CRITICAL) : Incorrect access control in the realtime.cgi endpoint of Deep Sea Electronics devices DSE855 v1.1.0 to v1.1.26 allows attackers to gain access to the admin panel and complete co...
- CVE-2025-48983 (10 CRITICAL) : A vulnerability in the Mount service of Veeam Backup & Replication, which allows for remote code execution (RCE) on the Backup infrastructure hosts by an authenticated domain user.
- CVE-2025-52665 (10 CRITICAL) : A malicious actor with access to the management network could exploit a misconfiguration in UniFi’s door access application, UniFi Access, that exposed a management API without ...
- CVE-2025-12516 (10 CRITICAL) : Lack of Graceful Error Handling - HTTP 5xx ErrorThis issue affects BLU-IC2: through 1.19.5; BLU-IC4: through 1.19.5 .
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
