CVE-Statistik: April 2026
- 01. Mai 2026
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im April 2026 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
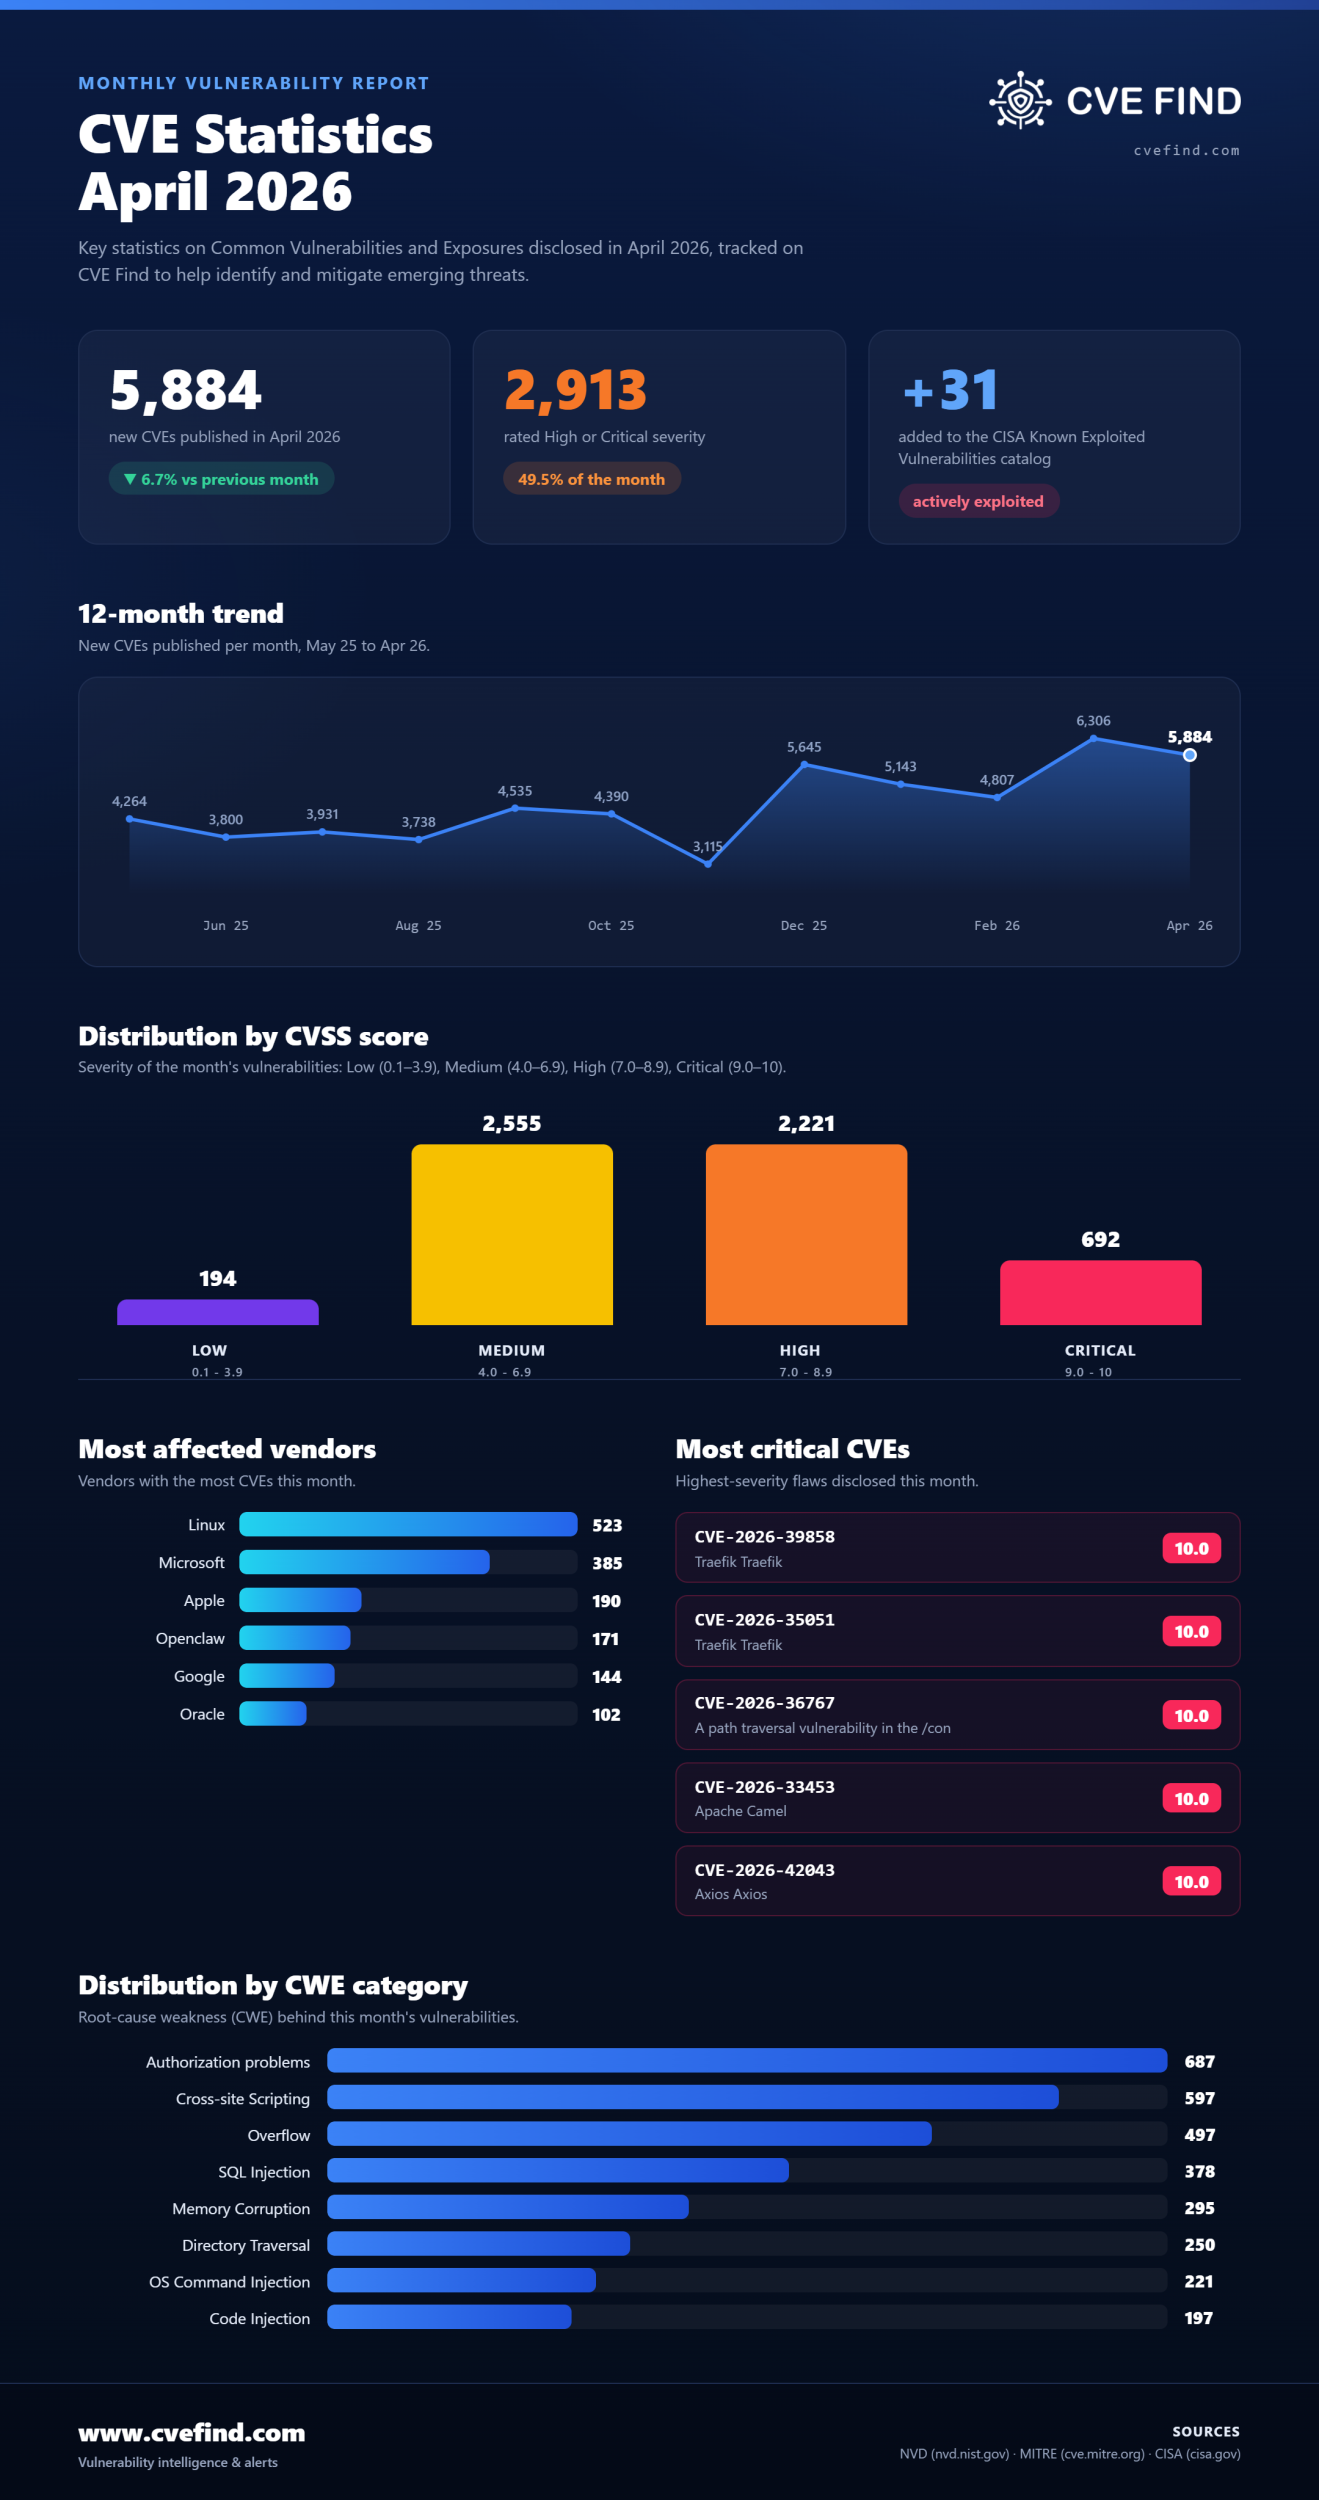
- Gesamtzahl der veröffentlichten CVEs : 5,884 (-6.7% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 31
📂 Verteilung nach Hauptkategorien
- Authorization problems : 687
- Cross-site Scripting : 597
- Overflow : 497
- SQL Injection : 378
- Memory Corruption : 295
- Directory Traversal : 250
📈 Verteilung nach CVSS-Score
- Low : 194
- Medium : 2555
- High : 2221
- Critical : 692
🏢 Am stärksten betroffene Hersteller
📦 Am stärksten betroffene Produkte
- linux linux_kernel : 523
- microsoft windows : 206
- apple macos : 187
- openclaw openclaw : 171
- google chrome : 141
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2026-39858 (10 CRITICAL) : Traefik is an HTTP reverse proxy and load balancer. Prior to versions 2.11.43, 3.6.14, and 3.7.0-rc.2, there is a high severity authentication bypass vulnerability in Traefik's ...
- CVE-2026-35051 (10 CRITICAL) : Traefik is an HTTP reverse proxy and load balancer. Prior to versions 2.11.43, 3.6.14, and 3.7.0-rc.2, there is an authentication bypass vulnerability in Traefik's ForwardAuth m...
- CVE-2026-36767 (10 CRITICAL) : A path traversal vulnerability in the /content/images/add endpoint of shopizer v3.2.5 allows attackers write arbitrary files to any writeable path via a crafted POST request.
- CVE-2026-33453 (10 CRITICAL) : Improperly Controlled Modification of Dynamically-Determined Object Attributes vulnerability in Apache Camel Camel-Coap component. Apache Camel's camel-coap component is vulner...
- CVE-2026-42043 (10 CRITICAL) : Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.1 and 0.31.1, an attacker who can influence the target URL of an Axios request can use any addres...
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
