CVE Statistics: April 2026
- May 01, 2026
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in April 2026 on CVE Find.
🔎 Overview
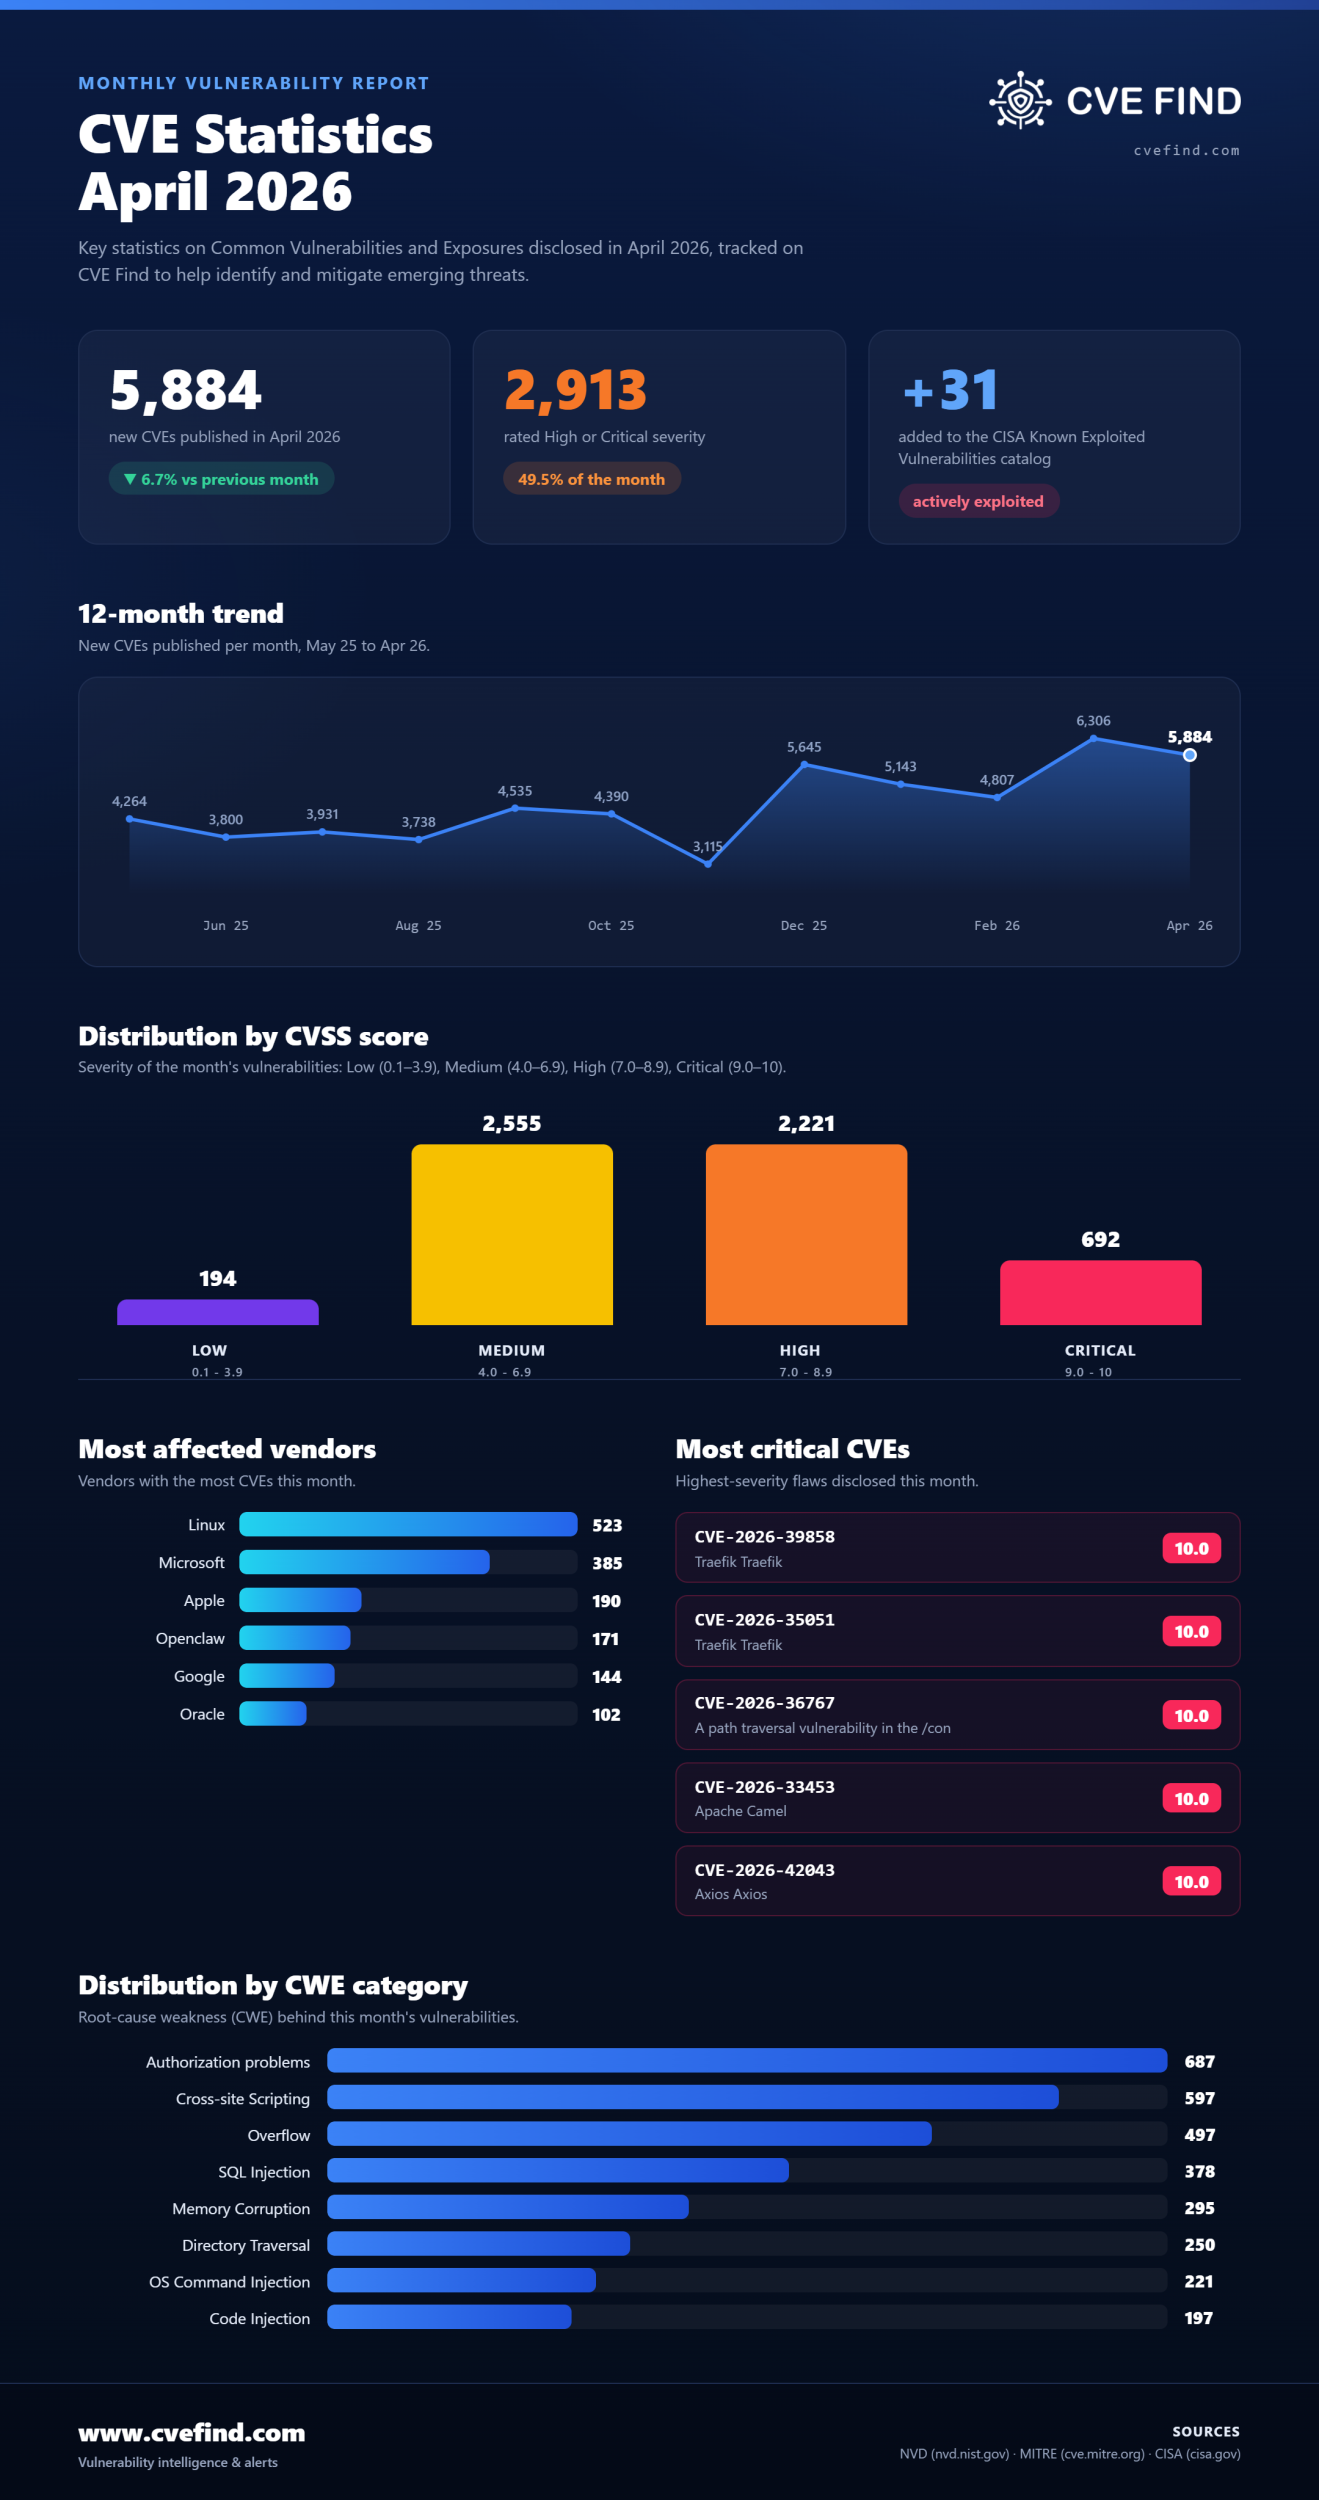
- Total number of CVEs published : 5,884 (-6.7% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 31
📂 Breakdown by main categories
- Authorization problems : 687
- Cross-site Scripting : 597
- Overflow : 497
- SQL Injection : 378
- Memory Corruption : 295
- Directory Traversal : 250
📈 Breakdown by CVSS score
- Low : 194
- Medium : 2555
- High : 2221
- Critical : 692
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 523
- microsoft windows : 206
- apple macos : 187
- openclaw openclaw : 171
- google chrome : 141
⚠️ Notable CVEs of the month
- CVE-2026-39858 (10 CRITICAL) : Traefik is an HTTP reverse proxy and load balancer. Prior to versions 2.11.43, 3.6.14, and 3.7.0-rc.2, there is a high severity authentication bypass vulnerability in Traefik's ...
- CVE-2026-35051 (10 CRITICAL) : Traefik is an HTTP reverse proxy and load balancer. Prior to versions 2.11.43, 3.6.14, and 3.7.0-rc.2, there is an authentication bypass vulnerability in Traefik's ForwardAuth m...
- CVE-2026-36767 (10 CRITICAL) : A path traversal vulnerability in the /content/images/add endpoint of shopizer v3.2.5 allows attackers write arbitrary files to any writeable path via a crafted POST request.
- CVE-2026-33453 (10 CRITICAL) : Improperly Controlled Modification of Dynamically-Determined Object Attributes vulnerability in Apache Camel Camel-Coap component. Apache Camel's camel-coap component is vulner...
- CVE-2026-42043 (10 CRITICAL) : Axios is a promise based HTTP client for the browser and Node.js. Prior to 1.15.1 and 0.31.1, an attacker who can influence the target URL of an Axios request can use any addres...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
