CVE-Statistik: August 2025
- 01. September 2025
- Temps de lecture: 3 min min
🌐 Entdecken Sie die wichtigsten Zahlen zu den im August 2025 veröffentlichten Schwachstellen auf CVE Find.
🔎 Überblick
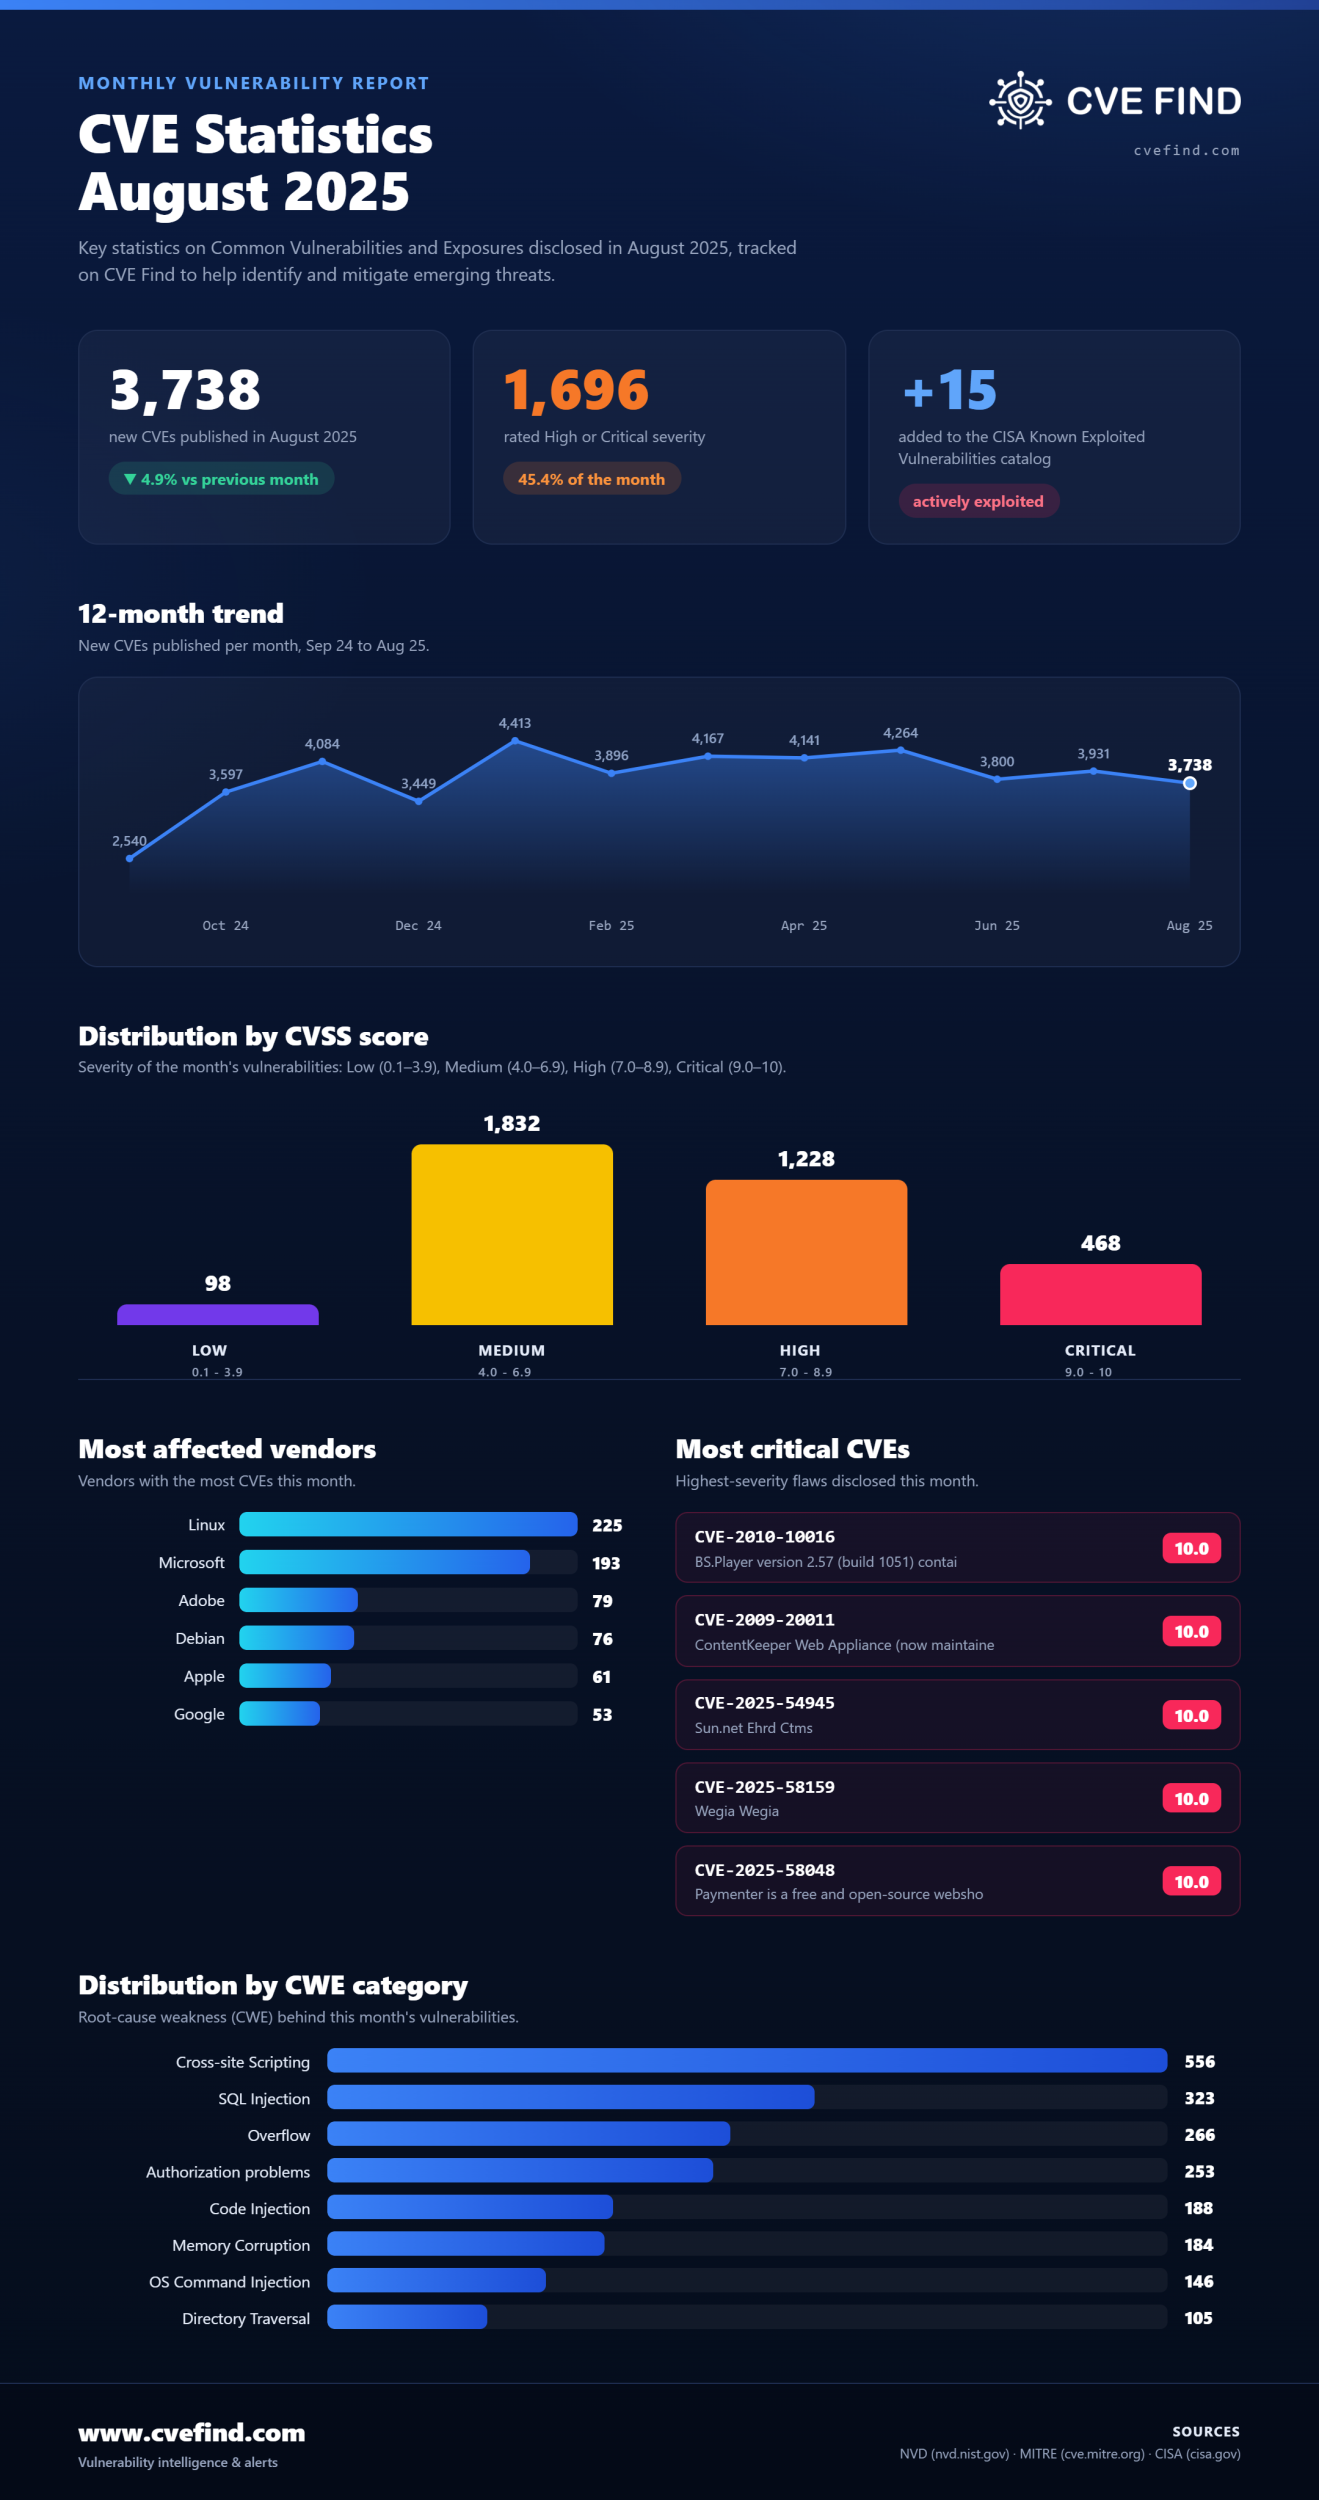
- Gesamtzahl der veröffentlichten CVEs : 3,738 (-4.9% gegenüber dem Vormonat)
- Neue Einträge im CISA-KEV-Katalog : 15
📂 Verteilung nach Hauptkategorien
- Cross-site Scripting : 556
- SQL Injection : 323
- Overflow : 266
- Authorization problems : 253
- Code Injection : 188
- Memory Corruption : 184
📈 Verteilung nach CVSS-Score
- Low : 98
- Medium : 1832
- High : 1228
- Critical : 468
🏢 Am stärksten betroffene Hersteller
📦 Am stärksten betroffene Produkte
- linux linux_kernel : 225
- microsoft windows : 79
- debian debian_linux : 75
- microsoft windows_server_2025 : 66
- microsoft windows_server_2022_23h2 : 62
⚠️ Bemerkenswerte CVEs des Monats
- CVE-2010-10016 (10 CRITICAL) : BS.Player version 2.57 (build 1051) contains a vulnerability in its playlist import functionality. When processing .m3u files, the application fails to properly validate the len...
- CVE-2009-20011 (10 CRITICAL) : ContentKeeper Web Appliance (now maintained by Impero Software) versions prior to 125.10 are vulnerable to remote command execution due to insecure handling of file uploads via ...
- CVE-2025-54945 (10 CRITICAL) : An external control of file name or path vulnerability in SUNNET Corporate Training Management System before 10.11 allows remote attackers to execute arbitrary system commands v...
- CVE-2025-58159 (10 CRITICAL) : WeGIA is a Web manager for charitable institutions. Prior to version 3.4.11, a remote code execution vulnerability was identified, caused by improper validation of uploaded file...
- CVE-2025-58048 (10 CRITICAL) : Paymenter is a free and open-source webshop solution for hostings. Prior to version 1.2.11, the ticket attachments functionality in Paymenter allows a malicious authenticated us...
Alle Daten im Detail finden Sie auf CVE Find.
Entdecken Sie, wie bexxo Ihr Unternehmen sichern kann. Zögern Sie nicht, uns noch heute für eine persönliche Beratung zu kontaktieren!
