CVE Statistics: August 2025
- September 01, 2025
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in August 2025 on CVE Find.
🔎 Overview
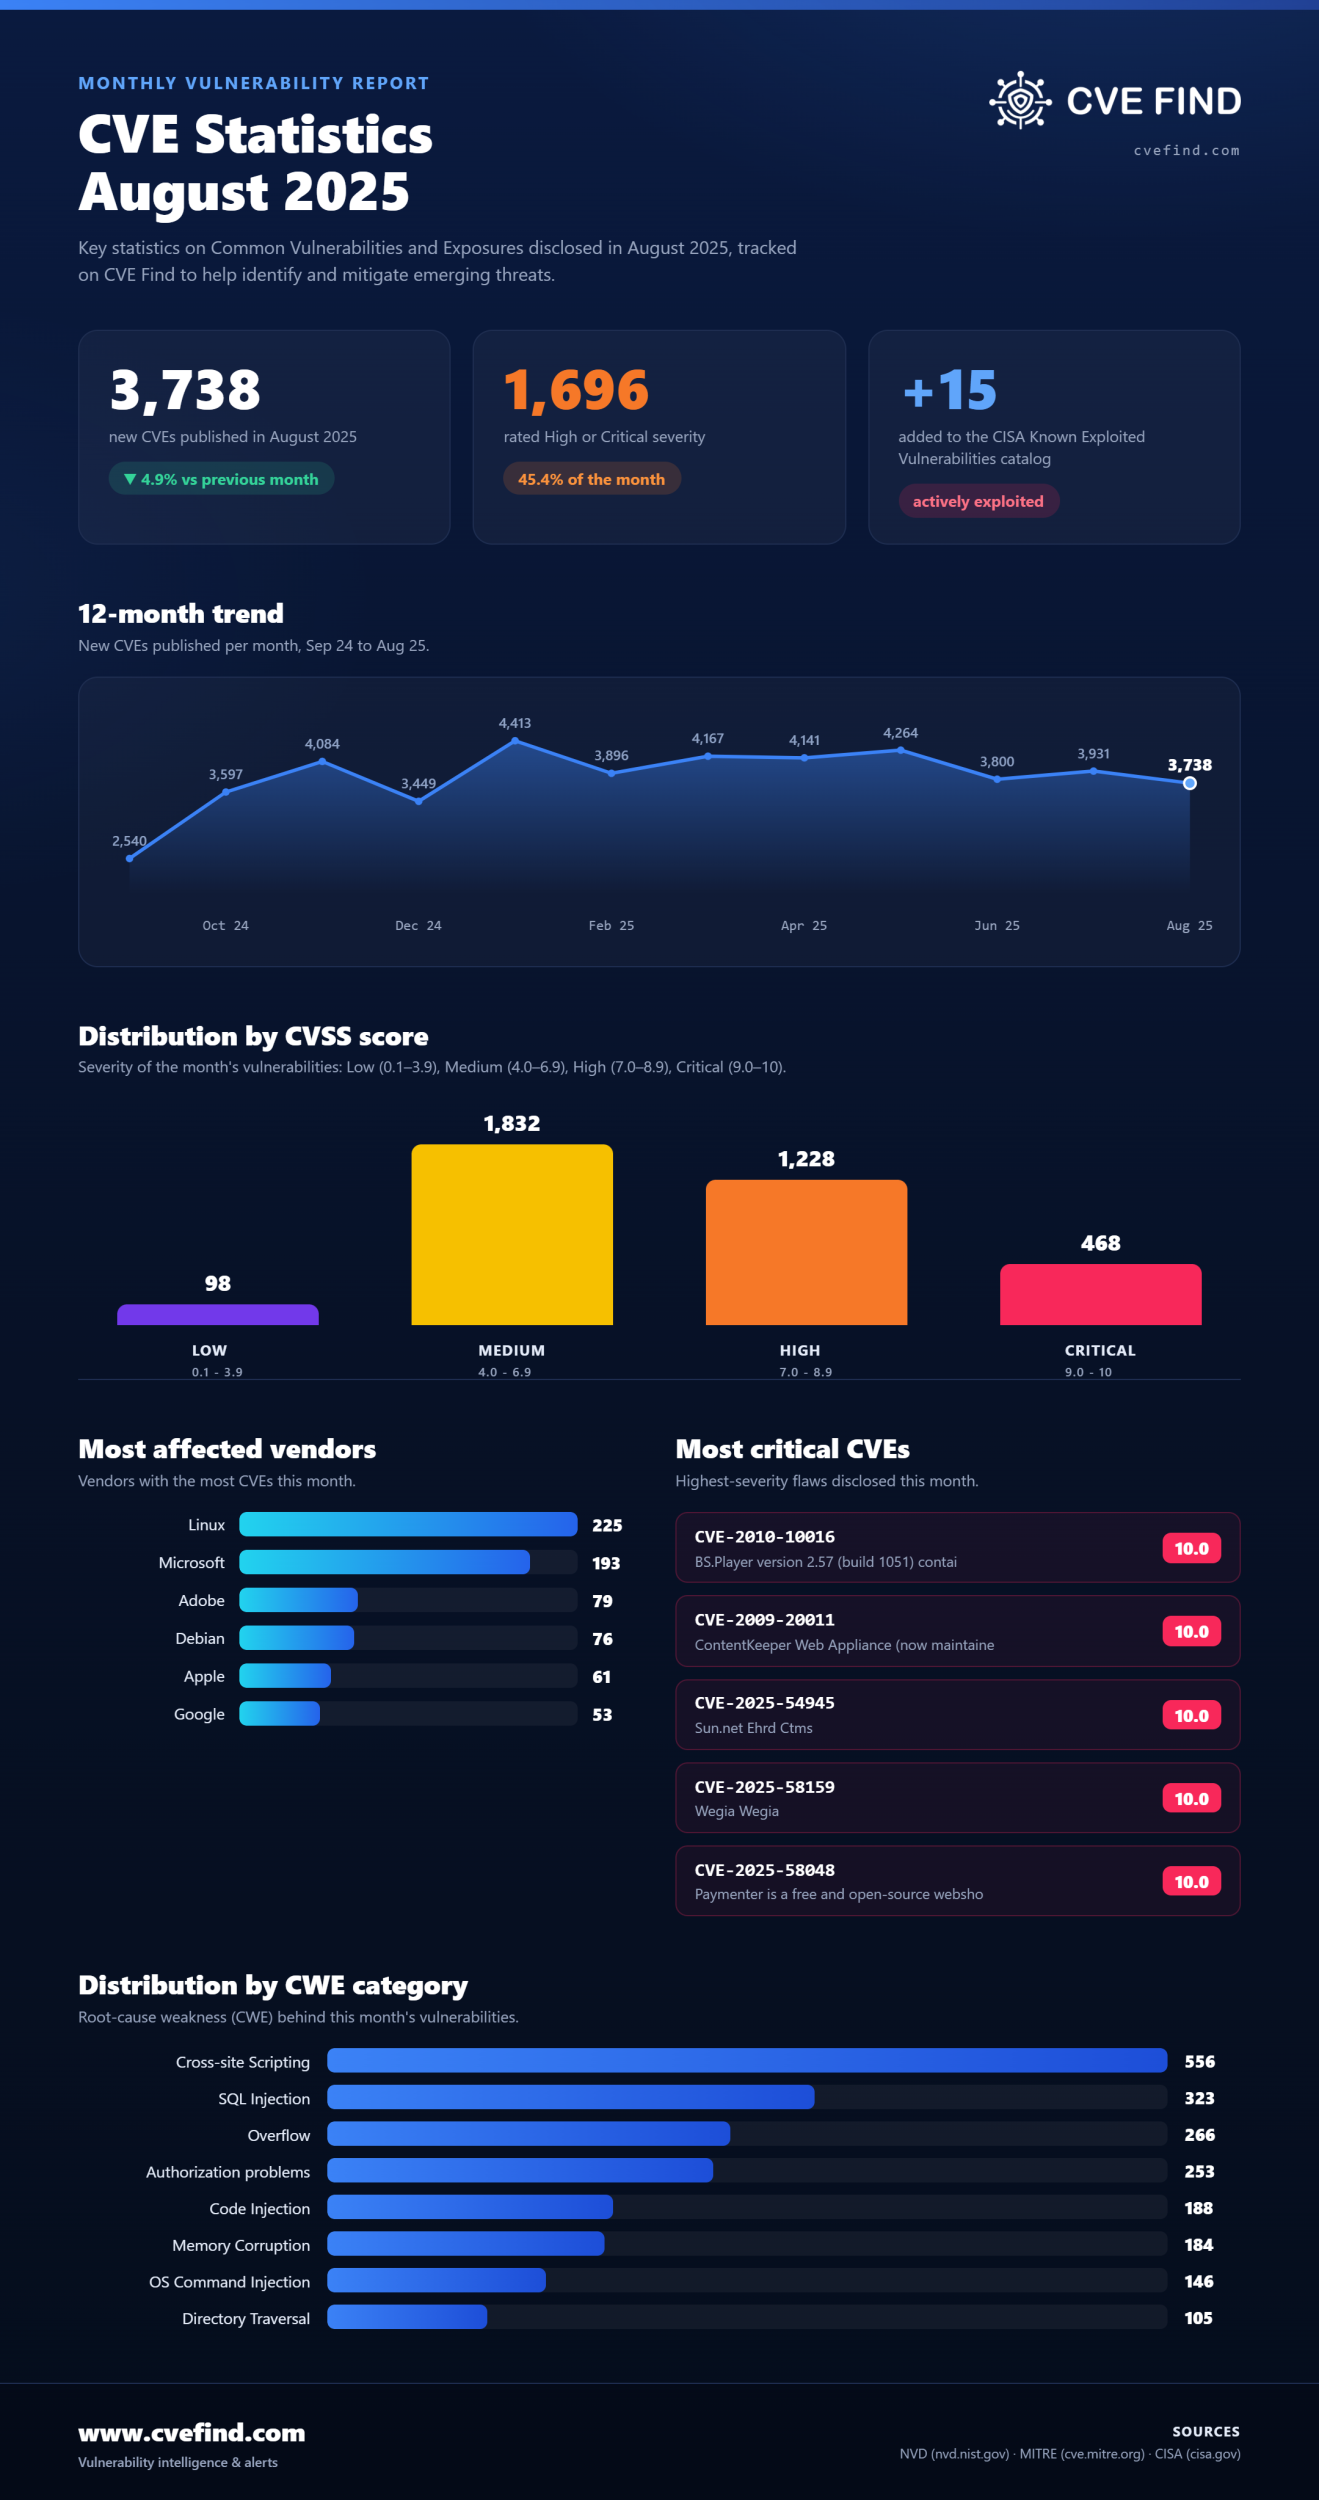
- Total number of CVEs published : 3,738 (-4.9% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 15
📂 Breakdown by main categories
- Cross-site Scripting : 556
- SQL Injection : 323
- Overflow : 266
- Authorization problems : 253
- Code Injection : 188
- Memory Corruption : 184
📈 Breakdown by CVSS score
- Low : 98
- Medium : 1832
- High : 1228
- Critical : 468
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 225
- microsoft windows : 79
- debian debian_linux : 75
- microsoft windows_server_2025 : 66
- microsoft windows_server_2022_23h2 : 62
⚠️ Notable CVEs of the month
- CVE-2010-10016 (10 CRITICAL) : BS.Player version 2.57 (build 1051) contains a vulnerability in its playlist import functionality. When processing .m3u files, the application fails to properly validate the len...
- CVE-2009-20011 (10 CRITICAL) : ContentKeeper Web Appliance (now maintained by Impero Software) versions prior to 125.10 are vulnerable to remote command execution due to insecure handling of file uploads via ...
- CVE-2025-54945 (10 CRITICAL) : An external control of file name or path vulnerability in SUNNET Corporate Training Management System before 10.11 allows remote attackers to execute arbitrary system commands v...
- CVE-2025-58159 (10 CRITICAL) : WeGIA is a Web manager for charitable institutions. Prior to version 3.4.11, a remote code execution vulnerability was identified, caused by improper validation of uploaded file...
- CVE-2025-58048 (10 CRITICAL) : Paymenter is a free and open-source webshop solution for hostings. Prior to version 1.2.11, the ticket attachments functionality in Paymenter allows a malicious authenticated us...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
