Bexxo supports Swiss SMEs in their IT security.

 Swiss
Label
Swiss Label Certification
Bexxo is Swiss Label certified, the quality label guaranteeing that our services are provided in Switzerland, by a Swiss company, according to Swiss quality standards.
 CyberSafe Switzerland Partner
Bexxo is a certified CyberSafe Switzerland partner, the official Swiss Confederation programme dedicated to promoting cybersecurity for Swiss businesses.
Our Cybersecurity Services
Website Security

01 Complete audit and vulnerability detection
A Bexxo web audit is a comprehensive technical examination of the company's website: automated and manual analysis of vulnerabilities (OWASP Top 10, SQL injections, XSS, CSRF, server configuration), report classified by criticality, and prioritized action plan. Our clients fix an average of 12 to 15 vulnerabilities per engagement, with a clear remediation plan, before they could be exploited.

02 Protection against attacks
Bexxo deploys protections against the most frequent attack vectors: SQL injections, XSS, CSRF, brute force and ClickJacking. These vectors account for 88% of recorded web attacks (Verizon DBIR 2025): identifying and blocking them is enough to eliminate the vast majority of risk. Each measure is documented in the audit report with its criticality level.

03 Data security
The nLPD (in effect since September 1, 2023) sets clear obligations for securing personal data for all Swiss companies. Bexxo supports SMEs in assessing their nLPD compliance, identifying gaps and implementing the required technical measures. Fines of up to CHF 250,000 simply don't apply to our clients.

Enterprise Network Security
01 Network infrastructure audit and analysis
Our network audit maps all exposed attack vectors of your infrastructure, with an ISO 27001 and NIST CSF compliant report. In 2024, the Federal Office for Cybersecurity recorded 62,954 incidents in Switzerland. The audit tells you exactly where you stand.
02 Global IT infrastructure protection
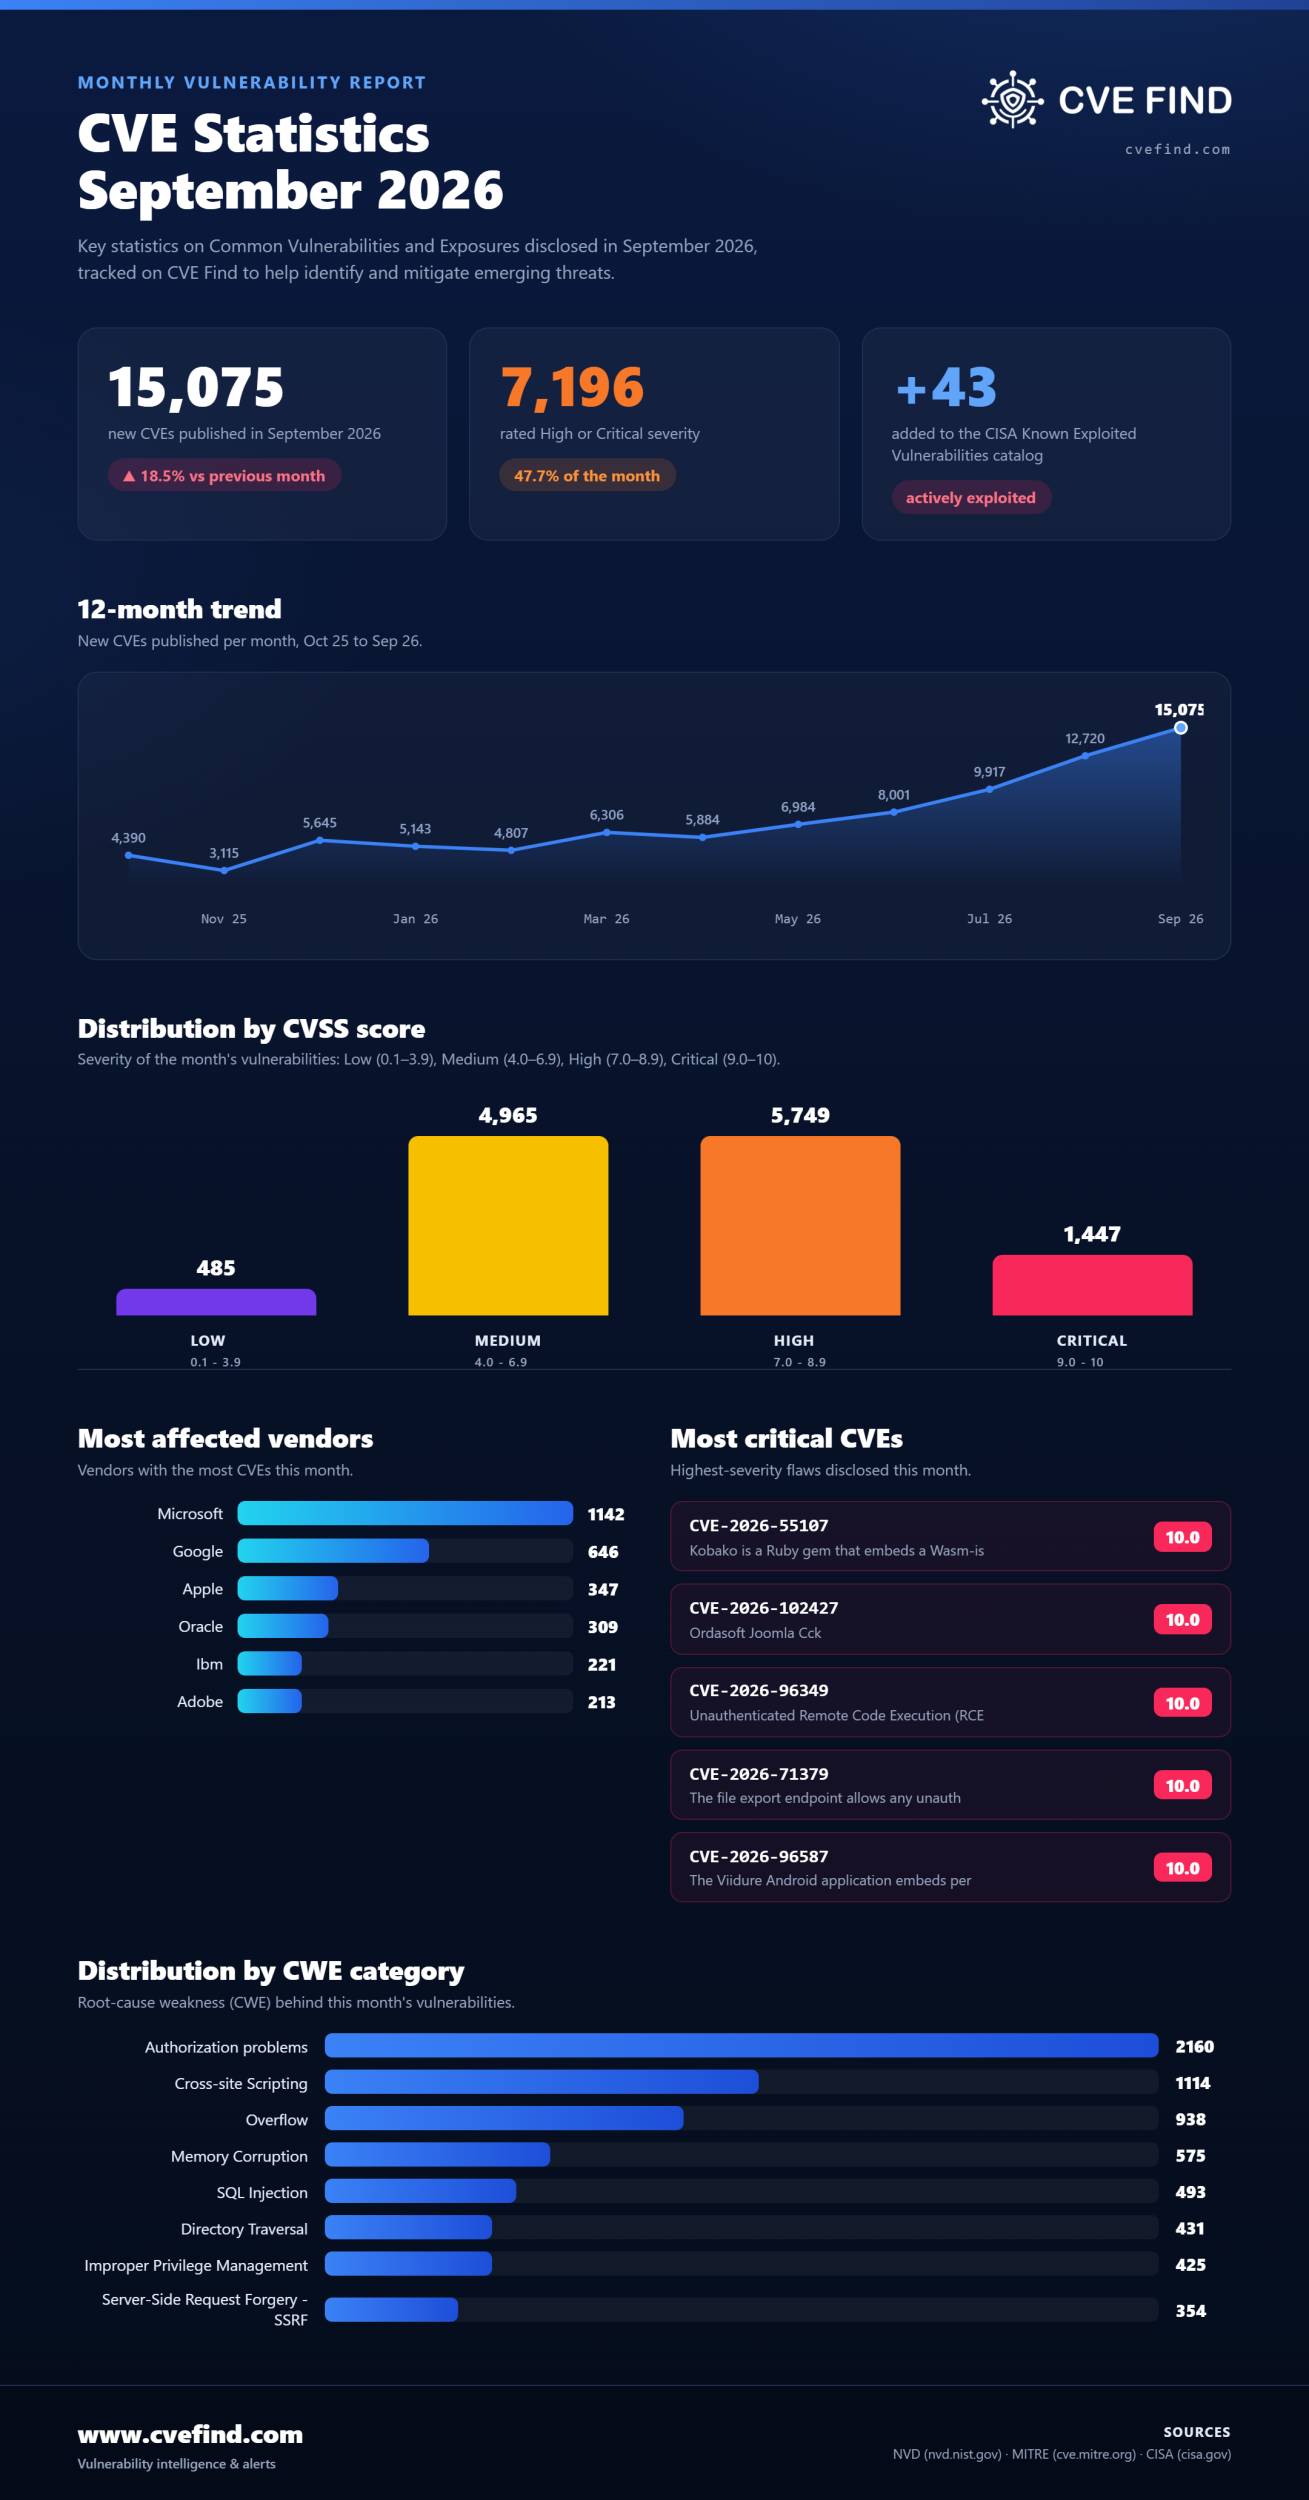
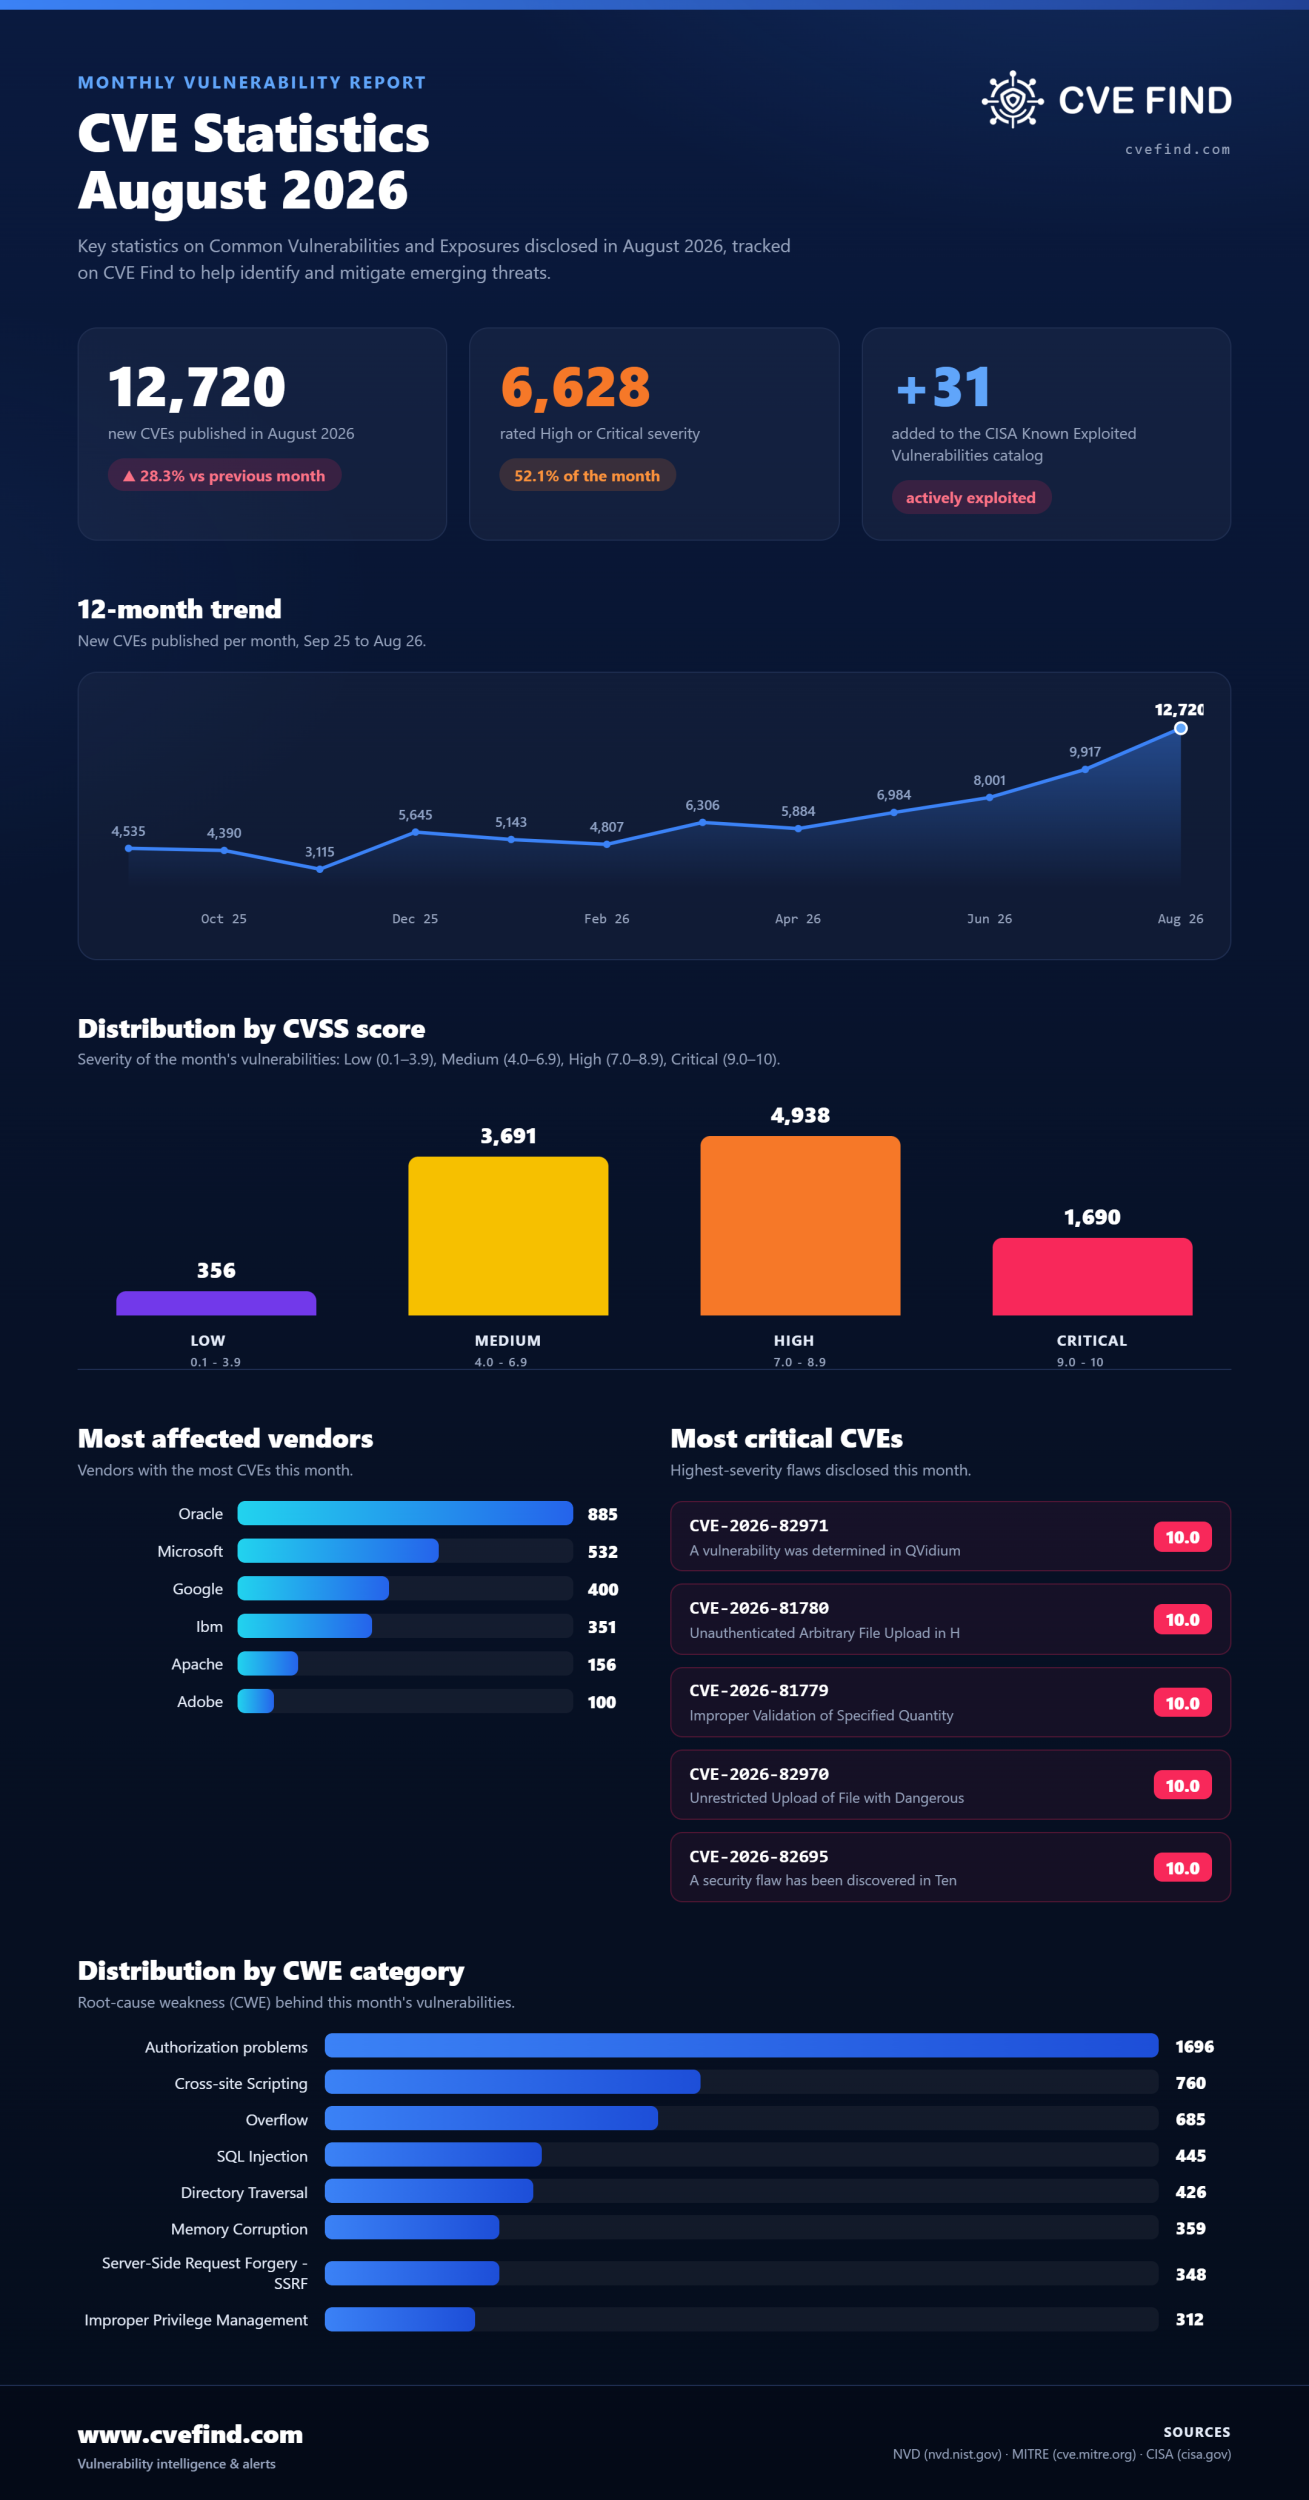
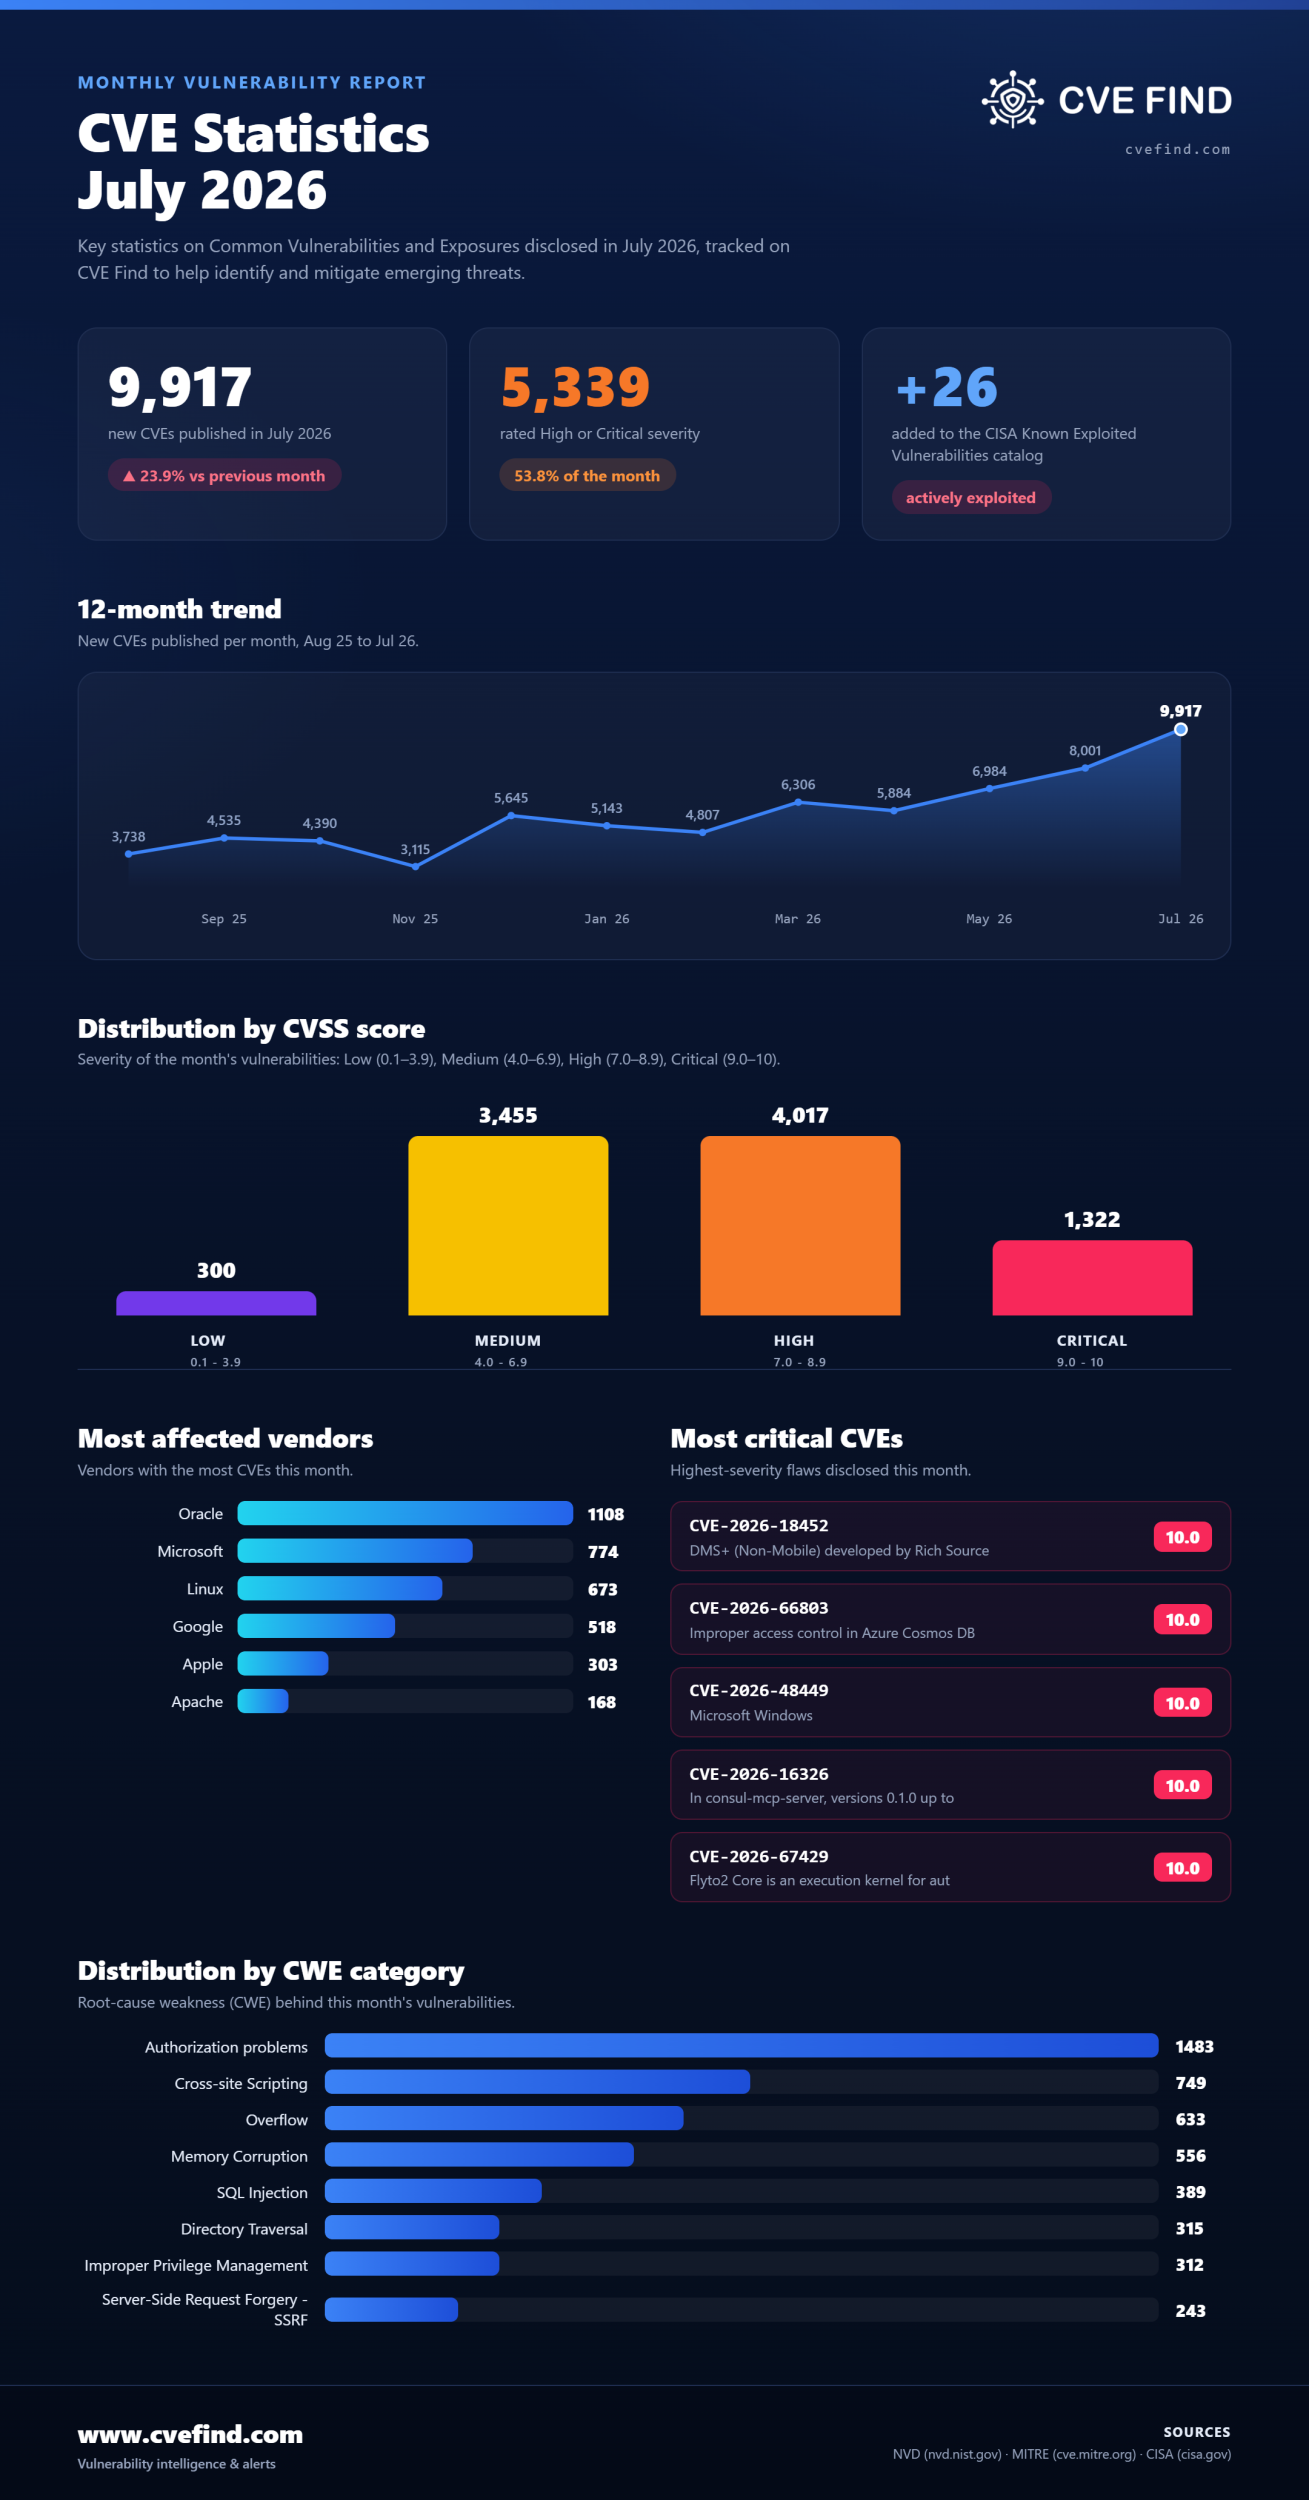
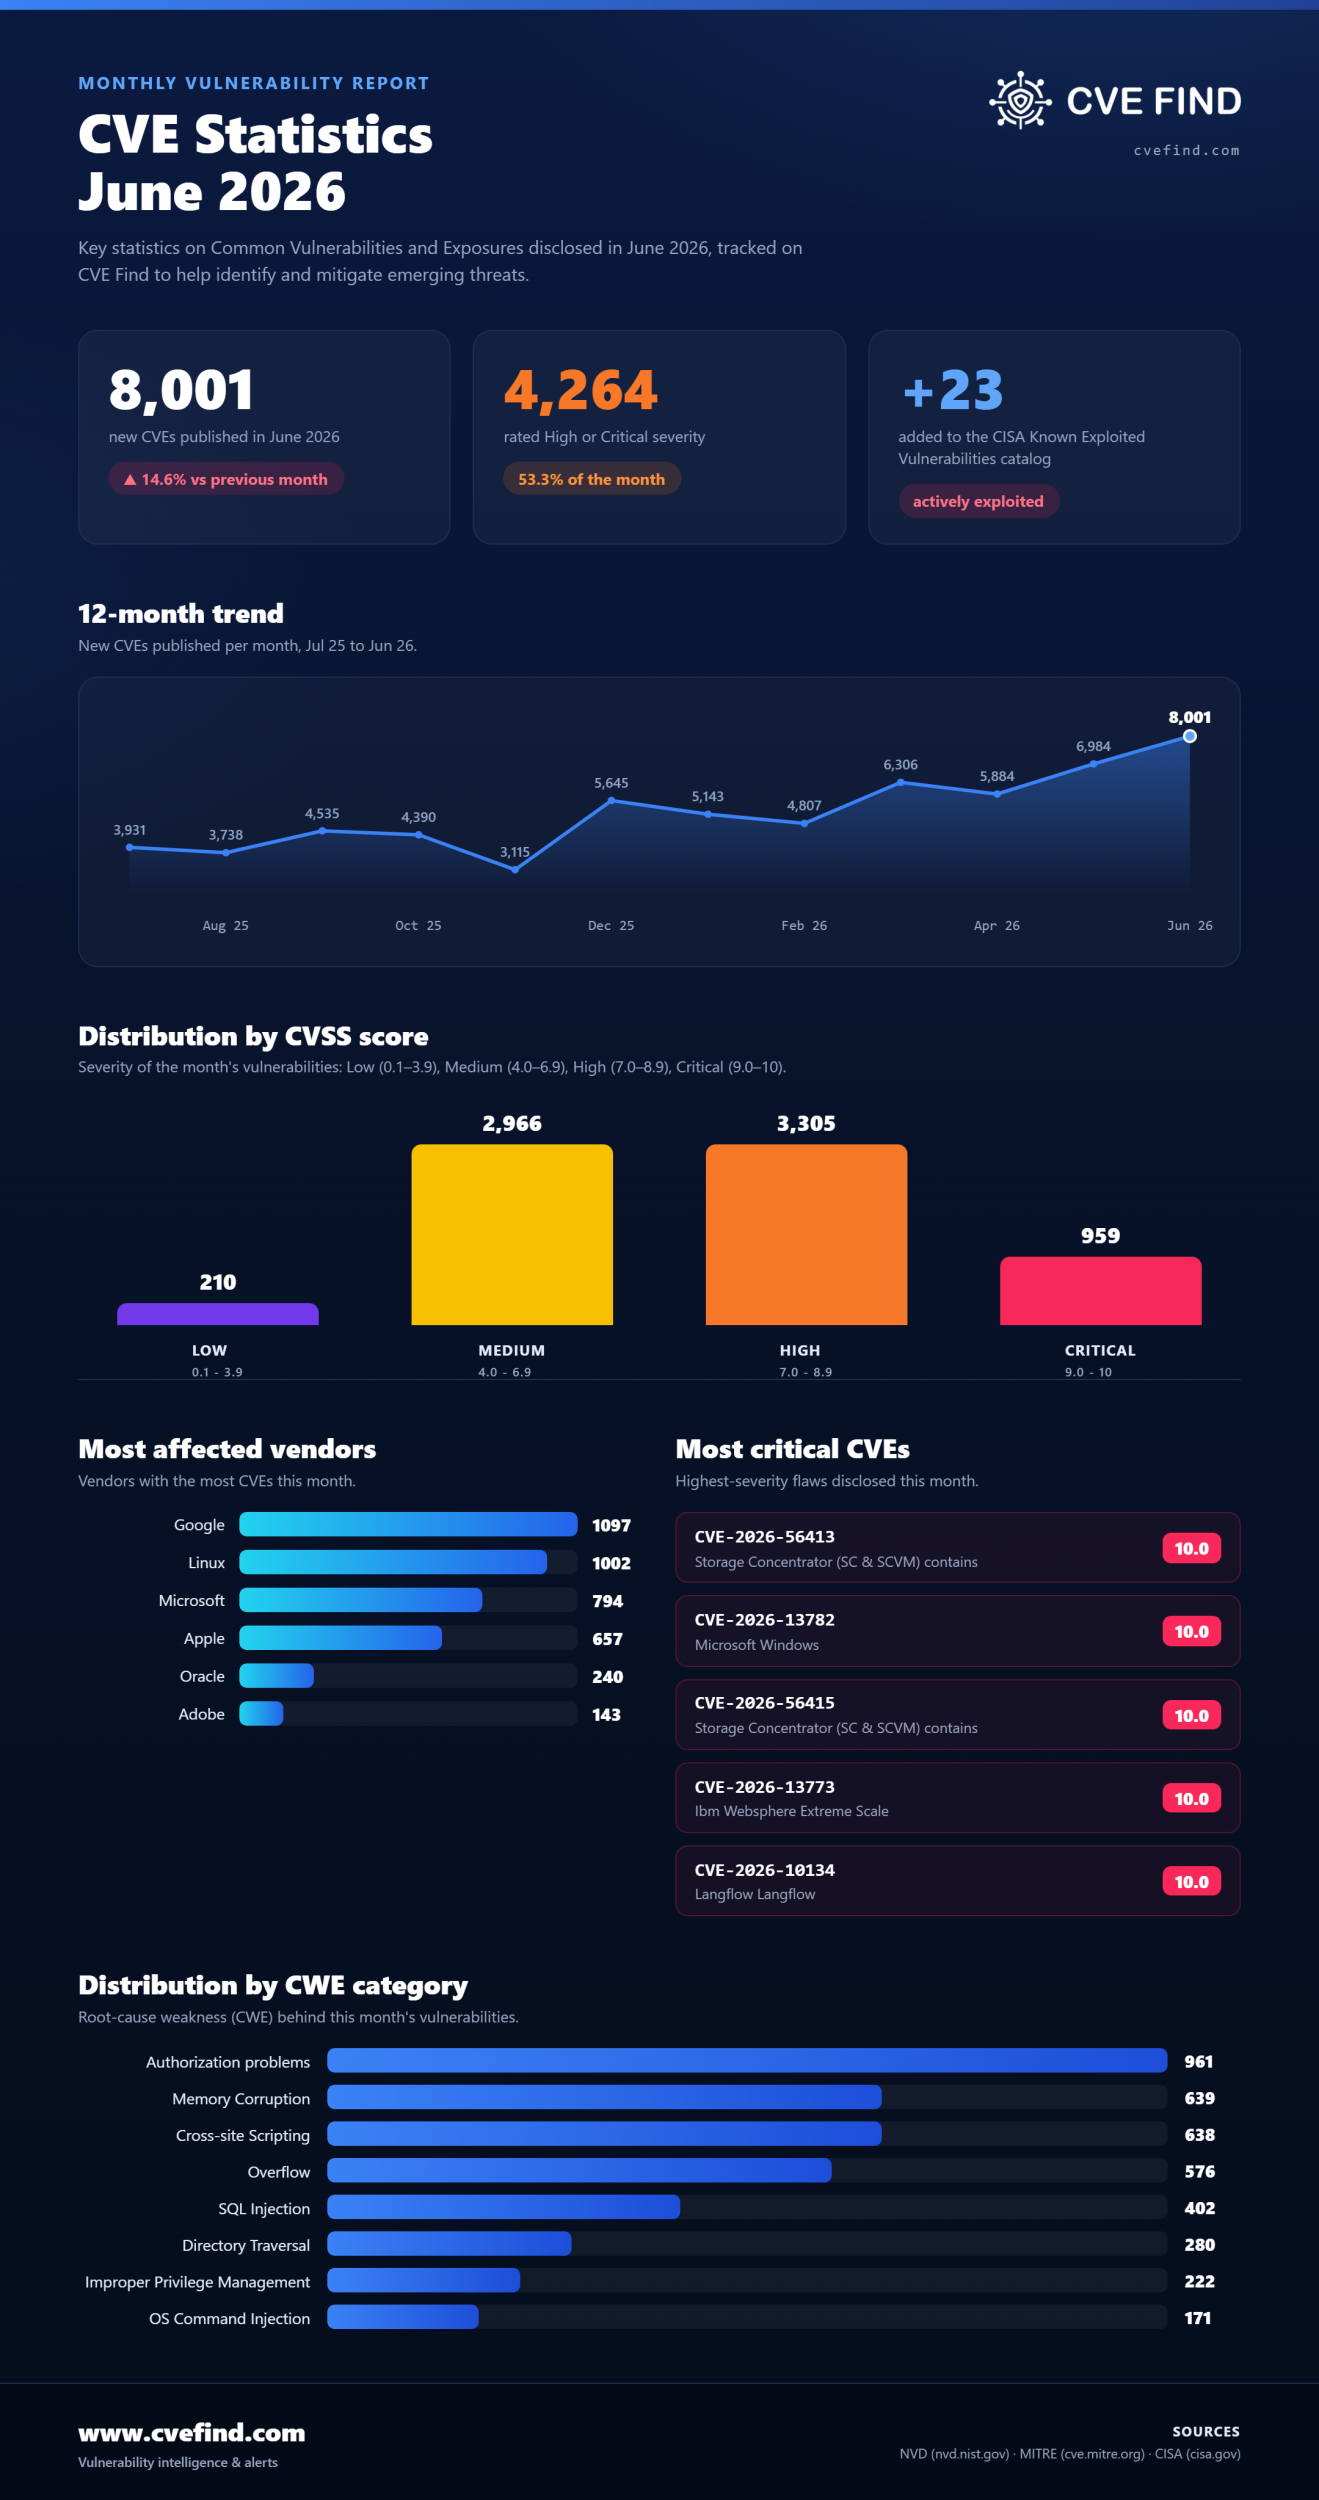
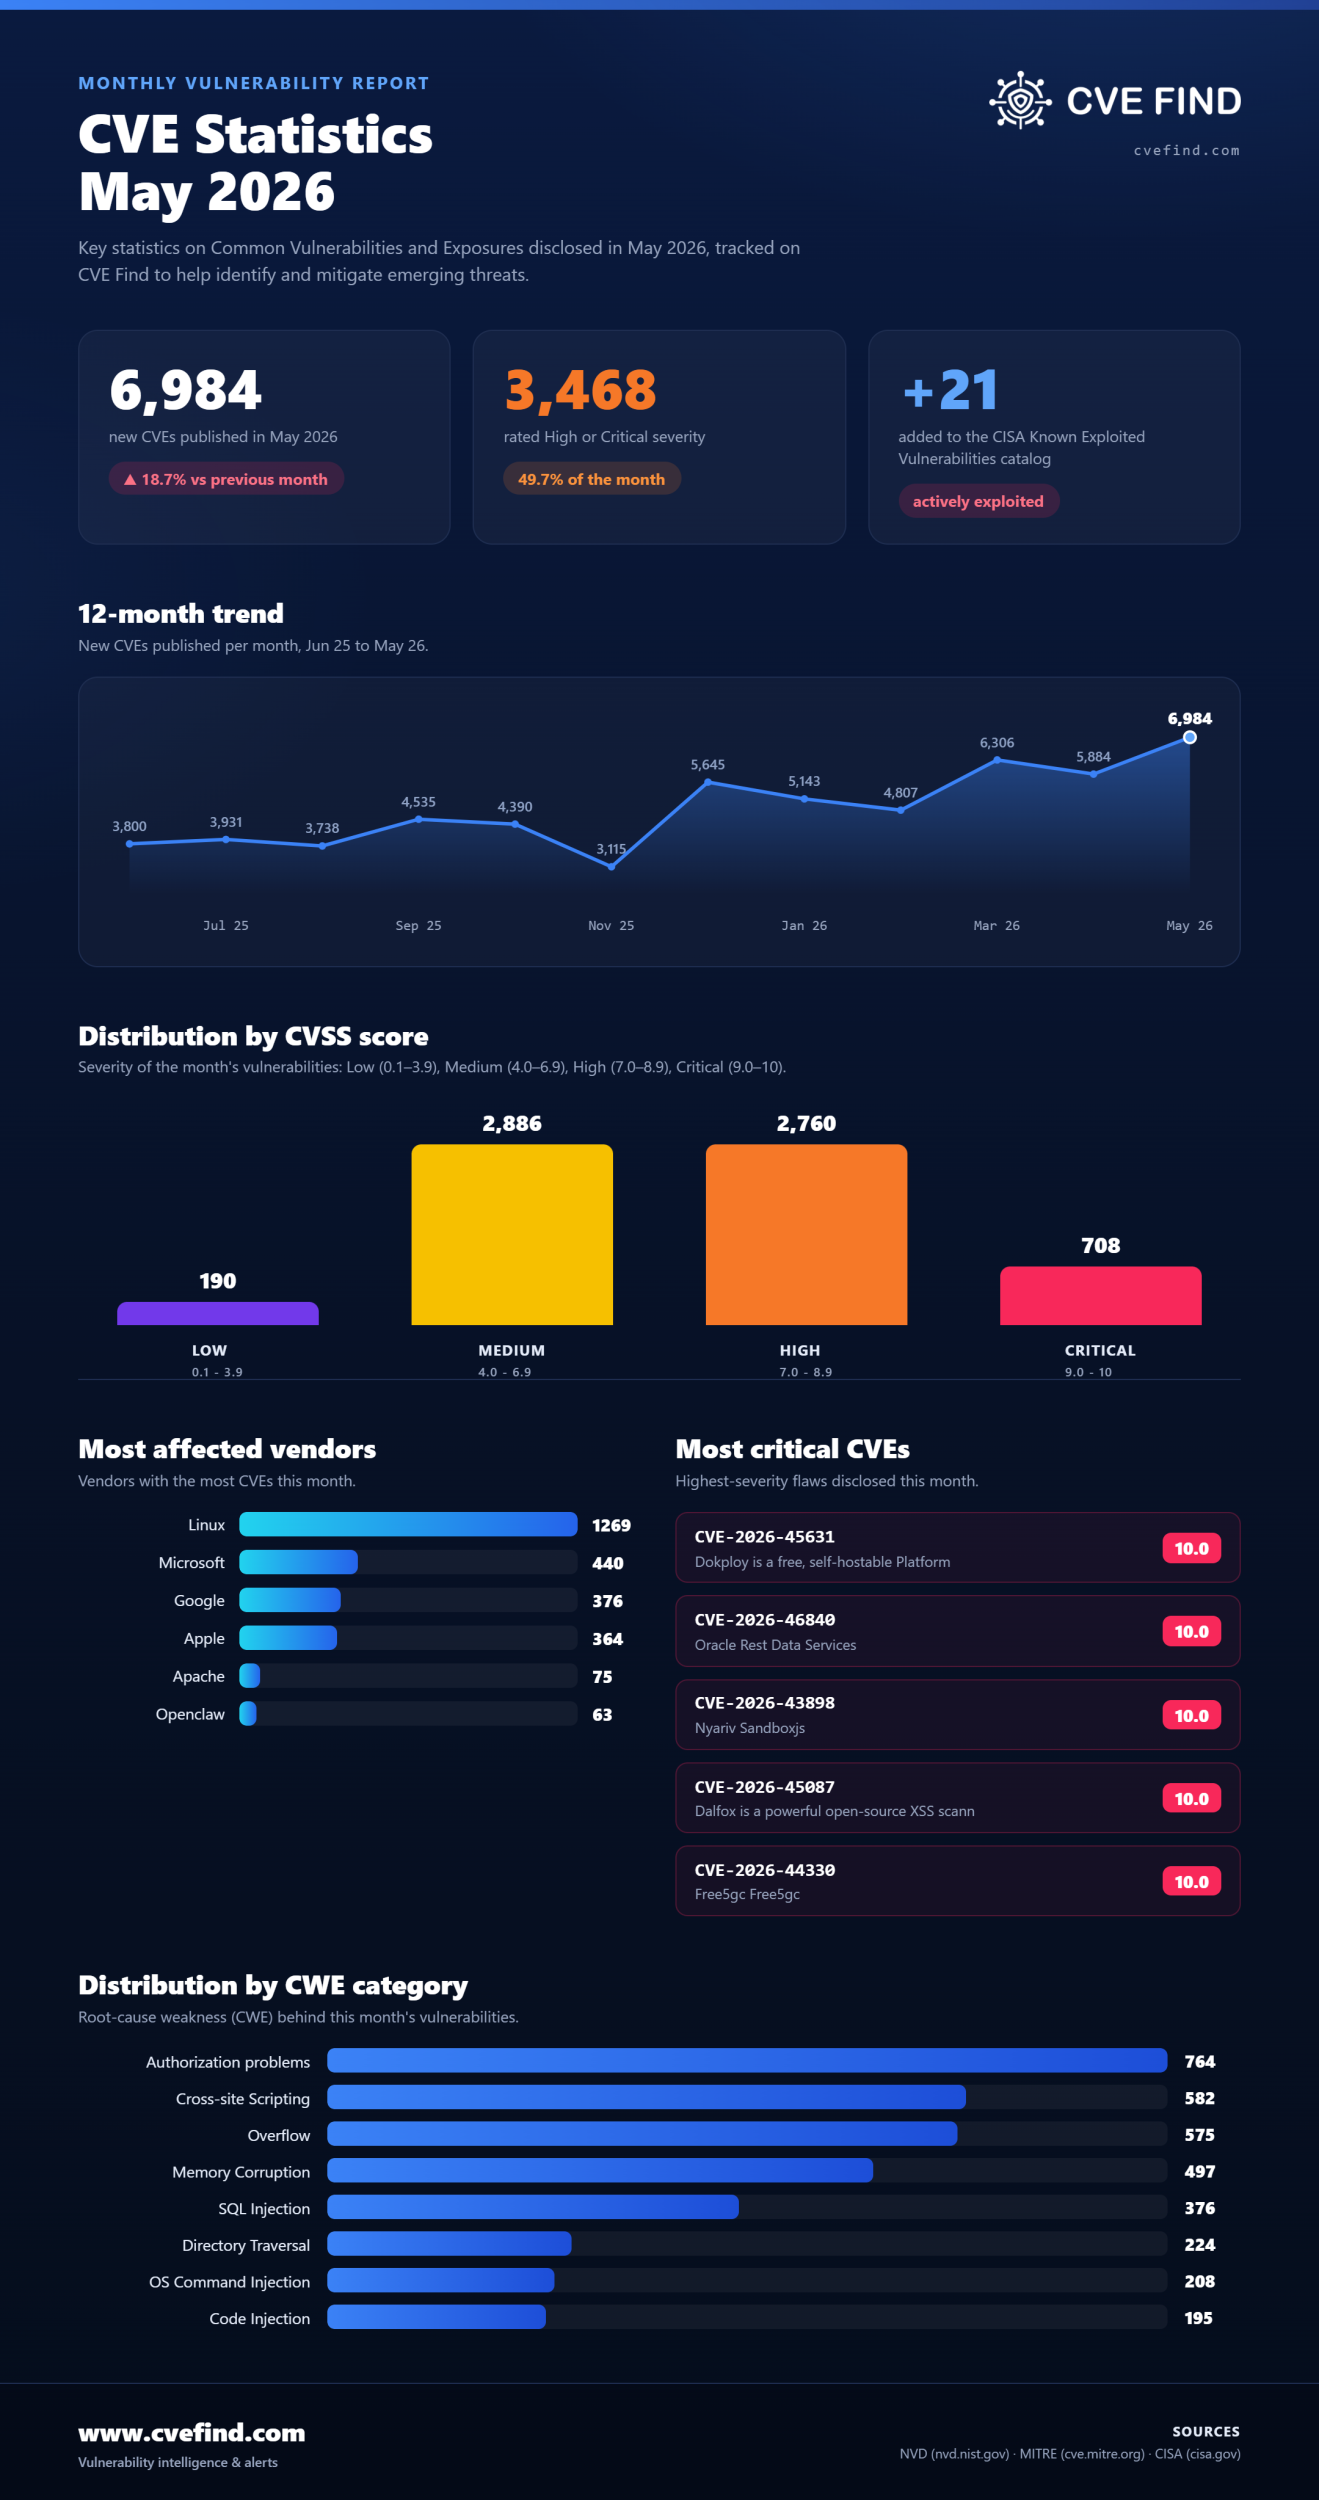
CVE Find, Bexxo's proprietary tool, integrates the MITRE, NVD and CISA KEV databases in real time and sends an alert as soon as a known vulnerability affects the client's systems. Without active monitoring, the average detection time for a network breach reaches 241 days (IBM Cost of a Data Breach 2025). CVE Find reduces that to a matter of hours.
03 Securing access and sensitive data
Bexxo audits authentication policies, assesses password strength, deploys MFA and secures administrator and VPN access. Compromised credentials are behind 22% of data breaches (Verizon DBIR 2025): the most frequent vector, and also the easiest to fix with the right measures.
Our Cybersecurity Solutions

We analyze your entire IT infrastructure to identify potential flaws and improve the security of your connections, equipment, and protocols.
Learn more

We conduct an in-depth diagnosis of your website to detect vulnerabilities and strengthen its protection against cyberattacks, such as SQL injections, XSS flaws, and brute-force attacks.
Learn more

Our experts assist you in developing and optimizing your IT security policy. Together, we define a tailored strategy to secure your systems, reduce risks, and ensure your compliance with current regulations.
Learn more

We implement advanced technologies to protect your infrastructures, networks, and sensitive data. From access management to information encryption, we ensure effective protection against cyber threats.
Learn more
Why choose Bexxo?
Latest Thinking


How we collaborate with you

Listening and understanding
An initial meeting (30–60 min) to identify your systems, sensitive data and legal obligations (Swiss DSA, ISO 27001). No jargon, we speak your language.

In-depth analysis
Manual and automated analysis of your web and network systems. Duration: 3 to 10 days depending on complexity. Result: a complete vulnerability map ranked by criticality.

Correction and reinforcement
You receive a detailed report with a prioritised action plan. Our teams can implement corrections directly or support your IT teams in the remediation process.

Permanent vigilance
Continuous monitoring via CVE Find, real-time alerts on new vulnerabilities affecting your systems, and regular follow-up reports.

Measure, train, learn: one platform, one score
Security Culture Score, PhishTrainer and Bexxo Academy work together: evaluate your security culture, test your teams' reflexes, train them in a targeted way and track progress with a global score out of 1000, broken down by organisation, groups and employees.
01 Measure
Security Culture Score evaluates your security culture.
02 Train
PhishTrainer tests reflexes with realistic simulations.
03 Learn
Bexxo Academy trains with learning paths adapted to every profile.
04 Progress
Scores measure progress and guide next steps.
Cybersecurity tailored to your challenges
Cyberattacks are becoming increasingly sophisticated and can have disastrous consequences for businesses: loss of critical data, reputational damage, regulatory penalties, and business interruptions. A structured, continuously maintained cybersecurity strategy prevents these risks.
At Bexxo, we offer tailor-made protection solutions, adapted to your needs and compliant with the most demanding security standards, such as ISO 27001/27002 and NIST. In line with NCSC recommendations, we analyze, detect, and correct vulnerabilities in your infrastructure.
Stay ahead with the latest critical security vulnerabilities.
CVE-2026-1928 - HIGH
28/10/2026
The Rank Math SEO – AI SEO Tools to Dominate SEO Rankings plugin for WordPress is vulnerable to PHP Object Injection in all versions up to, and including, 1.0.276 via deserialization of untrusted input in the updateMeta REST API endpoint. This makes it possible forauthenticated attackers, with Contributor-level access and above, to inject a PHP Object. The additional presence of a POP chain allo...
OWSAP: A08
CVE-2026-110879 - CRITICAL
28/10/2026
jackson-databind validates the outer class of a class-name type ID but accepts attacker-selected classes inside its generic arguments, even when those classes violate the declared type or would be rejected as direct type IDs. This bypasses the generic-argument validation added for CVE-2026-54512 (GHSA-j3rv-43j4-c7qm), of which this is an incomplete fix. DatabindContext._resolveAndValidateGeneri...
OWSAP: A08
CVE-2026-58256 - CRITICAL
27/10/2026
GRR is a resource management and reservation application. Prior to the advisory-reported fixed version 4.5.0, an administrator can inject malicious PHP through LDAP connector configuration parameters such as `ldap_filter`, poisoning `/personnalisation/config_ldap.inc.php` and permitting remote code execution. The administrator must first successfully connect to an LDAP server, which can be attacke...
codeinjectionOWSAP: A03
CVE-2026-58255 - HIGH
27/10/2026
Cronicle is a multi-server task scheduler and runner, with a web based front-end UI. Prior to 0.9.121, a non-administrator user or scoped API key with `create_events` and `run_events` privileges can inject top-level `uid` and `gid` fields through `/api/app/create_event` or `/api/app/update_event`. In `lib/api.js`, `requireValidEventData` uses `validateOptionalParams` as a partial allow-list that s...
priviliegemanagementauthorisationproblemOWSAP: A04OWSAP: A01OWSAP: A08
CVE-2026-85898 - HIGH
27/10/2026
Access of resource using incompatible type ('type confusion') in Microsoft Edge (Chromium-based) allows an unauthorized attacker to execute code over a network.
CVE-2026-83831 - HIGH
27/10/2026
Double free in Microsoft Edge (Chromium-based) allows an unauthorized attacker to execute code over a network.
CVE-2026-116692 - CRITICAL
27/10/2026
MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From 3.12.0rc0 until 3.17.0, third-party scorer deserialization in mlflow/genai/scorers/base.py accepts request-selected descendants of THIRD_PARTY_SCORER_ALLOWED_MODULES rather than requiring an exact allowed module. A caller can use MLflow artifact endpoints to place a Python module b...
codeinjectionOWSAP: A03
CVE-2026-112352 - CRITICAL
27/10/2026
Sunhillo SureLine before 9.1.5 contains an authentication bypass vulnerability that allows an unauthenticated remote attacker to impersonate any user with an active web session by forging a session cookie containing only a cleartext username with no random identifier or integrity protection. Attackers can guess default account names such as Admin or sftp_user and submit a forged username cookie to...
OWSAP: A08
CVE-2026-112351 - HIGH
27/10/2026
Sunhillo SureLine before 9.1.5 contains an OS command injection vulnerability in the networkDiag.cgi endpoint that allows an authenticated remote attacker with any web account to execute arbitrary commands as root by injecting shell metacharacters into the ipAddr or dnsAddr parameters. Attackers can bypass the incomplete character denylist from the prior CVE-2021-36380 fix using URL-encoded newlin...
oscommandinjectionOWSAP: A03
CVE-2026-116682 - HIGH
27/10/2026
FileBrowser Quantum is a free, self-hosted, web-based file manager. Prior to 1.5.2-stable and 2.0.1-beta, file read handling in backend/pkg/indexing/indexingFiles.go resolves symbolic links through GetRealPath without confirming that the resolved target remains inside the source root and the user's authorized scope. Download, preview, media, OnlyOffice, and public-share read flows that enable Foll...
directorytraversalOWSAP: A01
CVE-2026-116676 - HIGH
27/10/2026
Atlantis is a self-hosted golang application that listens for Terraform pull request events via webhooks. From version 0.4.0 until 0.47.1, Atlantis passes the pull-request-controlled workspace value from atlantis.yaml into Terraform command arguments that are joined with strings.Join(args, " ") and executed through sh -c. An authenticated contributor whose pull request is eligible for an Atlantis ...
oscommandinjectionOWSAP: A03
CVE-2026-108329 - HIGH
27/10/2026
Tanium addressed an unauthorized code execution vulnerability in Threat Response.
commandinjectionOWSAP: A03
CVE-2026-108303 - HIGH
27/10/2026
Tanium addressed an unauthorized code execution vulnerability in Certificate Manager.
commandinjectionOWSAP: A03
CVE-2026-48360 - CRITICAL
27/10/2026
Adobe Connect is affected by an Improper Control of Generation of Code ('Code Injection') vulnerability that could result in arbitrary code execution in the context of the current user. An attacker could exploit this vulnerability to execute arbitrary code. Exploitation of this issue requires user interaction in that a victim must visit a maliciously crafted URL or interact with a compromised web ...
codeinjectionOWSAP: A03
CVE-2026-116672 - HIGH
27/10/2026
Authlib is a Python library which builds OAuth and OpenID Connect servers. From 0.15 until 1.9.1, the documented ClientConfigurationEndpoint.authenticate_client and ClientConfigurationEndpoint.check_permission reference implementations look up a target client from request-controlled client_id data and check only whether that target is editable, without verifying that request.credential belongs to ...
authorisationproblemOWSAP: A01
CVE-2026-114596 - HIGH
27/10/2026
In EPICS Base release 7.0.10 and prior, an improper validation of message length values during protocol parsing can trigger an integer overflow, resulting in an out-of-bounds memory write. Successful exploitation can cause process instability or denial of service.
CVE-2026-114595 - CRITICAL
27/10/2026
In EPICS Base release 7.0.10 and prior, an integer overflow in network request processing can cause memory to be allocated with an incorrect size. Subsequent handling of attacker supplied data may result in memory corruption, denial of service, or potential remote code execution.
CVE-2026-112353 - HIGH
27/10/2026
GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component that allows a remote attacker to run JavaScript in a victim's authenticated Webmail session by uploading a crafted SVG email attachment that bypasses sanitization of event-handler attributes. Attackers can exploit the temporary-download endpoint's insufficient Conten...
crosssitescriptingOWSAP: A03
CVE-2026-105781 - CRITICAL
27/10/2026
Adobe Campaign Classic (ACC) is affected by an Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability that could result in arbitrary code execution in the context of the current user. An attacker could exploit this vulnerability to execute arbitrary SQL commands, potentially gaining elevated access or control over the victim's account or session. Exploit...
sqlinjectionOWSAP: A03
CVE-2026-105780 - CRITICAL
27/10/2026
Adobe Campaign Classic (ACC) is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in the context of the current user. A low-privileged attacker could exploit this vulnerability to execute arbitrary code. Exploitation of this issue does not require user interaction. Scope is changed.
authorisationproblemOWSAP: A01