CVE Statistics: August 2026
- September 01, 2026
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in August 2026 on CVE Find.
🔎 Overview
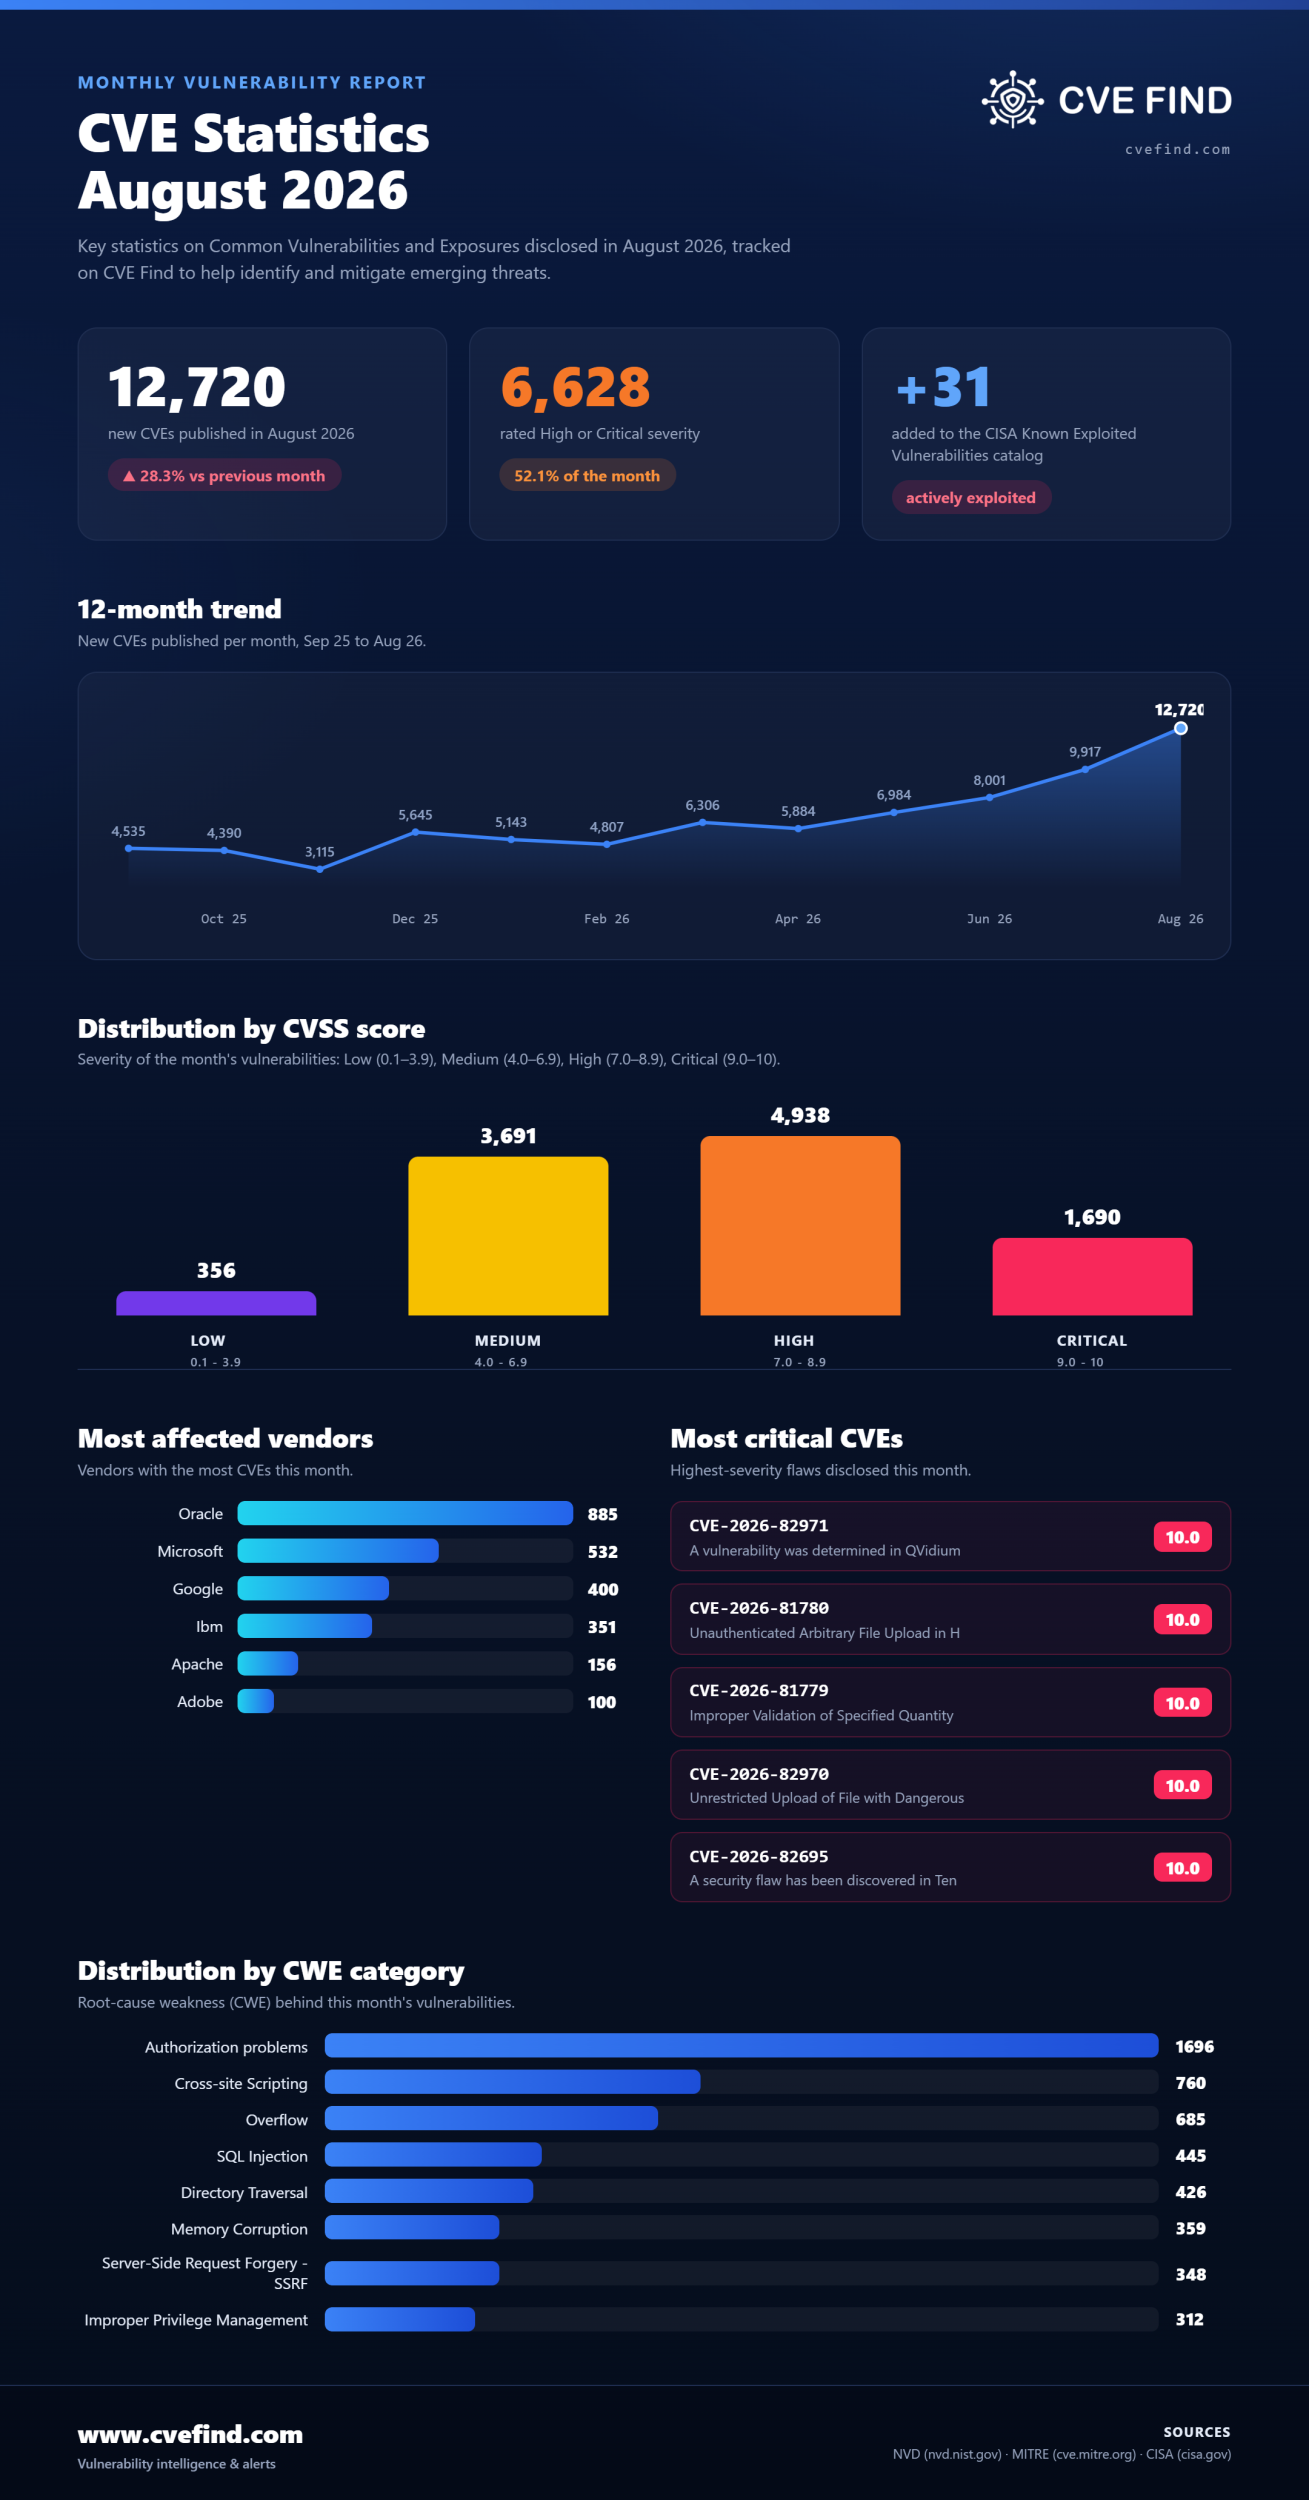
- Total number of CVEs published : 12,720 (+28.3% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 31
📂 Breakdown by main categories
- Authorization problems : 1696
- Cross-site Scripting : 760
- Overflow : 685
- SQL Injection : 445
- Directory Traversal : 426
- Memory Corruption : 359
📈 Breakdown by CVSS score
- Low : 356
- Medium : 3691
- High : 4938
- Critical : 1690
🏢 Most affected vendors
📦 Most affected products
- google chrome : 396
- microsoft windows_server_2025 : 216
- microsoft windows_11_26h1 : 200
- microsoft windows_11_24h2 : 197
- microsoft windows_11_25h2 : 197
⚠️ Notable CVEs of the month
- CVE-2026-82971 (10 CRITICAL) : A vulnerability was determined in QVidium Opera11 3.3.2a26-Ax4x-opera11. This affects an unknown part of the file /cgi-bin/net_tr.cgi of the component CGI Script. This manipulat...
- CVE-2026-81780 (10 CRITICAL) : Unauthenticated Arbitrary File Upload in Hash Form <= 1.4.2 versions.
- CVE-2026-81779 (10 CRITICAL) : Improper Validation of Specified Quantity in Input vulnerability in Silk Themes Newspapers X allows Malicious Software Implanted. This issue affects Newspapers X: from 1.0.46 t...
- CVE-2026-82970 (10 CRITICAL) : Unrestricted Upload of File with Dangerous Type vulnerability in WP Legal Pages WP Cookie Notice for GDPR, CCPA & ePrivacy Consent allows Using Malicious Files. This issue affe...
- CVE-2026-82695 (10 CRITICAL) : A security flaw has been discovered in Tenda AC18 15.03.05.19. Impacted is an unknown function of the file /goform/telnet of the component Telnet Handler. The manipulation resul...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
