CVE Statistics: July 2025
- August 01, 2025
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in July 2025 on CVE Find.
🔎 Overview
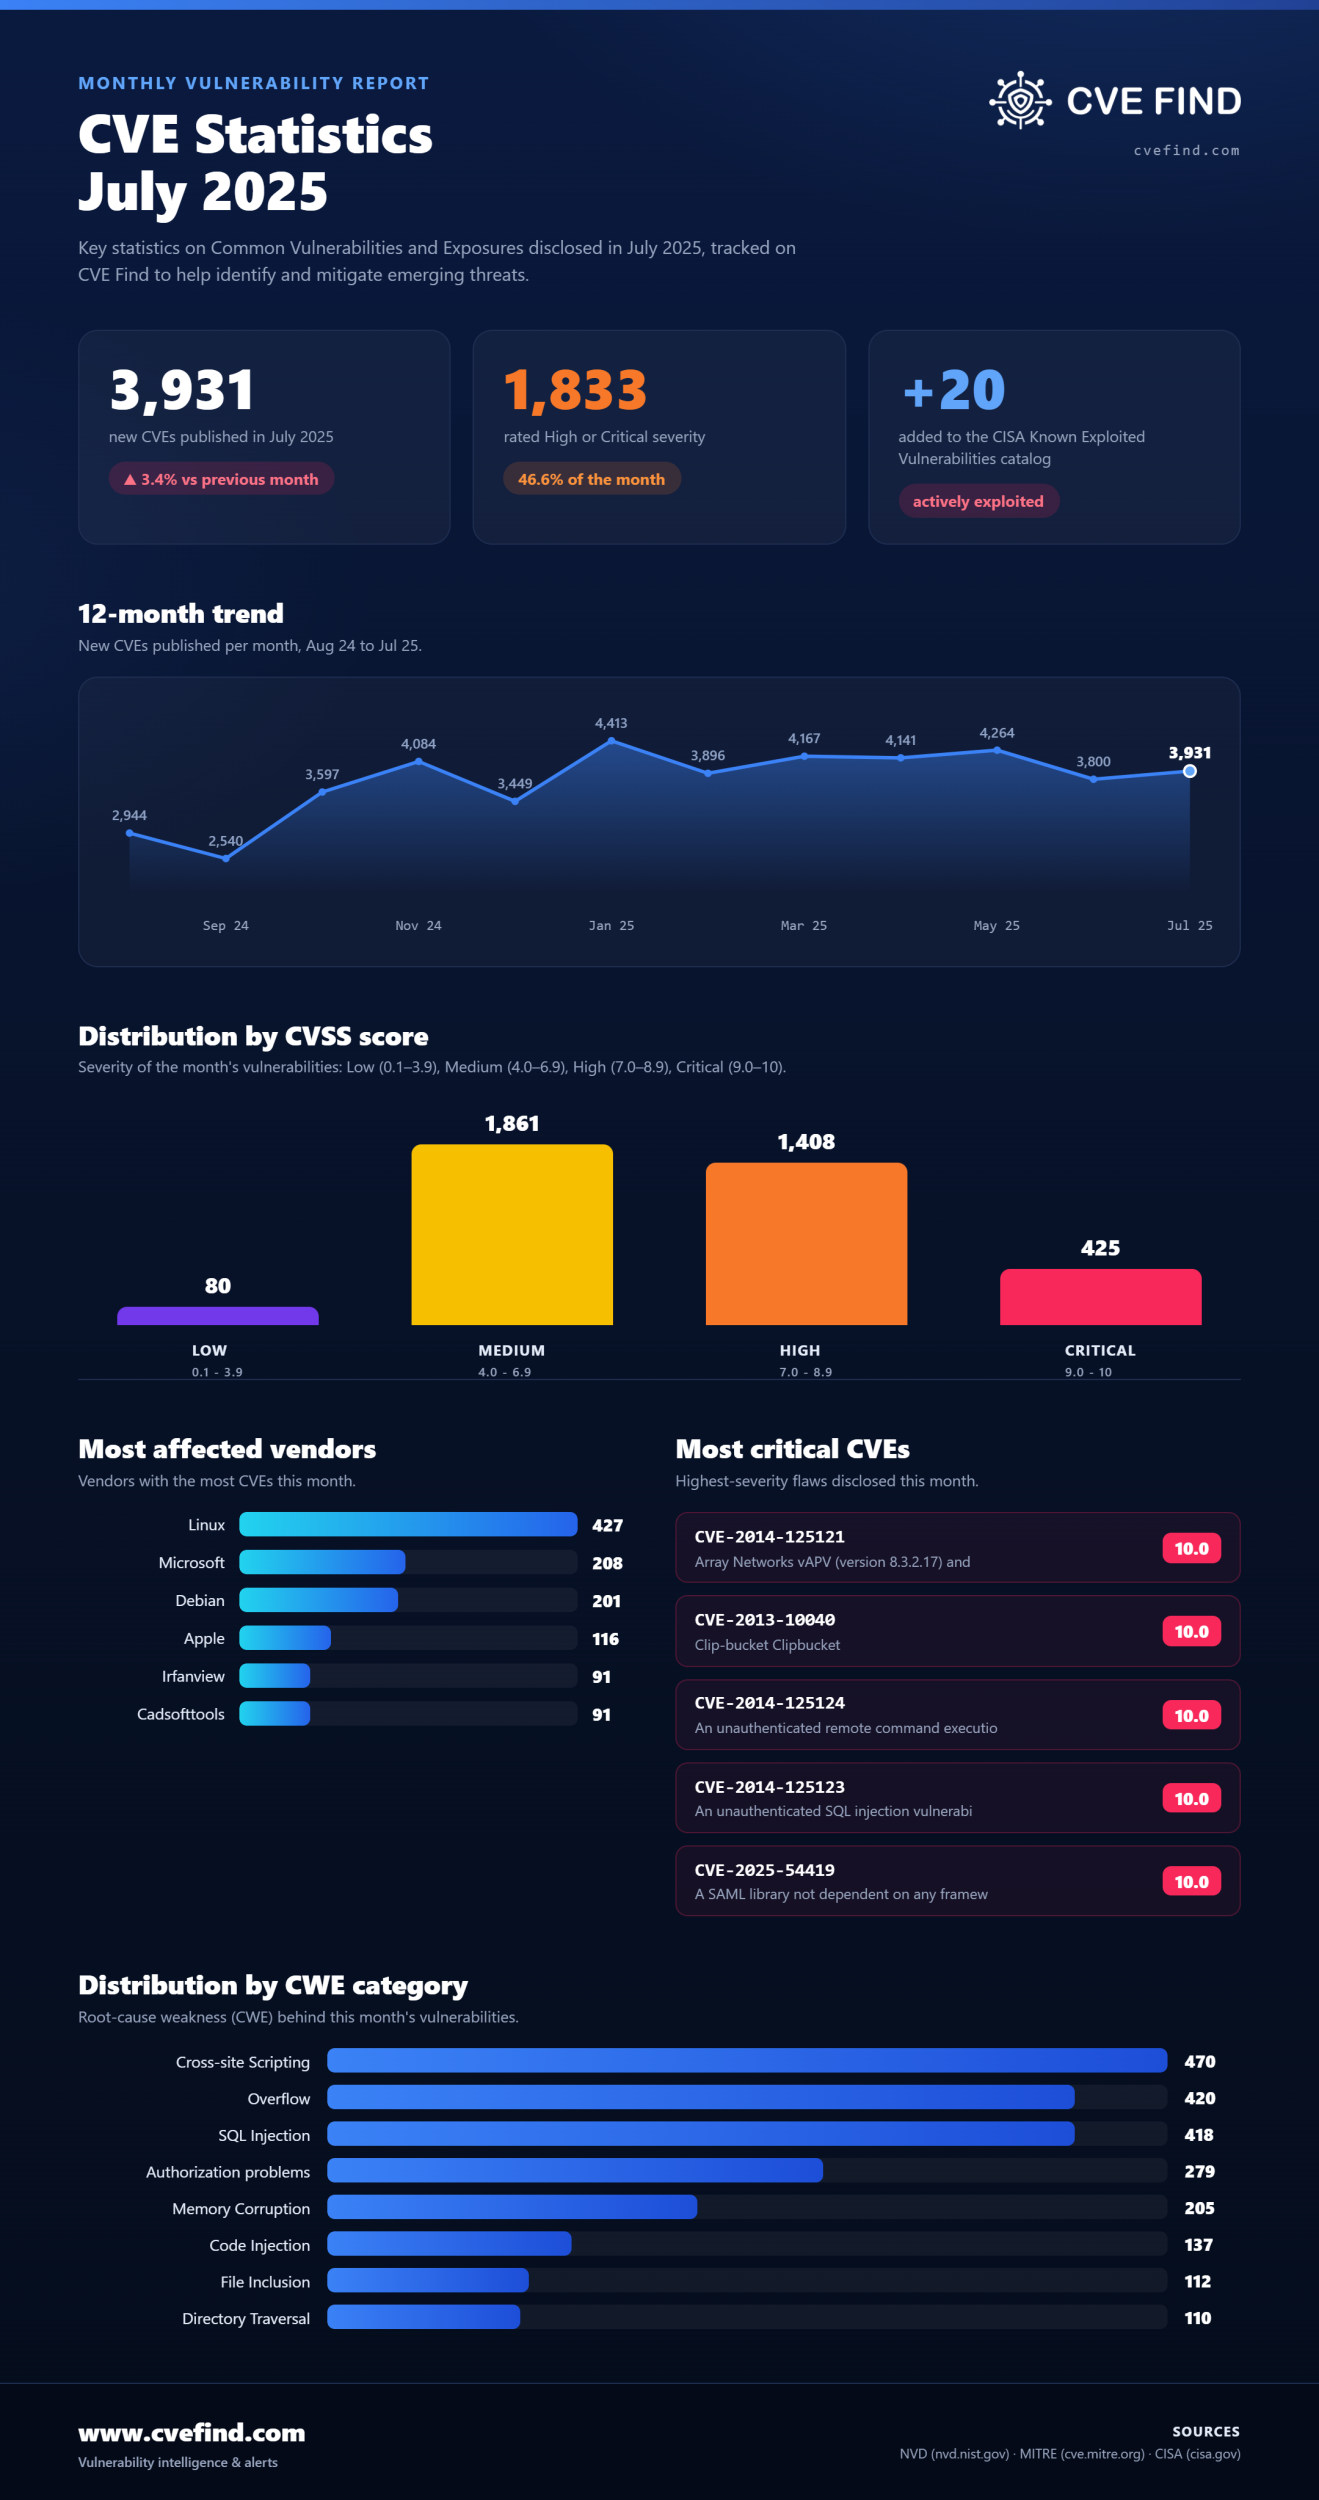
- Total number of CVEs published : 3,931 (+3.4% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 20
📂 Breakdown by main categories
- Cross-site Scripting : 470
- Overflow : 420
- SQL Injection : 418
- Authorization problems : 279
- Memory Corruption : 205
- Code Injection : 137
📈 Breakdown by CVSS score
- Low : 80
- Medium : 1861
- High : 1408
- Critical : 425
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 427
- debian debian_linux : 200
- apple macos : 110
- microsoft windows_server_2025 : 97
- microsoft windows_server_2022_23h2 : 94
⚠️ Notable CVEs of the month
- CVE-2014-125121 (10 CRITICAL) : Array Networks vAPV (version 8.3.2.17) and vxAG (version 9.2.0.34) appliances are affected by a privilege escalation vulnerability caused by a combination of hardcoded SSH crede...
- CVE-2013-10040 (10 CRITICAL) : ClipBucket version 2.6 and earlier contains a critical vulnerability in the ofc_upload_image.php script located at /admin_area/charts/ofc-library/. This endpoint allows unauthen...
- CVE-2014-125124 (10 CRITICAL) : An unauthenticated remote command execution vulnerability exists in Pandora FMS versions up to and including 5.0RC1 via the Anyterm web interface, which listens on TCP port 8023...
- CVE-2014-125123 (10 CRITICAL) : An unauthenticated SQL injection vulnerability exists in the Kloxo web hosting control panel (developed by LXCenter) prior to version 6.1.12. The flaw resides in the login-name ...
- CVE-2025-54419 (10 CRITICAL) : A SAML library not dependent on any frameworks that runs in Node. In version 5.0.1, Node-SAML loads the assertion from the (unsigned) original response document. This is differe...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
