CVE Statistics: May 2026
- June 01, 2026
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in May 2026 on CVE Find.
🔎 Overview
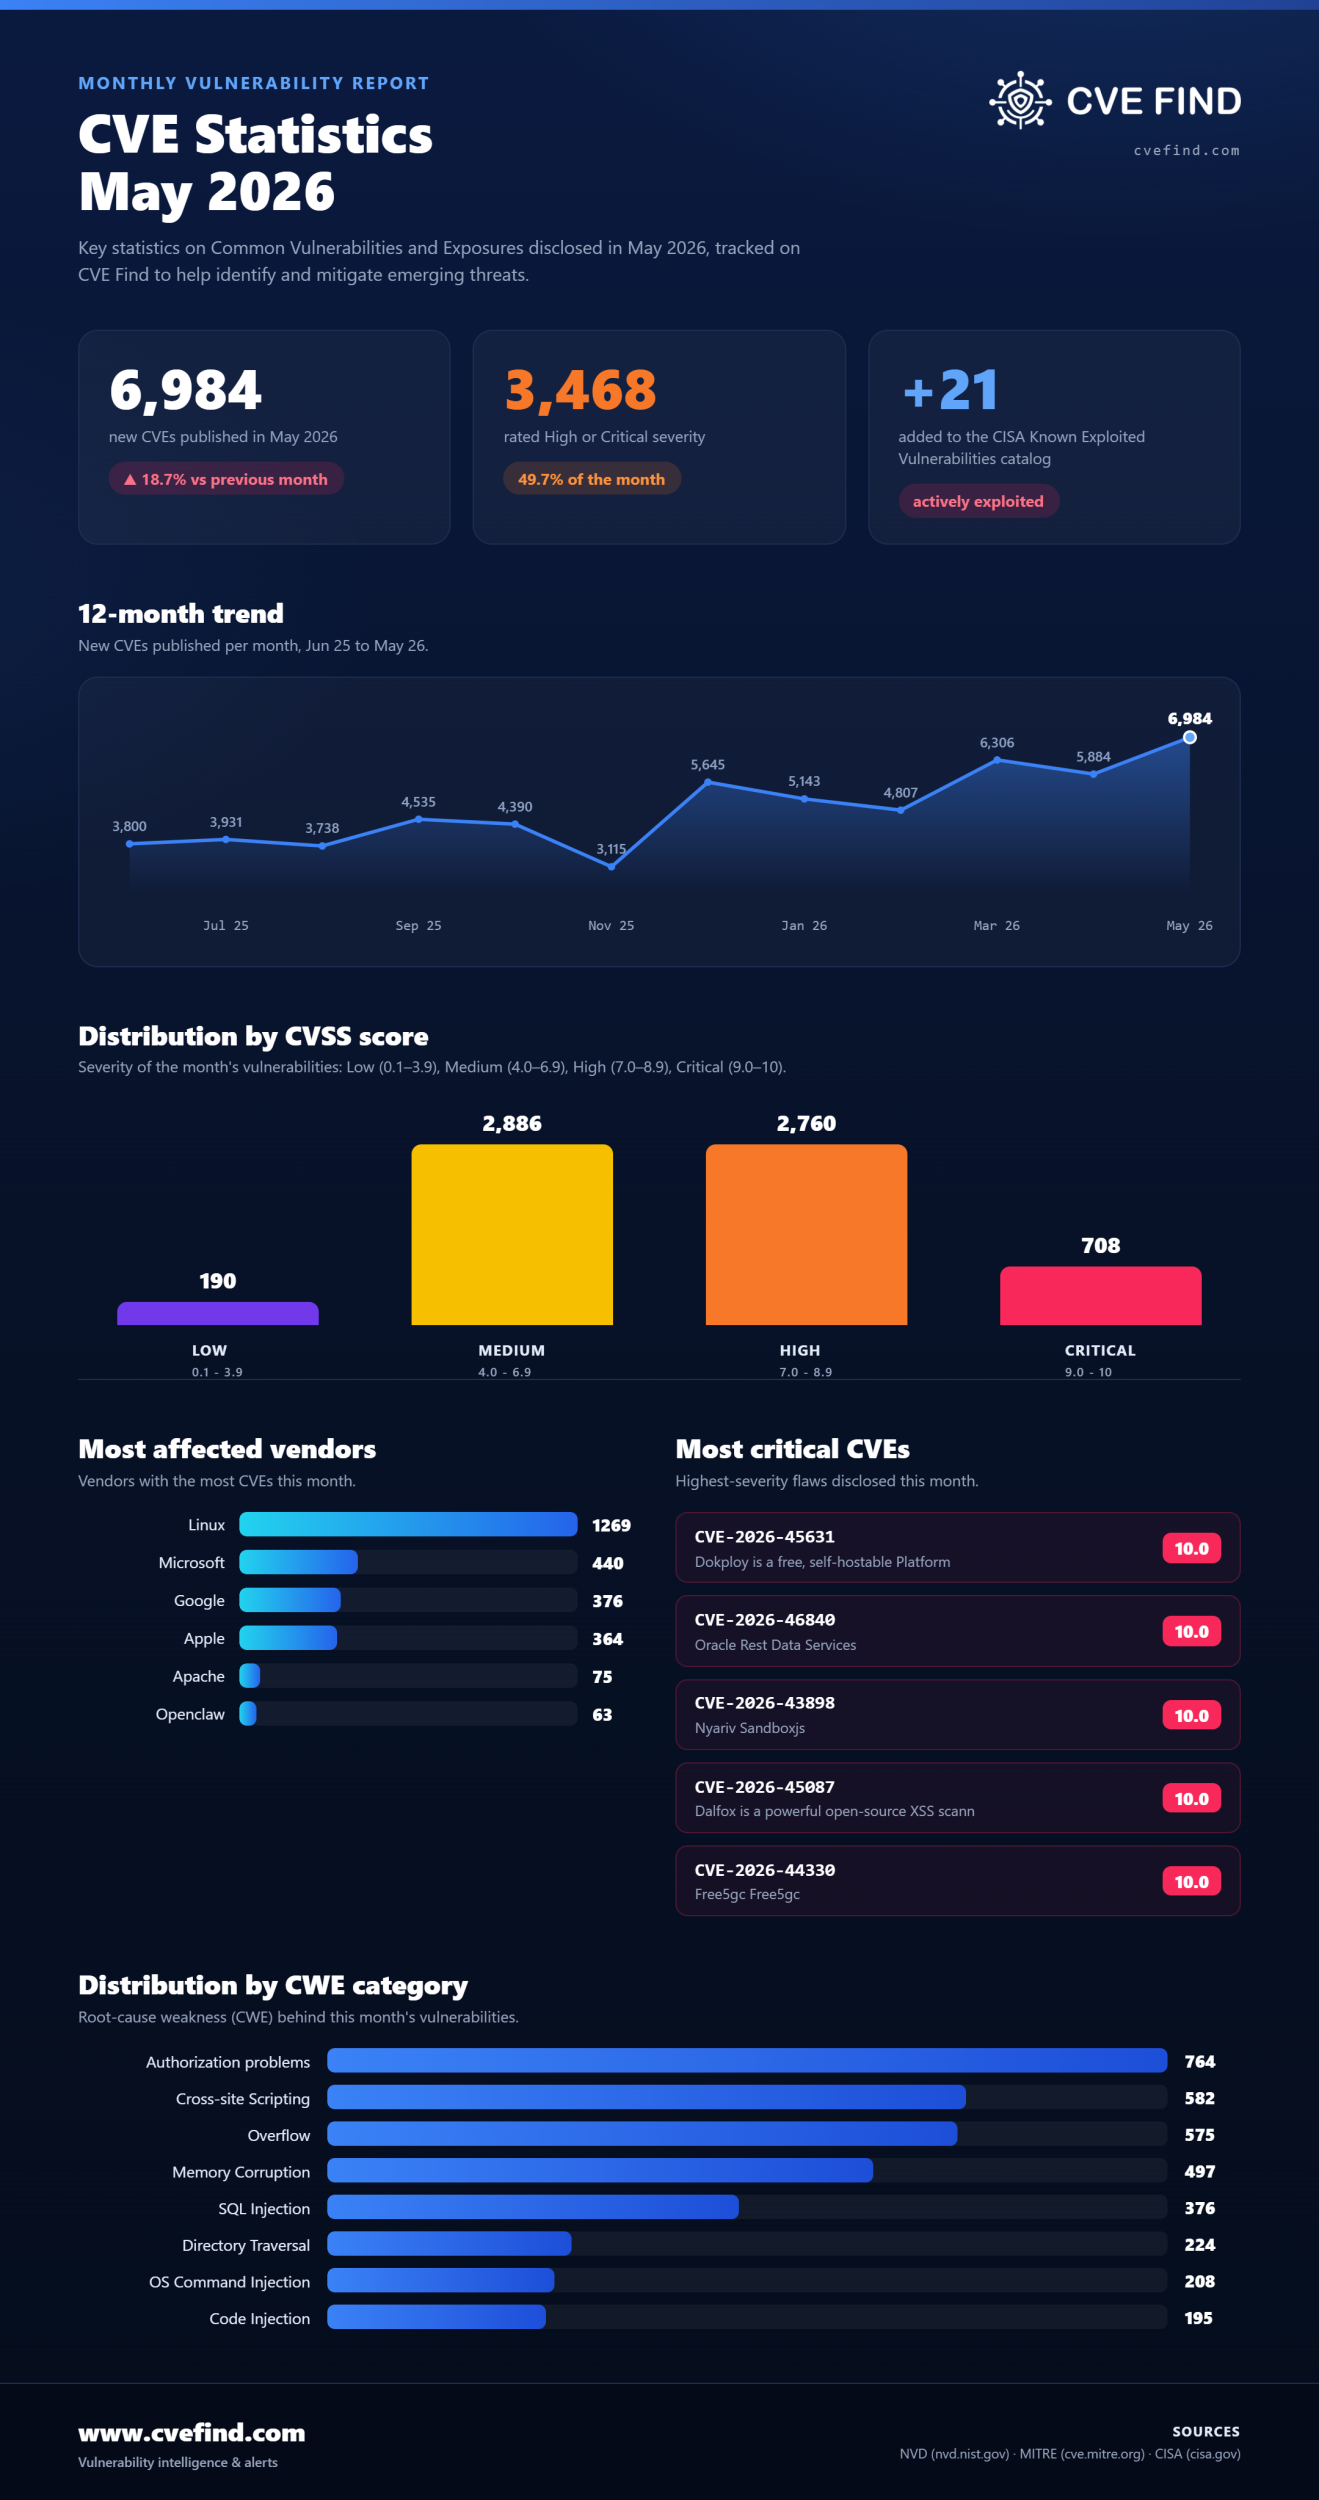
- Total number of CVEs published : 6,984 (+18.7% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 21
📂 Breakdown by main categories
- Authorization problems : 764
- Cross-site Scripting : 582
- Overflow : 575
- Memory Corruption : 497
- SQL Injection : 376
- Directory Traversal : 224
📈 Breakdown by CVSS score
- Low : 190
- Medium : 2886
- High : 2760
- Critical : 708
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 1269
- google chrome : 368
- apple macos : 346
- microsoft windows : 283
- apple iphone_os : 81
⚠️ Notable CVEs of the month
- CVE-2026-45631 (10 CRITICAL) : Dokploy is a free, self-hostable Platform as a Service (PaaS). From 0.27.0 to before 0.29.3, a hardcoded BETTER_AUTH_SECRET fallback ("better-auth-secret-123456789") lets an una...
- CVE-2026-46840 (10 CRITICAL) : Vulnerability in Oracle REST Data Services (component: Backend-as-a-Service). Supported versions that are affected are 24.2.0-26.1.0. Easily exploitable vulnerability allows un...
- CVE-2026-43898 (10 CRITICAL) : SandboxJS is a JavaScript sandboxing library. Prior to 0.9.6, sandbox-defined functions expose Function.caller, allowing sandboxed code to recover the internal LispType.Call run...
- CVE-2026-45087 (10 CRITICAL) : Dalfox is a powerful open-source XSS scanner and utility focused on automation. Prior to 2.13.0, when dalfox is started in REST API server mode (dalfox server), the server binds...
- CVE-2026-44330 (10 CRITICAL) : free5GC is an open-source implementation of the 5G core network. Prior to 4.2.2, free5GC's NEF mounts the nnef-pfdmanagement route group without inbound OAuth2/bearer-token auth...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
