CVE Statistics: September 2025
- October 01, 2025
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in September 2025 on CVE Find.
🔎 Overview
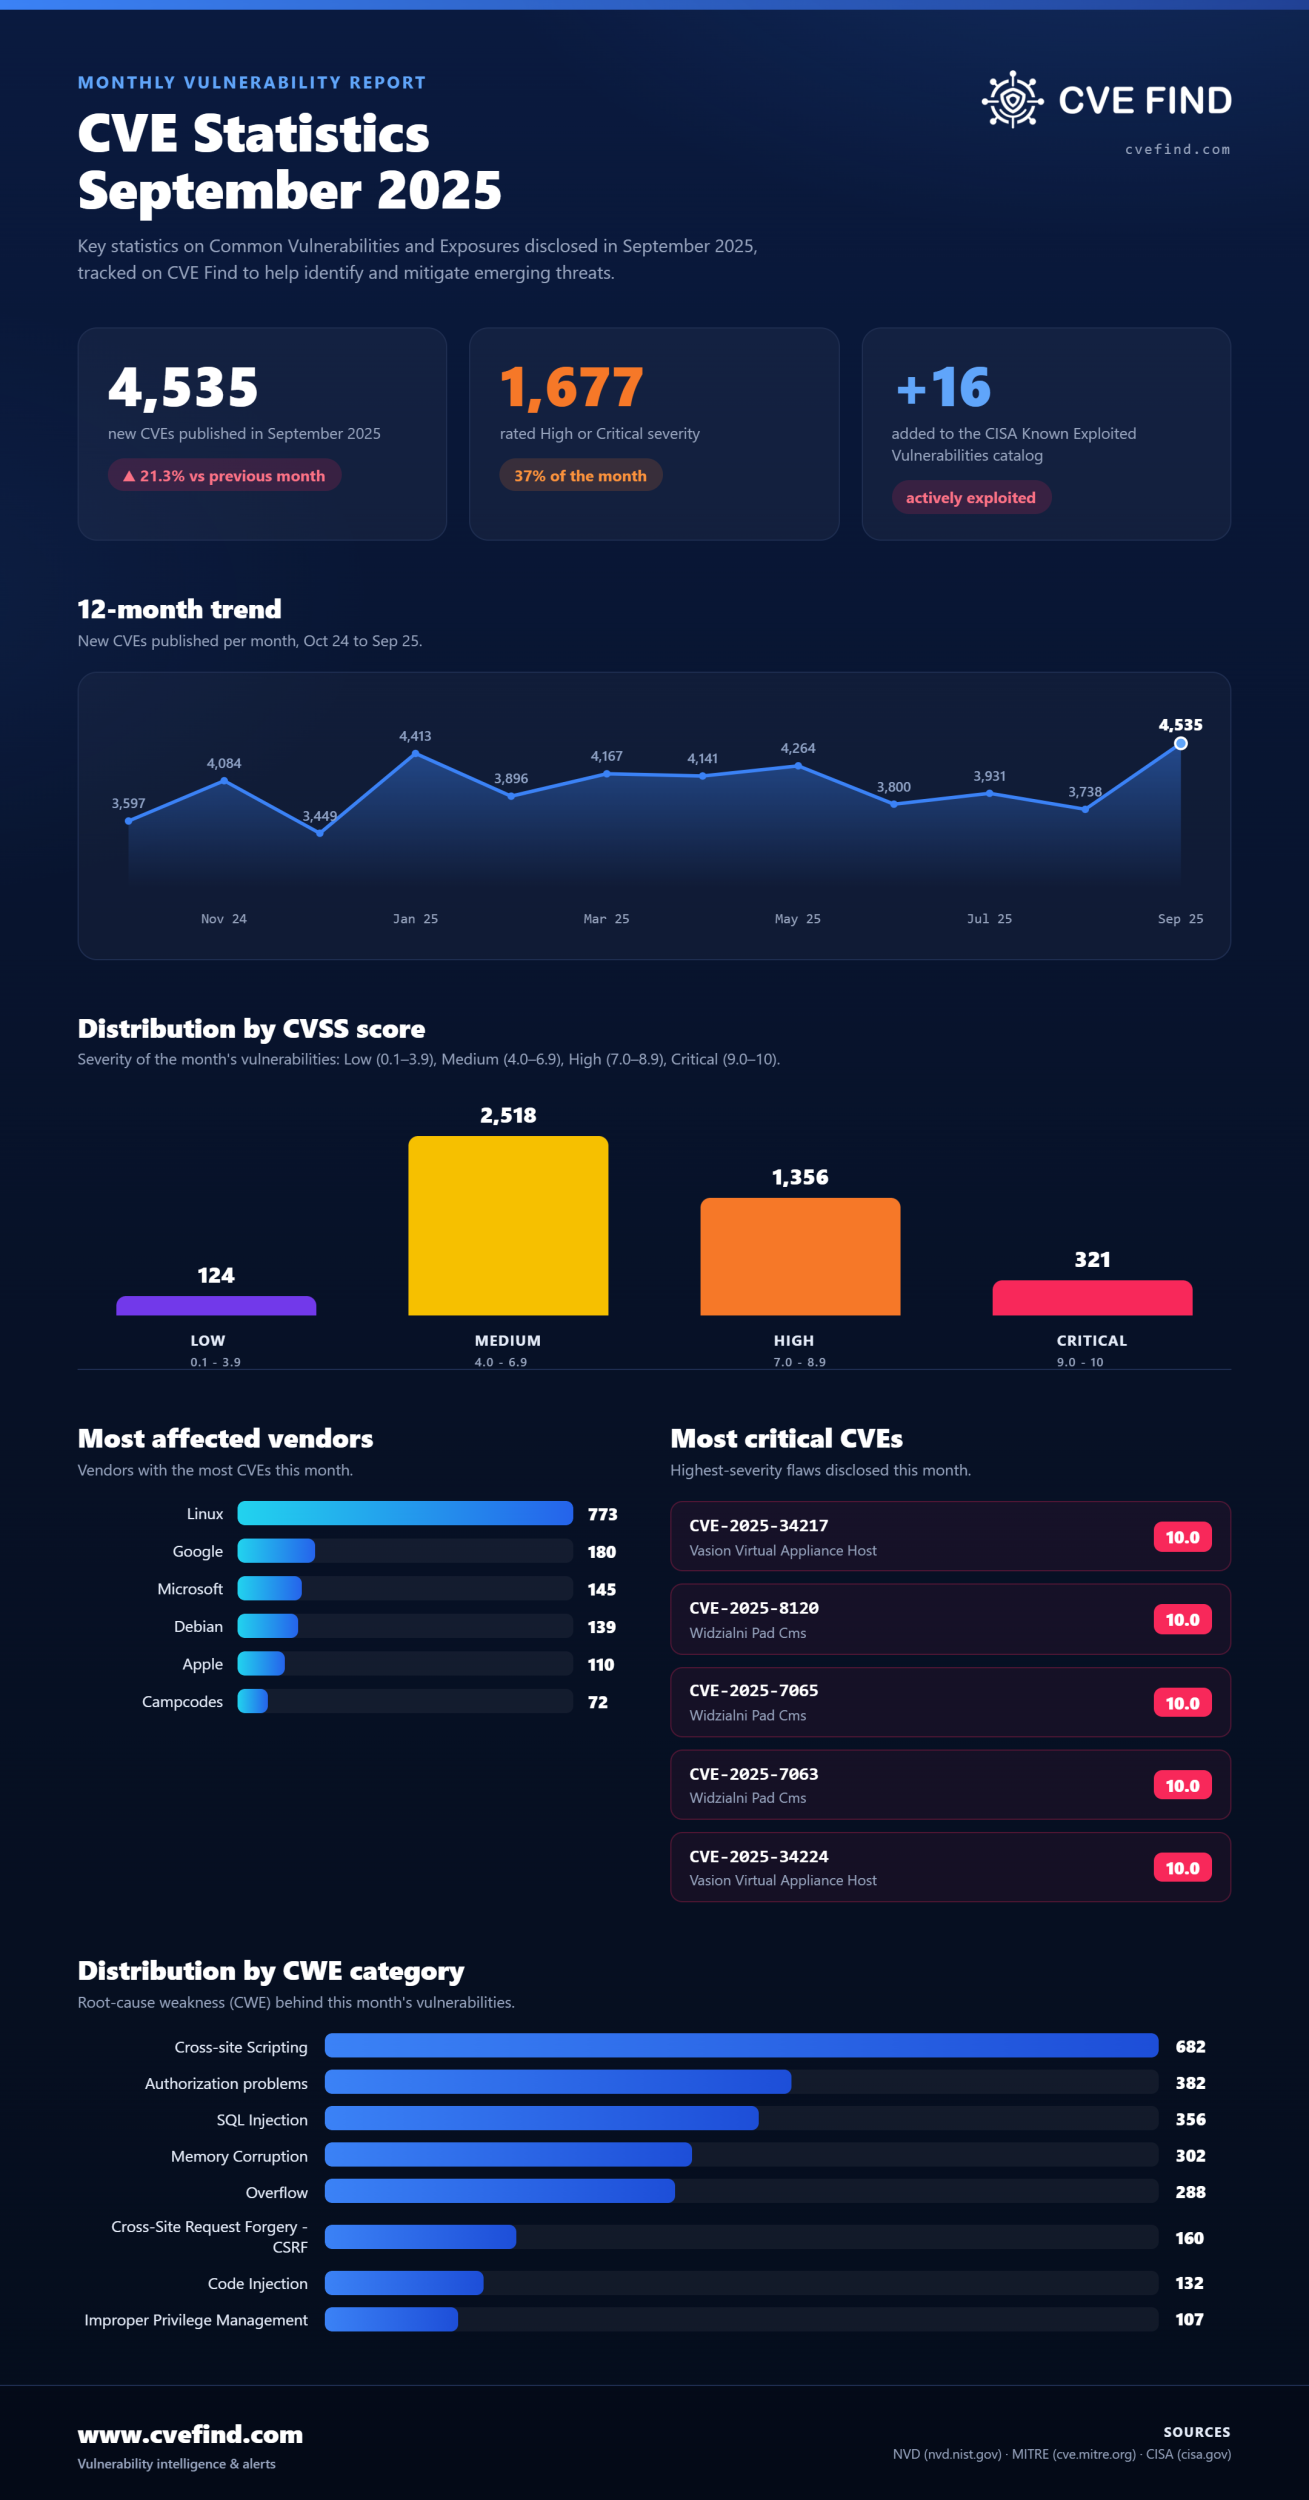
- Total number of CVEs published : 4,535 (+21.3% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 16
📂 Breakdown by main categories
- Cross-site Scripting : 682
- Authorization problems : 382
- SQL Injection : 356
- Memory Corruption : 302
- Overflow : 288
- Cross-Site Request Forgery - CSRF : 160
📈 Breakdown by CVSS score
- Low : 124
- Medium : 2518
- High : 1356
- Critical : 321
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 773
- google android : 169
- debian debian_linux : 139
- apple macos : 102
- microsoft windows_server_2025 : 59
⚠️ Notable CVEs of the month
- CVE-2025-34217 (10 CRITICAL) : Vasion Print (formerly PrinterLogic) Virtual Appliance Host and Application (VA/SaaS deployments) contain an undocumented 'printerlogic' user with a hardcoded SSH public key in ...
- CVE-2025-8120 (10 CRITICAL) : Due to client-controlled permission check parameter, PAD CMS's upload photo functionality allows an unauthenticated remote attacker to upload files of any type and extension wit...
- CVE-2025-7065 (10 CRITICAL) : Due to client-controlled permission check parameter, PAD CMS's photo upload functionality allows an unauthenticated remote attacker to upload files of any type and extension wit...
- CVE-2025-7063 (10 CRITICAL) : Due to client-controlled permission check parameter, PAD CMS's file upload functionality allows an unauthenticated remote attacker to upload files of any type and extension with...
- CVE-2025-34224 (10 CRITICAL) : Vasion Print (formerly PrinterLogic) Virtual Appliance Host prior to version 22.0.1049 and Application prior to version 20.0.2786 (VA/SaaS deployments) expose a set of PHP scrip...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
