CVE Statistics: September 2026
- October 27, 2026
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in September 2026 on CVE Find.
🔎 Overview
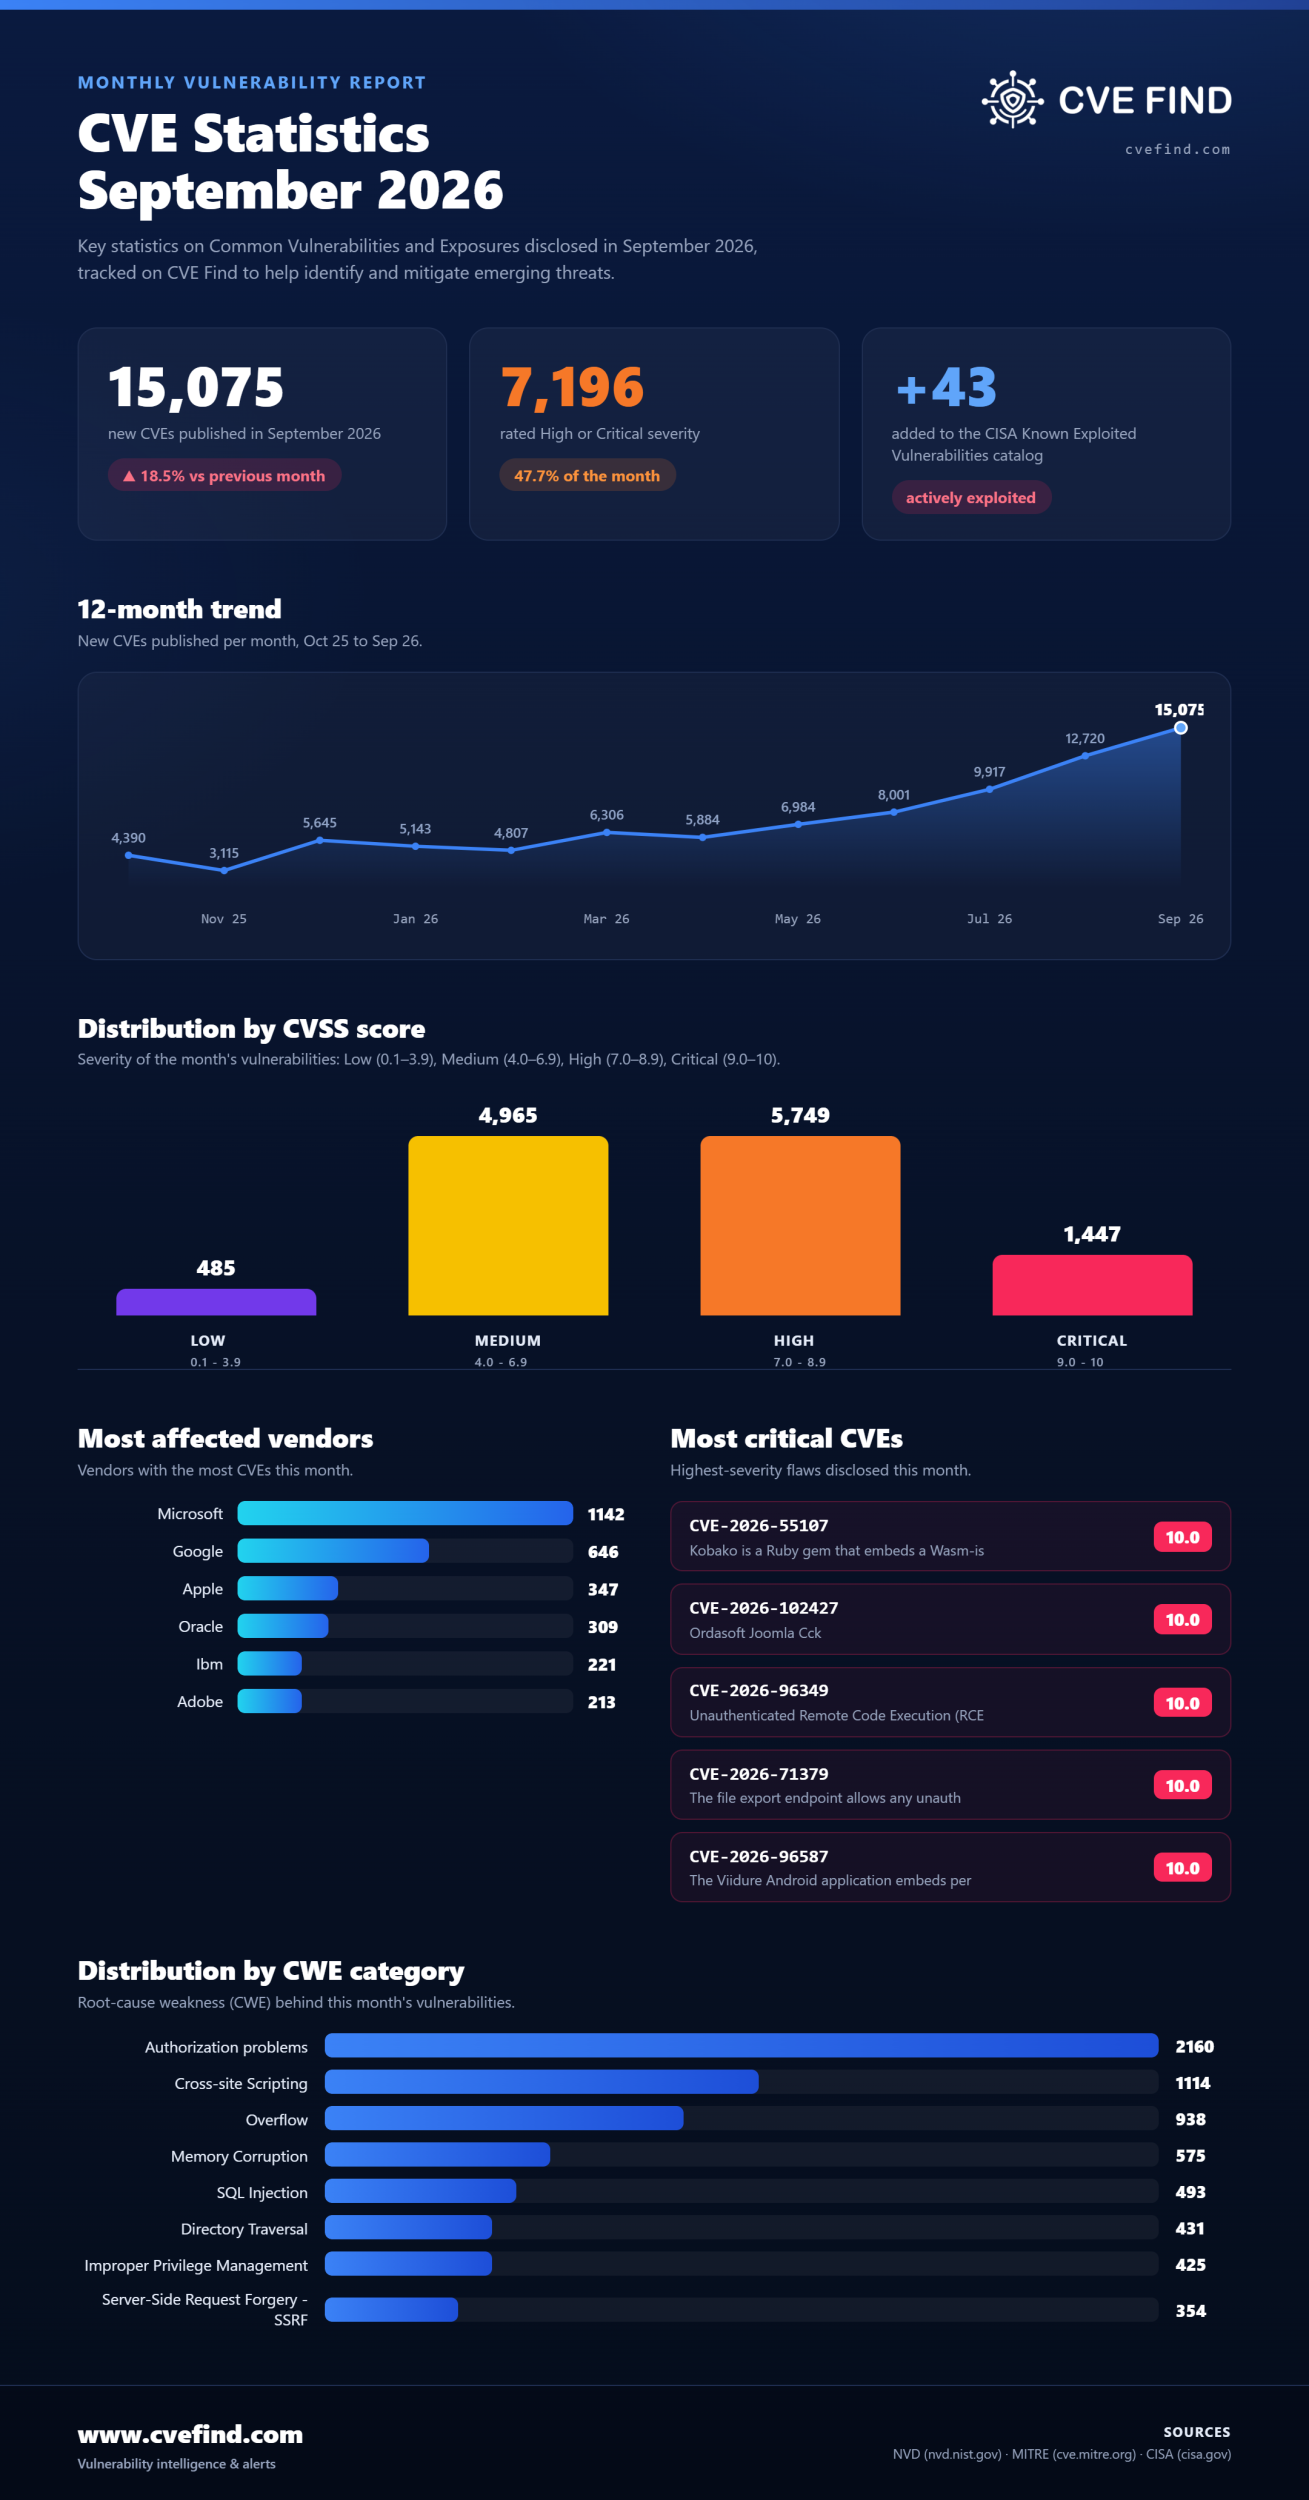
- Total number of CVEs published : 15,075 (+18.5% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 43
📂 Breakdown by main categories
- Authorization problems : 2160
- Cross-site Scripting : 1114
- Overflow : 938
- Memory Corruption : 575
- SQL Injection : 493
- Directory Traversal : 431
📈 Breakdown by CVSS score
- Low : 485
- Medium : 4965
- High : 5749
- Critical : 1447
🏢 Most affected vendors
📦 Most affected products
- microsoft windows_server_2025 : 679
- microsoft windows_server_2022 : 641
- microsoft windows_11_24h2 : 631
- microsoft windows_11_26h1 : 631
- microsoft windows_11_25h2 : 630
⚠️ Notable CVEs of the month
- CVE-2026-55107 (10 CRITICAL) : Kobako is a Ruby gem that embeds a Wasm-isolated mruby interpreter inside applications, allowing execution of untrusted Ruby scripts (LLM-generated code, user formulas, student ...
- CVE-2026-102427 (10 CRITICAL) : Joomla Extension - ordasoft.com - Unauthenticated Remote Code Execution in OrdaSoft Joomla CCK < 8.3.16 - site/uploader.php is reached through the component’s normal frontend ro...
- CVE-2026-96349 (10 CRITICAL) : Unauthenticated Remote Code Execution (RCE) in SiteSkite <= 2.1.8 versions.
- CVE-2026-71379 (10 CRITICAL) : The file export endpoint allows any unauthenticated attacker to export arbitrary database tables by sending a crafted POST request.
- CVE-2026-96587 (10 CRITICAL) : The Viidure Android application embeds permanent, plaintext cloud storage credentials within its compiled code. These credentials provide full access to critical platform storag...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
