Statistiche CVE: febbraio 2026
- 02 marzo 2026
- Temps de lecture: 3 min min
🌐 Scopri le cifre chiave delle vulnerabilità pubblicate a febbraio 2026 su CVE Find.
🔎 Panoramica
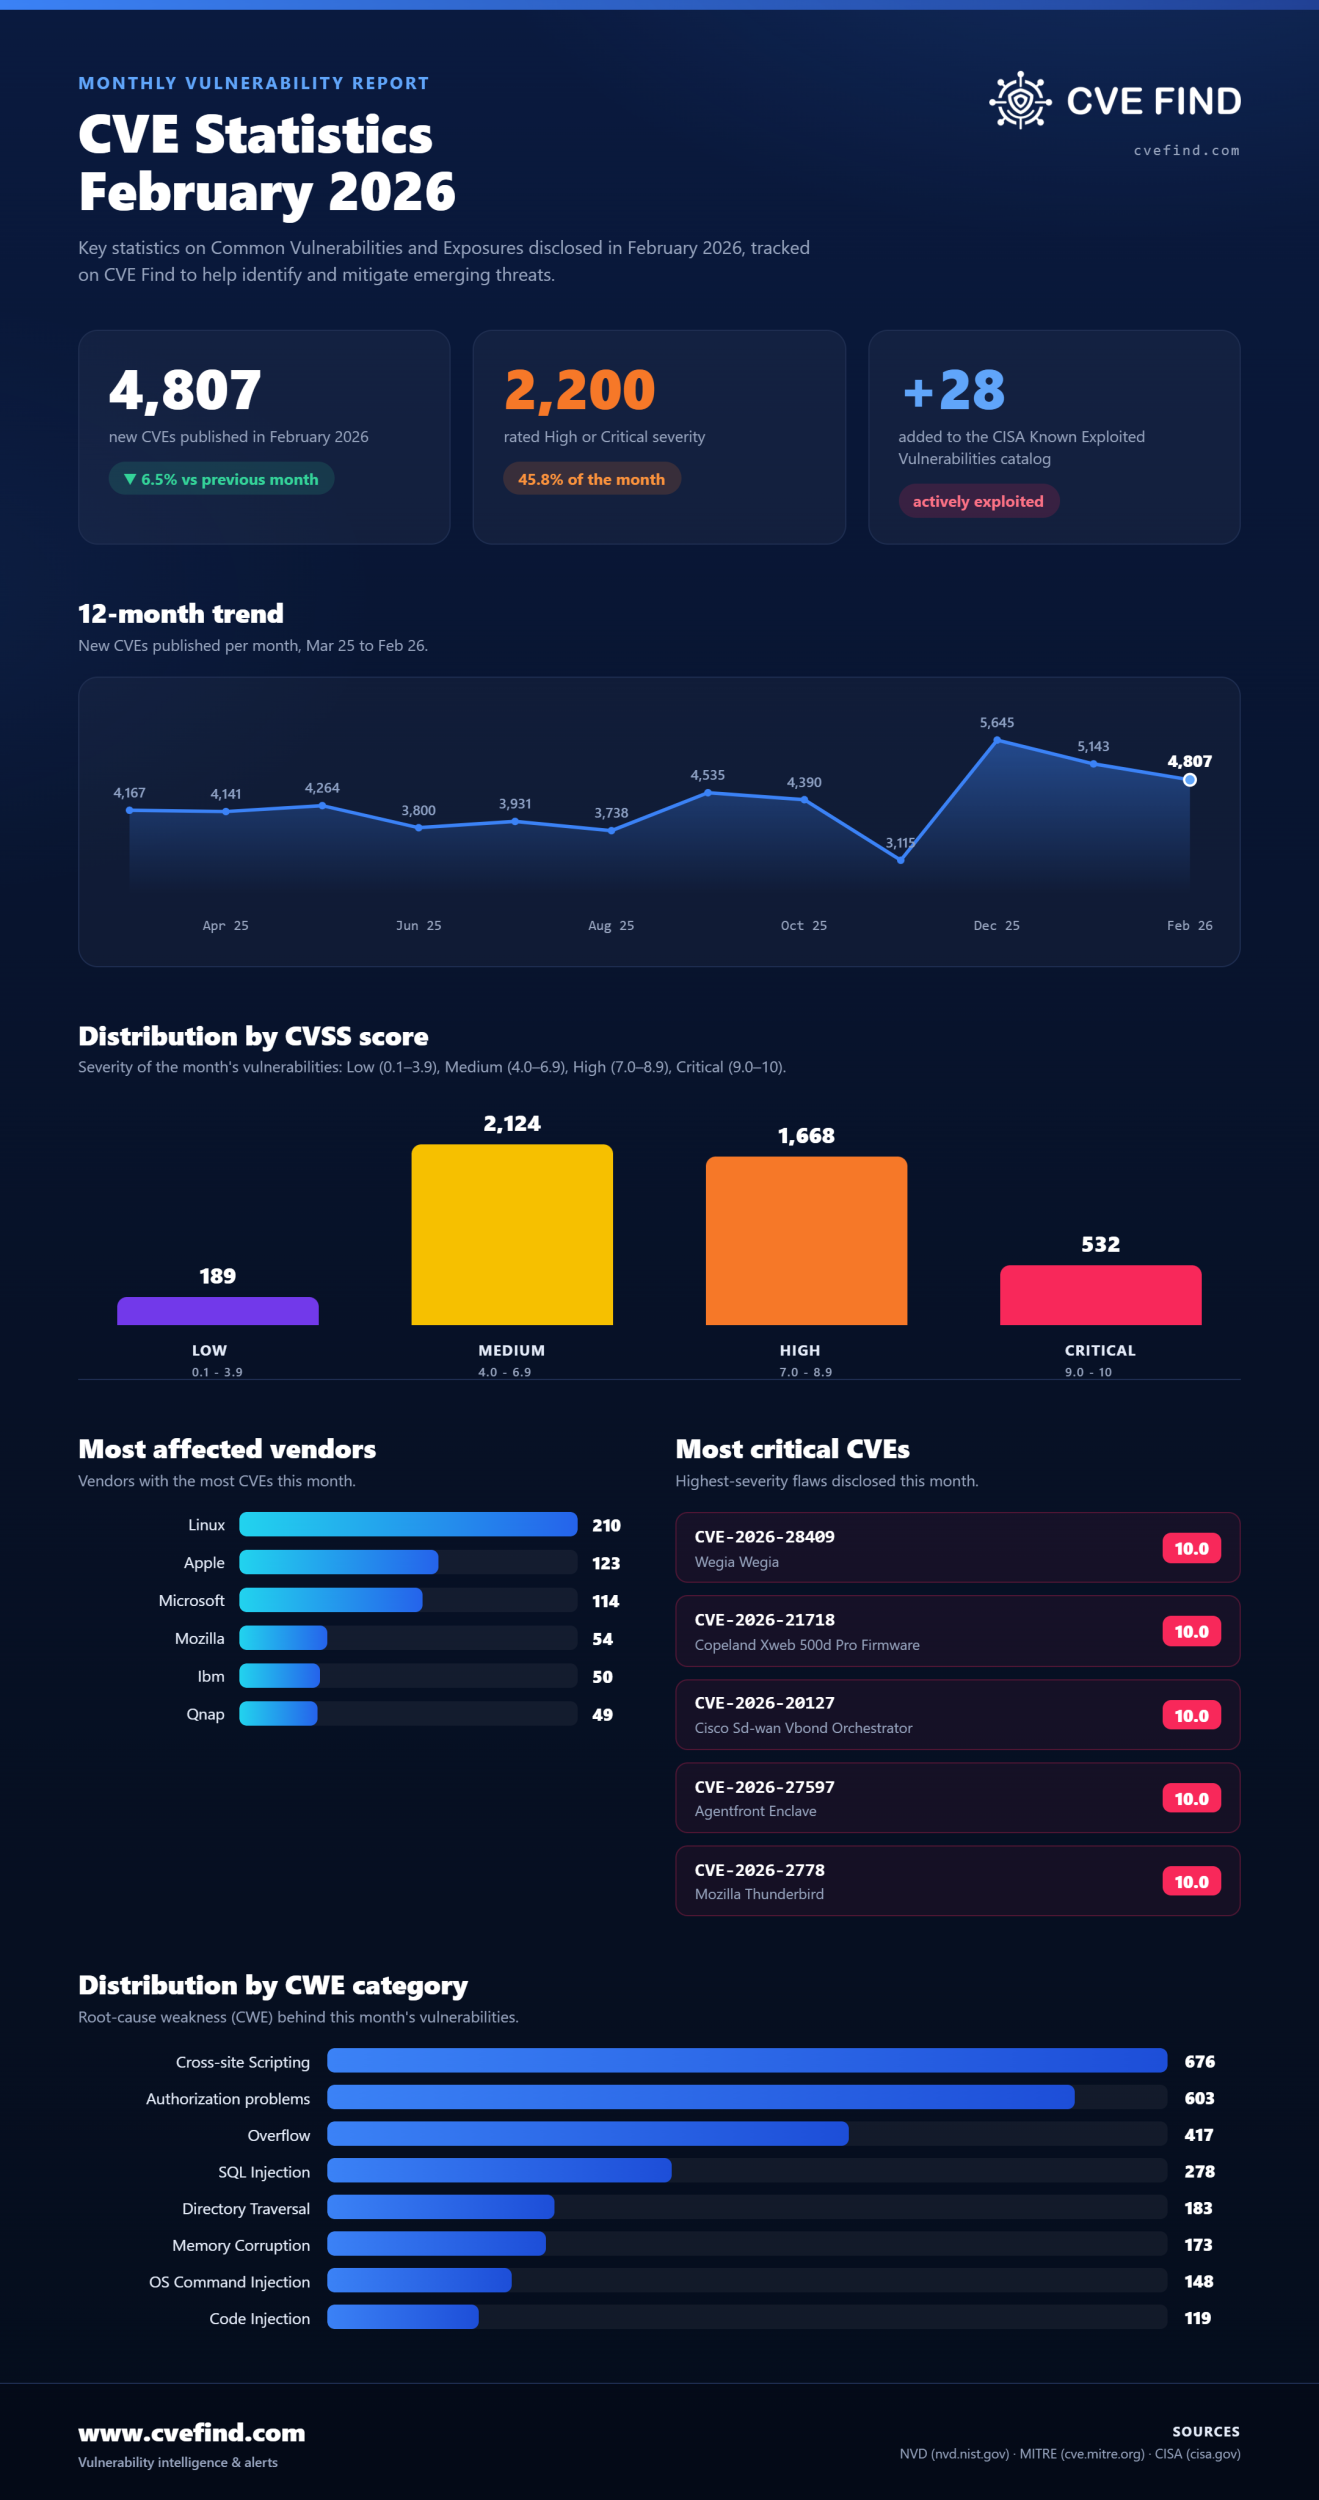
- Numero totale di CVE pubblicate : 4,807 (-6.5% rispetto al mese precedente)
- Vulnerabilità aggiunte al catalogo CISA KEV : 28
📂 Distribuzione per categorie principali
- Cross-site Scripting : 676
- Authorization problems : 603
- Overflow : 417
- SQL Injection : 278
- Directory Traversal : 183
- Memory Corruption : 173
📈 Distribuzione per punteggio CVSS
- Low : 189
- Medium : 2124
- High : 1668
- Critical : 532
🏢 Fornitori più colpiti
📦 Prodotti più colpiti
- linux linux_kernel : 210
- apple macos : 112
- mozilla firefox : 54
- microsoft windows : 53
- mozilla thunderbird : 51
⚠️ CVE rilevanti del mese
- CVE-2026-28409 (10 CRITICAL) : WeGIA is a web manager for charitable institutions. Prior to version 3.6.5, a critical Remote Code Execution (RCE) vulnerability exists in the WeGIA application's database resto...
- CVE-2026-21718 (10 CRITICAL) : An authentication bypass vulnerability exists in Copeland XWEB Pro version 1.12.1 and prior, enabling any attackers to bypass the authentication requirement and achieve pre-au...
- CVE-2026-20127 (10 CRITICAL) : A vulnerability in the peering authentication in Cisco Catalyst SD-WAN Controller, formerly SD-WAN vSmart, Cisco Catalyst SD-WAN Manager, formerly SD-WAN vManage, and Cisco Cata...
- CVE-2026-27597 (10 CRITICAL) : Enclave is a secure JavaScript sandbox designed for safe AI agent code execution. Prior to version 2.11.1, it is possible to escape the security boundraries set by `@enclave-vm/...
- CVE-2026-2778 (10 CRITICAL) : Sandbox escape due to incorrect boundary conditions in the DOM: Core & HTML component. This vulnerability was fixed in Firefox 148, Firefox ESR 115.33, Firefox ESR 140.8, Thunde...
Esplora tutti i dati in dettaglio su CVE Find.
Scoprite come bexxo può proteggere la vostra azienda. Non esitate a contattarci per una consulenza personalizzata oggi stesso!
