CVE Statistics: February 2026
- March 02, 2026
- Temps de lecture: 3 min min
🌐 Discover the key figures for vulnerabilities published in February 2026 on CVE Find.
🔎 Overview
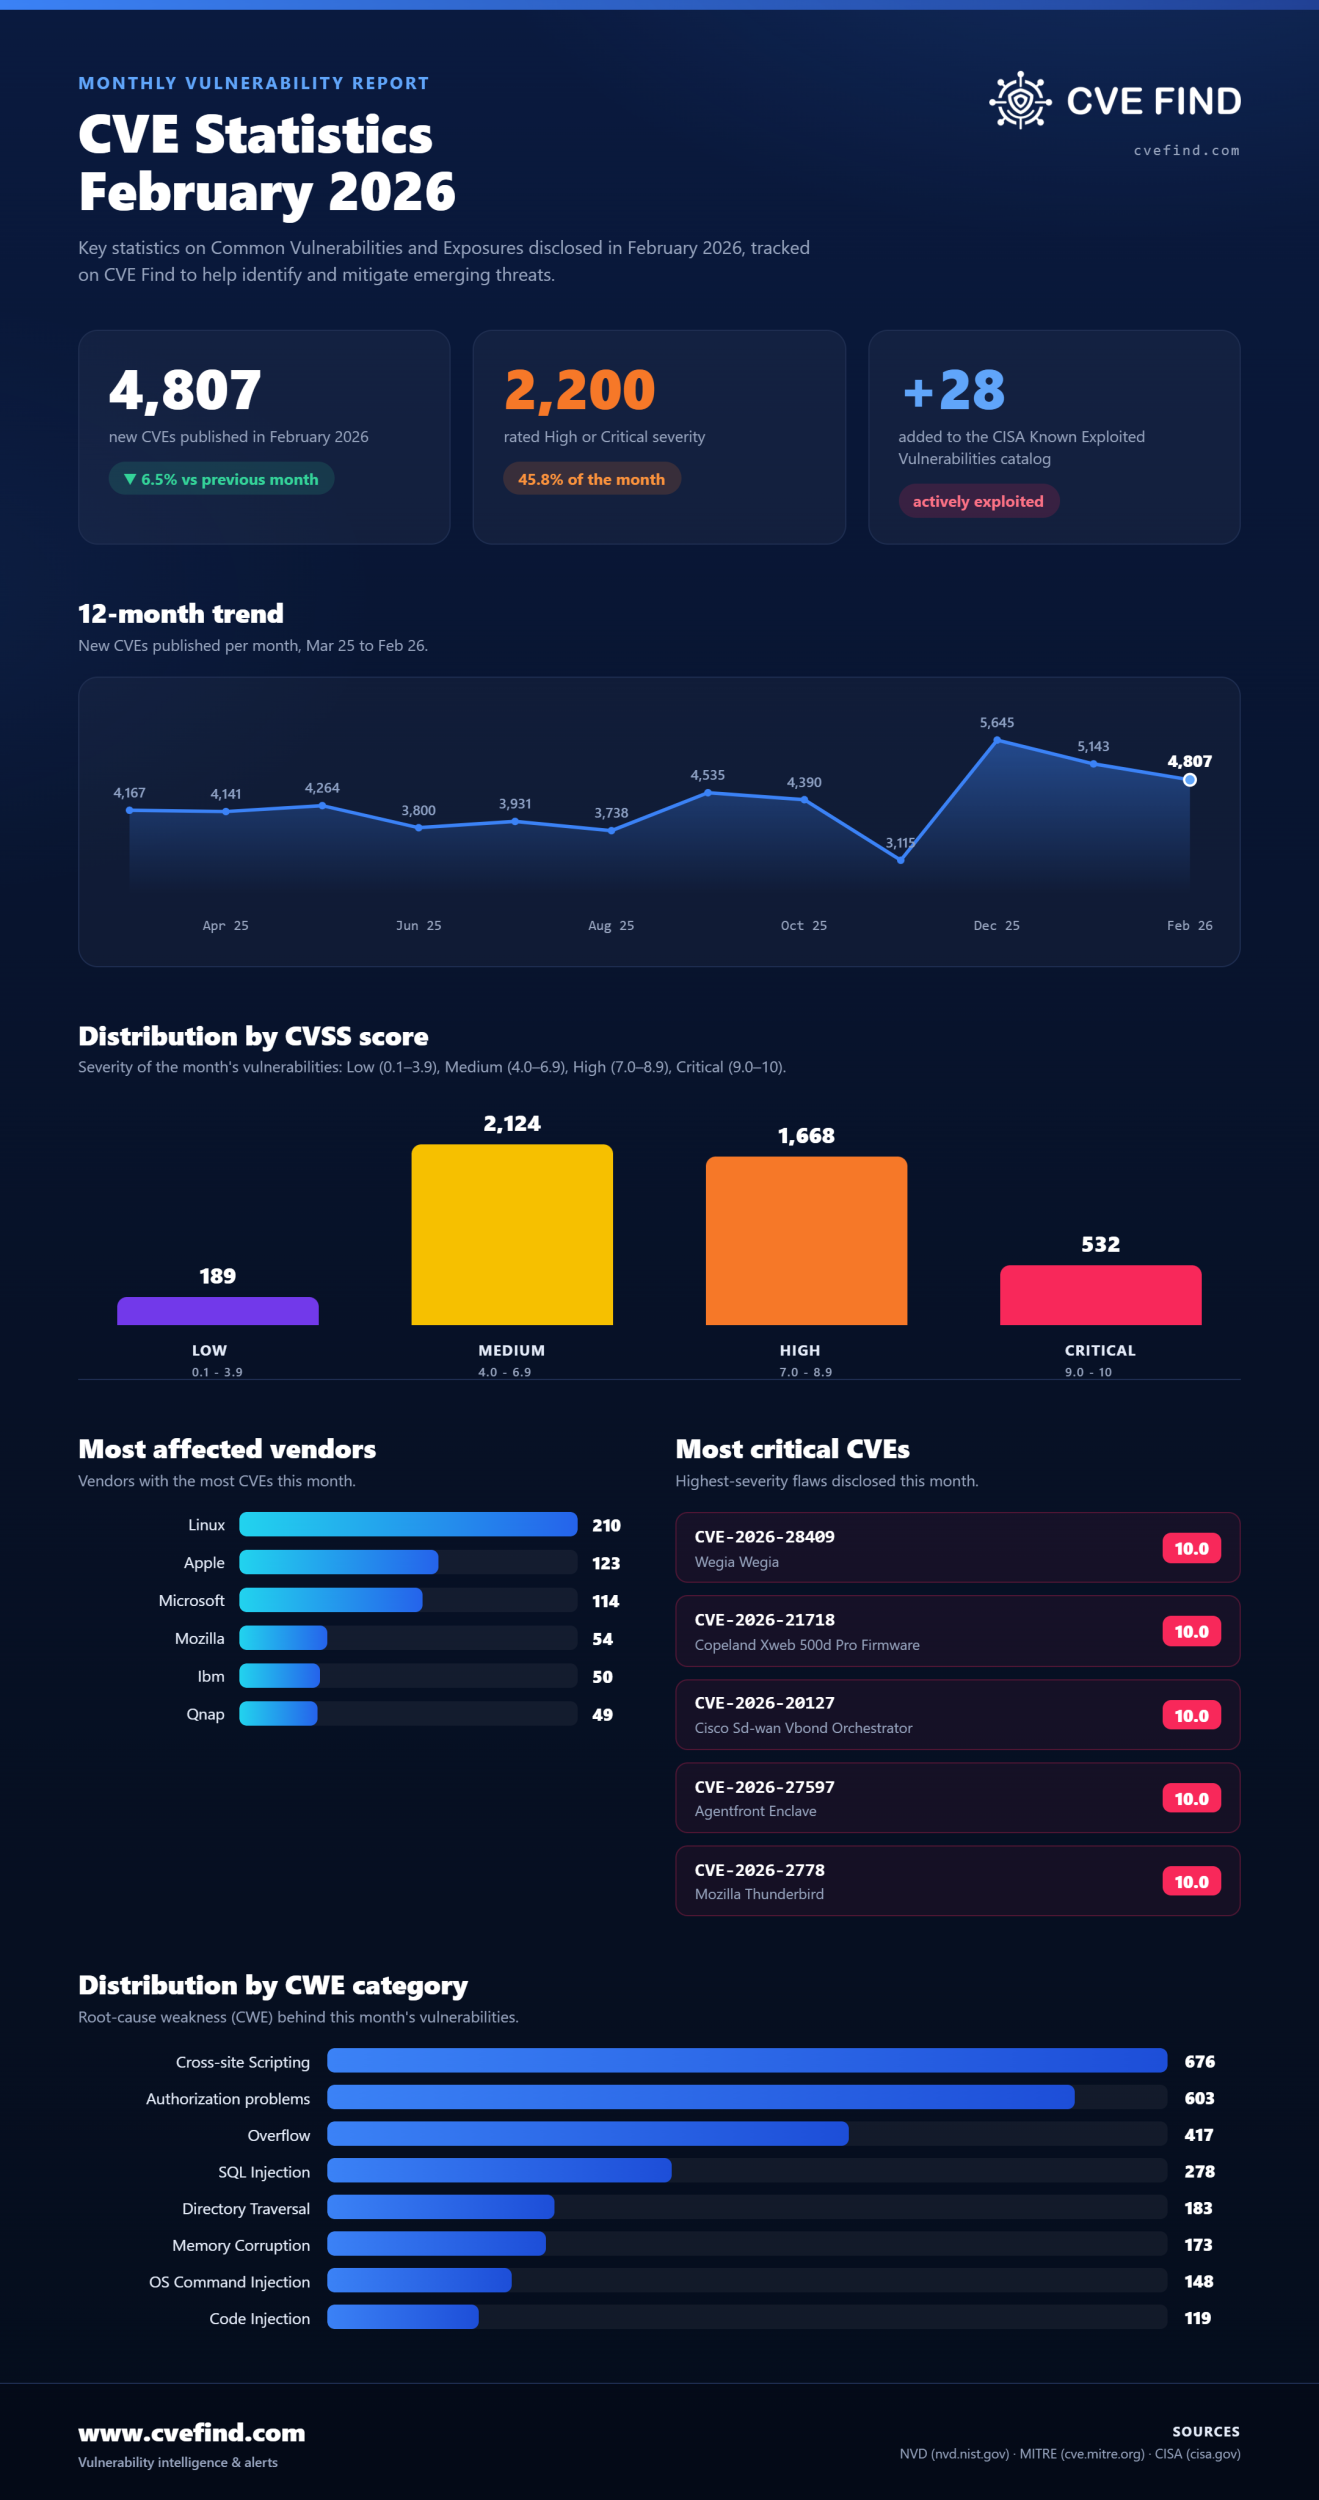
- Total number of CVEs published : 4,807 (-6.5% vs the previous month)
- Vulnerabilities added to the CISA KEV catalog : 28
📂 Breakdown by main categories
- Cross-site Scripting : 676
- Authorization problems : 603
- Overflow : 417
- SQL Injection : 278
- Directory Traversal : 183
- Memory Corruption : 173
📈 Breakdown by CVSS score
- Low : 189
- Medium : 2124
- High : 1668
- Critical : 532
🏢 Most affected vendors
📦 Most affected products
- linux linux_kernel : 210
- apple macos : 112
- mozilla firefox : 54
- microsoft windows : 53
- mozilla thunderbird : 51
⚠️ Notable CVEs of the month
- CVE-2026-28409 (10 CRITICAL) : WeGIA is a web manager for charitable institutions. Prior to version 3.6.5, a critical Remote Code Execution (RCE) vulnerability exists in the WeGIA application's database resto...
- CVE-2026-21718 (10 CRITICAL) : An authentication bypass vulnerability exists in Copeland XWEB Pro version 1.12.1 and prior, enabling any attackers to bypass the authentication requirement and achieve pre-au...
- CVE-2026-20127 (10 CRITICAL) : A vulnerability in the peering authentication in Cisco Catalyst SD-WAN Controller, formerly SD-WAN vSmart, Cisco Catalyst SD-WAN Manager, formerly SD-WAN vManage, and Cisco Cata...
- CVE-2026-27597 (10 CRITICAL) : Enclave is a secure JavaScript sandbox designed for safe AI agent code execution. Prior to version 2.11.1, it is possible to escape the security boundraries set by `@enclave-vm/...
- CVE-2026-2778 (10 CRITICAL) : Sandbox escape due to incorrect boundary conditions in the DOM: Core & HTML component. This vulnerability was fixed in Firefox 148, Firefox ESR 115.33, Firefox ESR 140.8, Thunde...
Explore all the data in detail on CVE Find.
Discover how bexxo can secure your business. Don't hesitate to contact us for a personalized consultation today!
