Articles

- May 18, 2026, Stéphane Chapuis
Ransomware: can you recover your data without paying?
- February 19, 2026, Peter Senn
Quishing: Behind Every QR Code Lies a Decision
Malicious QR codes bypass all your anti-spam filters. Discover how quishing targets your employees and the 5 essential steps to protect your Swiss SME from this rapidly growing threat.
- February 05, 2026, Peter Senn
Shadow IT and Shadow AI: The Invisible Risks Threatening Your SME
Shadow IT refers to the unauthorized use of digital tools within a company — and its variant, Shadow AI, is now one of the main sources of data leaks for Swiss SMEs. Every time an employee copies customer data into ChatGPT or stores files on their personal Dropbox, your sensitive data escapes all control. Discover the concrete risks associated with the revised Federal Act on Data Protection (nLPD) and the American Cloud Act, and the sovereign solutions to regain control without hindering the productivity of your teams.
Complete Shadow IT / Shadow AI guide for Swiss SMEs: nLPD risks, Cloud Act, sovereign solutions (Euria, kDrive, Proton Drive, SwissTransfer) and practical governance.
- January 23, 2026, Peter Senn
Daily Digital Hygiene: 7 Essential Practices for Every Employee in a Swiss SME
- January 13, 2026, Peter Senn
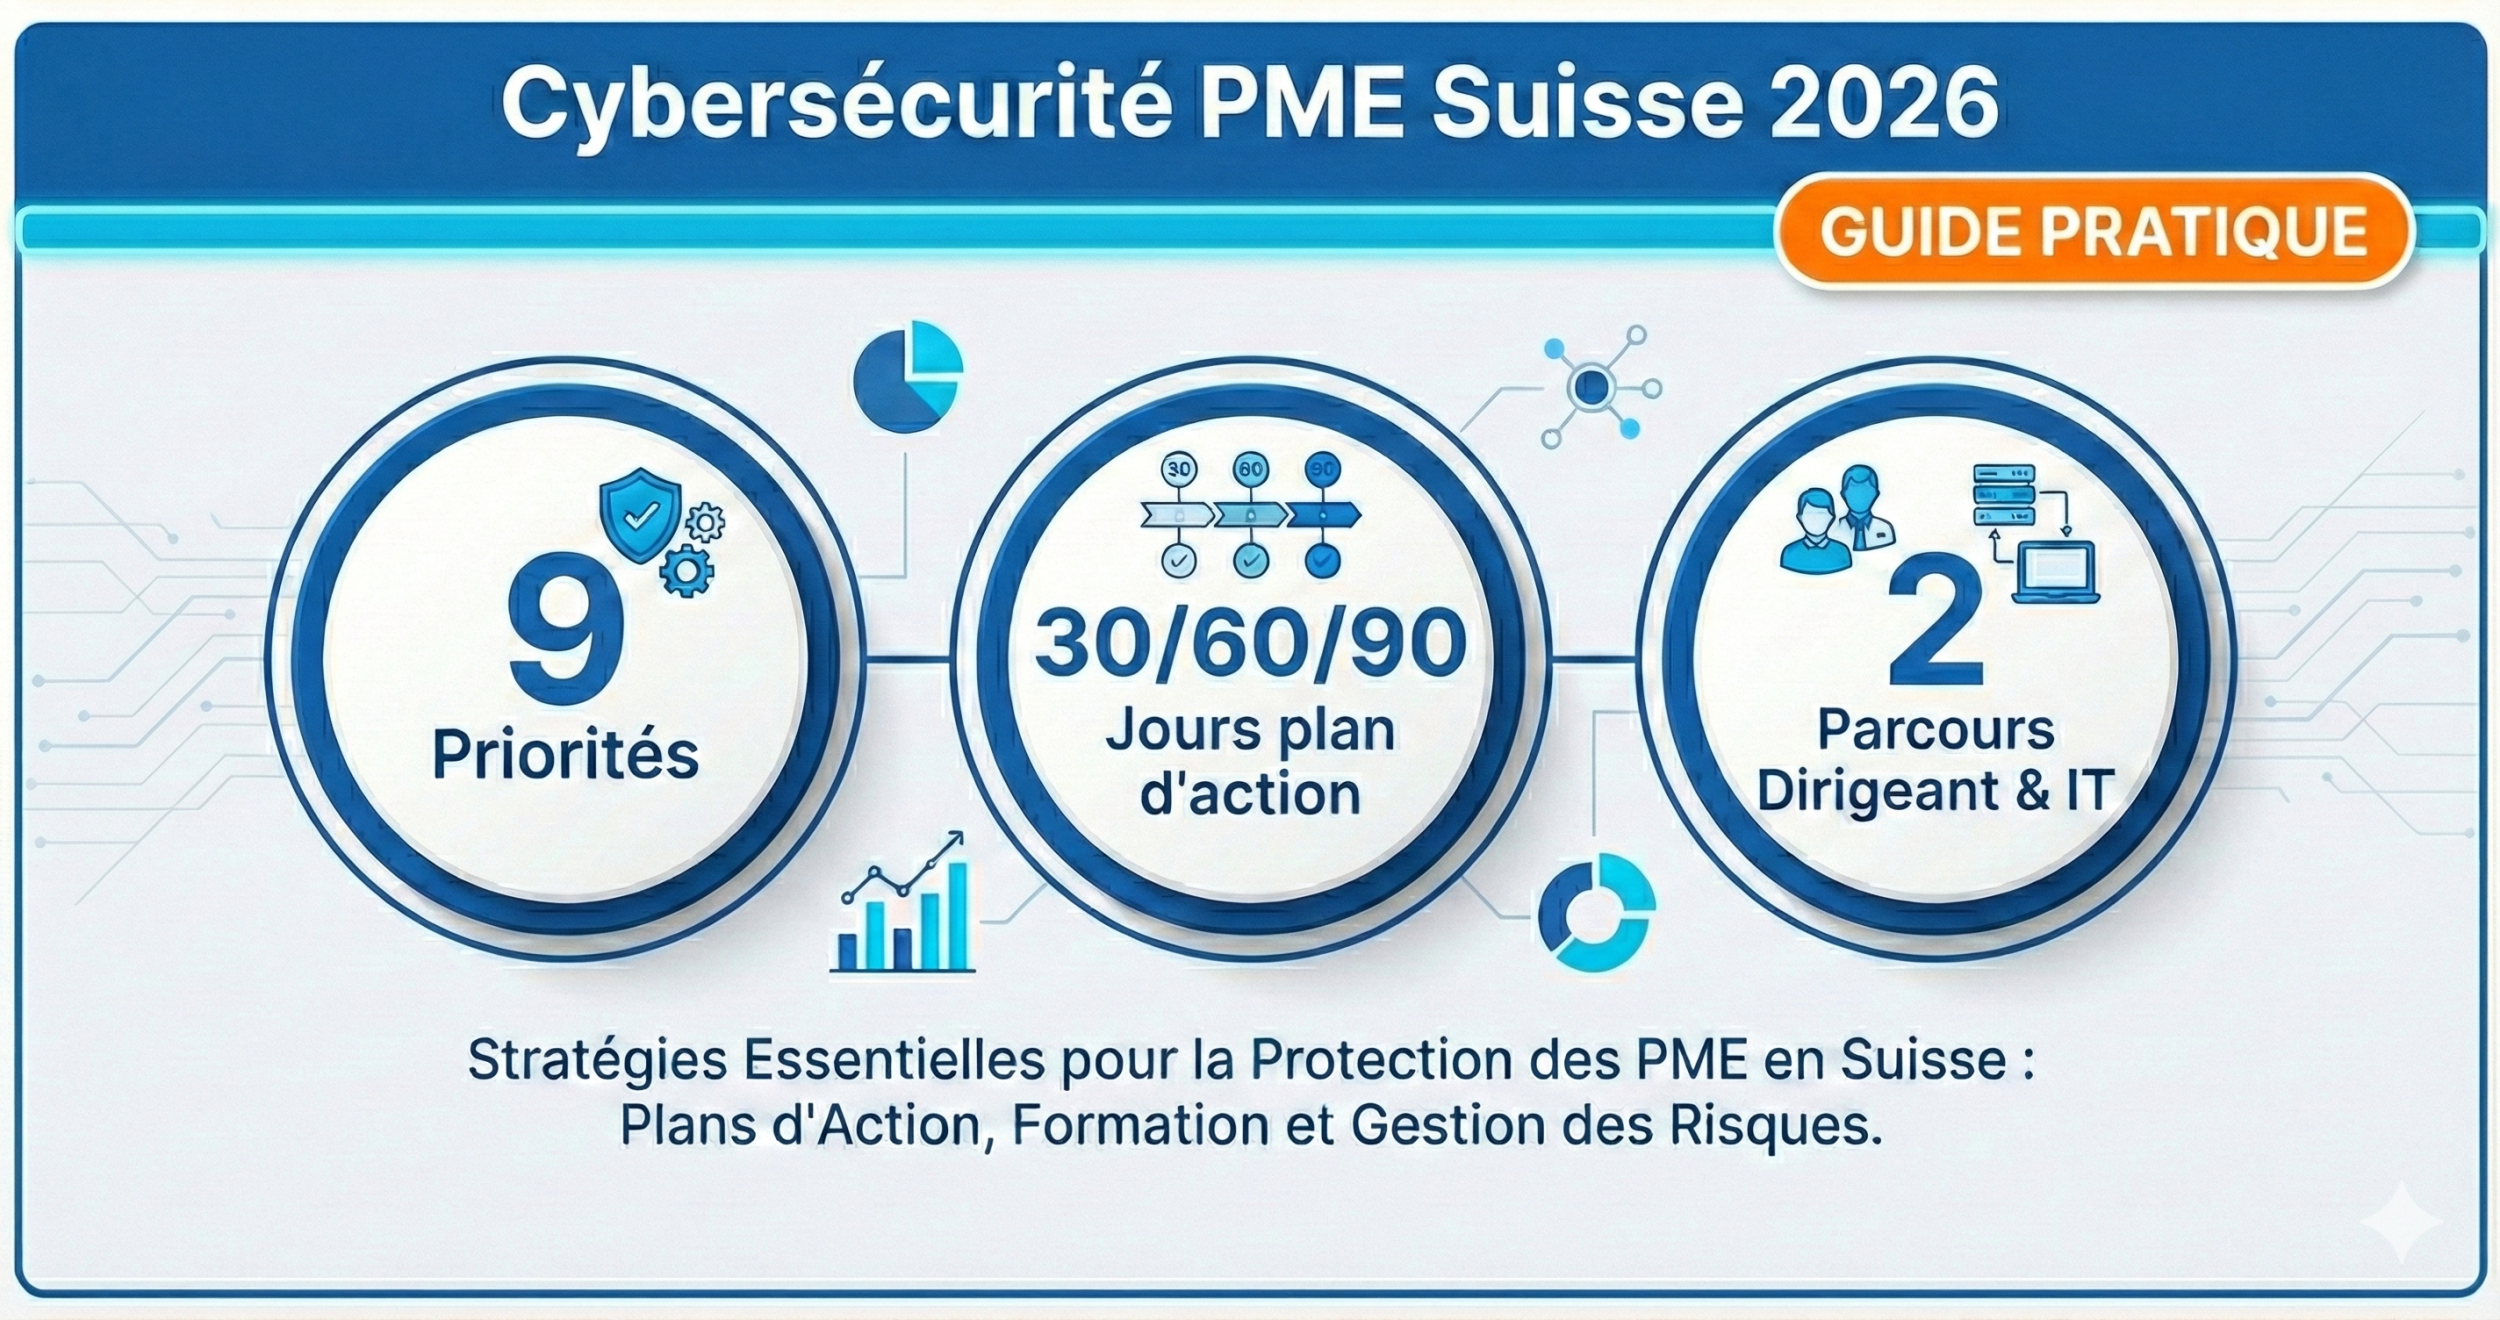
Swiss SME Cybersecurity: 2025 Summary & 30/60/90-Day Action Plan for 2026
The guide that transforms cybersecurity into 9 concrete actions for Swiss SMEs 10-250, with a 30/60/90-day plan adapted for both managers and IT teams (two reading paths).
- December 15, 2025, Peter Senn
Why Swiss SMEs Need to Enable Automatic Updates
Automatic updates are the simplest and most effective cybersecurity measure to protect your Swiss SME: a one-time setup of just a few minutes is enough to block cyberattacks that exploit known vulnerabilities. According to the National Cyber Security Centre (NCSC), 60% of cyber incidents affecting Swiss SMEs exploit unpatched software flaws. Discover how to configure this essential protection without disrupting your daily operations, with solutions tailored to the realities of Swiss SMEs and the requirements of the revised Federal Act on Data Protection (nLPD).
- December 04, 2025, Peter Senn
BYOD in Business: How to Protect Your SME When Employees Use Personal Devices
Do your SME employees use their personal smartphones, tablets, and computers for work? This practice, called BYOD (Bring Your Own Device), offers flexibility and cost savings, but it exposes your company to significant security risks: data loss, nLPD violations, or cyberattacks. This practical guide explains how to effectively manage BYOD with measures accessible to Swiss SMEs: define a clear policy, protect devices, separate professional and personal data, raise awareness among your teams, and prepare a contingency plan. Concrete advice, without technical jargon, to protect your business without overcomplicating things.
- September 10, 2025, Stéphane Chapuis
Secure Password: The Complete Guide to Protecting Your Accounts in 2026
A weak password exposes your accounts, identity, and finances to cyberattacks in seconds. This practical guide explains exactly how to create memorable and unbreakable passwords, enable two-factor authentication, and adopt sustainable digital hygiene — without being a computer expert.
- August 20, 2025, Peter Senn
Public WiFi on the Go: Securing Your Connections to Ensure Business Continuity
Public WiFi exposes Swiss SMEs to cyberattacks that are invisible but very real. Discover 5 concrete measures to protect your business data on the go and maintain business continuity.
- August 15, 2025, Peter Senn
Backup Security Plan for SMEs: Why It's Essential
A backup security plan is a set of documented procedures that ensures the availability, integrity, and rapid restoration of an SME's critical data in the event of an incident. According to the Veeam Data Protection Trends 2024 report, 76% of companies experienced at least one major data-related outage in the past 12 months — and those without a tested backup plan took an average of 3 times longer to resume operations.
For an SME, adopting such a policy protects the company's reputation, ensures regulatory compliance (GDPR, Swiss nLPD which came into force in September 2023), and maintains customer trust. It's a measurable strategic choice: according to Gartner (2023), the average cost of unplanned downtime reaches CHF 8,500 per hour — a risk that a structured plan helps to avoid.
