
Help The platform aideRub_annuaire
Connect the Microsoft Entra ID directory
On this page
Purpose
In Microsoft Entra, you create a group and a read-only application (steps 1 to 4). In the portal, you enter its identifiers and start the synchronisation (step 5): only the organisation's administrator can do this.
The screenshots show the portal in French; the English labels are given in the text.
Prerequisite: in Microsoft Entra ID, the right to create a group and an app registration, and to grant admin consent (Global Administrator role or equivalent).
The requested permissions only allow reading your users and groups: Bexxo cannot modify, create or delete anything in Entra ID.
1Create the synchronisation group
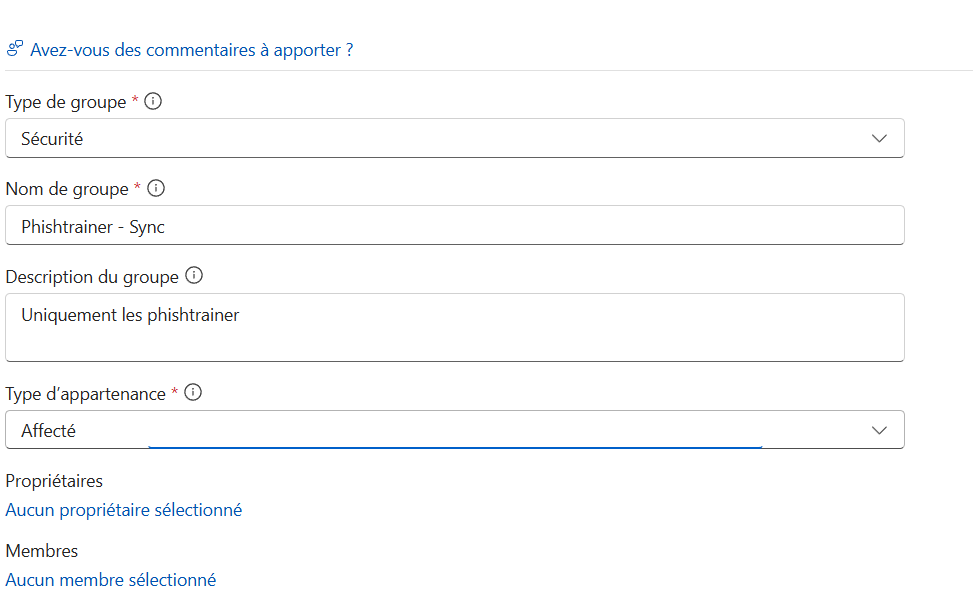
Only the members of this group are synchronised. Afterwards, adding or removing a person from the group is enough to include or exclude them from the next synchronisation. You can create several groups, for example one per department.
- In the Microsoft Entra admin center (entra.microsoft.com), go to Entra ID › Groups › All groups, then click New group.
- Group type: Security; Membership type: Assigned; Group name: a recognisable name, for example
Bexxo - Sync. - Under Members, add the people to synchronise, then create the group.
2Create the application and record its identifiers
- In Entra ID › App registrations, click New registration and name the application, for example
Bexxo - Directory synchronisation. - Supported account types: Single tenant only (Accounts in this organizational directory only in earlier versions of the portal).
- Leave the Redirect URI field empty, then click Register.
The application's Overview page shows two identifiers (GUID) to copy:
| On the Azure page | Field in the portal |
|---|---|
| Application (client) ID | Client ID |
| Directory (tenant) ID | Tenant ID |
3Allow reading of users and groups
- In the application's menu, open API permissions › Add a permission › Microsoft Graph.
- Be sure to choose Application permissions (not “Delegated permissions”).
- Add these two permissions:
| Permission | What it allows |
|---|---|
User.Read.All | Read the list of users (name, email, language, account status…). |
Group.Read.All | Read the groups and the membership of each group. |
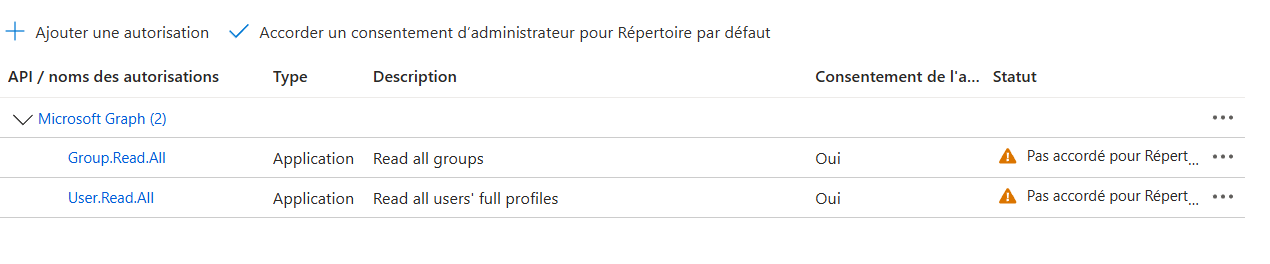
- Click Grant admin consent for [your organisation] and confirm. The status of both permissions must change to “Granted” (if needed, click Refresh).

Essential step: without this consent, the synchronisation fails with a permissions error.
4Create a client secret
- In Certificates & secrets › Client secrets, click New client secret.
- Expiration: according to your policy (Microsoft recommends less than 12 months, 24 at most). Note the date: the secret must be renewed before then.
- Click Add and immediately copy the Value.
Copy the Value column, not “Secret ID”. It is displayed only once: if you do not copy it, you have to create a new secret.
5Connect the directory in the portal
- In My organization › Directory and SSO, add a Microsoft Entra ID directory. In the Connection section, enter the tenant ID, the client ID and the secret value, then save.
- Test the connection. If it fails, check the admin consent first (step 3).
- In Imported groups, add the group from step 1 and save: without a group, the whole directory is imported.
- Set the people's permissions and the frequency. Automatic synchronisation only runs if Import active is ticked and the frequency is not Manual.
- Preview, check the result, then synchronise: the sign-in accounts are created and each new account receives an invitation.
Filters are optional and the field matching is prefilled. For people to sign in with their Microsoft account, also fill in SSO sign-in.
Encryption active: the vault must be unlocked to enter these settings, and your Bexxo Protected agent is the one that queries the directory.
After go-live
- Renew the secret: before it expires, create a new one (step 4), enter it in Connection and save.
- Least privilege: do not add any permission besides
User.Read.AllandGroup.Read.All.
Procedure created from the Microsoft documentation: Register an application with the Microsoft identity platform.
Didn’t find the answer? Contact us